Assumed Breach - A Better Model for Penetration Testing
Explore advanced penetration testing techniques using the Assumed Breach model, focusing on real-world tactics, domain fronting, and lateral movement strategies.
Adversarial Emulation
Explore adversarial emulation techniques, communication protocols, and defense validation strategies for effective red team operations and cybersecurity enhancement.
Investigating Windows Subsystem for Linux - WSL Endpoints
Explore forensic artifacts and investigation techniques for compromised Windows Subsystem for Linux (WSL) endpoints, covering attacker techniques and architectural changes relevant to digital forensics professionals.
I Know What Your AD Did Last Summer - Talks About Active Directory
Explore Active Directory security, lateral movement, and privilege escalation techniques. Learn forensic approaches for investigating AD incidents using open-source tools, with insights for both red and blue teams.
How I Would Attack SQL Server
Explore SQL Server vulnerabilities and attack strategies from an adversary's perspective, learning detection, prevention, and response techniques for enhanced database security.
Nakatomi Space - Lateral Movement as L1 Post-exploitation in OT
Exploring deep lateral movement in OT networks, focusing on TTPs for navigating through embedded device networks at the lowest levels, highlighting security vulnerabilities in industrial control systems.
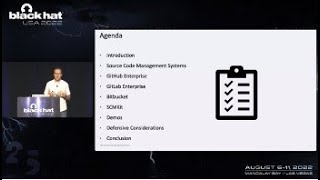
Controlling the Source - Abusing Source Code Management Systems
Explore vulnerabilities in Source Code Management systems, including reconnaissance, user role manipulation, and repository takeover. Learn attack scenarios and defensive strategies for GitHub, GitLab, and Bitbucket.
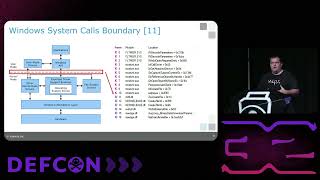
Defeating EDR Evading Malware with Memory Forensics
Discover advanced memory forensics techniques to detect and analyze EDR-evading malware, including system call manipulation, module overwriting, and debug register abuse.
A Decade of Active Directory Attacks: What We've Learned and What's Next
Explore a decade of Active Directory attacks, lessons learned, and future trends in this insightful IT security talk by Sean Metcalf at TROOPERS24 conference.

Black Hat USA 2025
Black Hat USA 2025

Black Hat Europe 2023
Black Hat Europe 2023

Black Hat Asia 2025
Black Hat Asia 2025

Black Hat Europe 2022
Black Hat Europe 2022