Data Protection at AWS - Securing Cloud Applications
Discover essential strategies for securing AWS-based applications, including network protection, encryption, key management, and storage architecture. Learn from real-life examples to avoid common pitfalls and ensure data safety.
Implementing Android Tamper-Resistant Secure Storage in Virtualization
Explore Android's tamper-resistant secure storage implementation, including RPMB key generation, factory provisioning, and virtualization in ACRN hypervisor for multiple Linux guests and TEE instances.
Better Protect Sensitive Data in the Cloud with Client-Side Application Layer Encryption
Learn to implement client-side application layer encryption for enhanced data protection in cloud environments, reducing breach risks and maintaining control over sensitive information.
Security on Android - What's Next
Explore Android security features, new APIs, and best practices for app integrity and data privacy. Learn about encryption, key management, user authentication, and transparency layers.
Keeping Your Java Applications Secure - Cryptographic Improvements and Best Practices
Explore Java's cryptographic enhancements and secure coding practices to develop robust applications with strong security capabilities and protection against vulnerabilities.
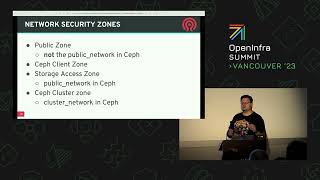
Data Security and Storage Hardening in Rook and Ceph
Explore comprehensive security strategies for Ceph storage systems, from threat modeling and encryption to access controls, focusing on practical hardening techniques for robust data protection.
Threshold Cryptosystems From Threshold Fully Homomorphic Encryption
Explore threshold cryptosystems derived from threshold fully homomorphic encryption, covering key management, signatures, and public key encryption, with insights on security definitions and techniques.
Building End-to-End Encryption and User Identity for Video Conferencing - Zoom's Approach
Exploring Zoom's approach to end-to-end encryption and user identity in video conferencing, focusing on security, trust, and user-friendly implementation in a remote-first world.
Public Key Methods
Learn about public key cryptography, including RSA, ECC, and ElGamal. Explore their workings, applications, and future challenges in the post-quantum era.
E-Security - Key Exchange
Explore key exchange methods, including Diffie-Hellman and elliptic curve cryptography, for secure communication and forward secrecy in modern applications.
Sigstore - How We Learned to Stop Trusting Registries and Love Signatures
Explore InfluxData's journey in implementing container image signing for their SaaS offering, covering the process, challenges, and technical details from DevOps and security perspectives.
Establishing Trust in Linux Keyrings - Built-in, Imputed, or Transitive Trust
Explore Linux keyrings, trust models, and key management in firmware, kernel, and user space. Learn about trust domains, scope, usage constraints, and security implications for different systems.
Zero Knowledge Proofs, Oblivious Transfer, and Key Management - Session 20
Explore zero knowledge proofs, oblivious transfer, and key management techniques in cryptography. Gain insights into advanced security protocols and their applications.
Designing, Implementing, Attacking, and Defending Symmetric Crypto
Explore symmetric cryptography design, implementation, attacks, and defense strategies in this comprehensive overview of modern encryption techniques and security challenges.
Extending OpenPOWER Boot Security to Guests
Explore secure boot design for KVM and PowerVM guests on OpenPOWER, addressing unique challenges and leveraging open source solutions to enhance OS boot security.
Installing Hardware Wallet for Consortium Blockchain - Protecting Hyperledger Fabric Node Private Keys with Intel SGX
Learn to protect Hyperledger Fabric node private keys using Intel SGX technology. Explore modifications to Golang encryption library, bridging Fabric and Enclave, and implementing plugin bccsp in BaaS scenarios.
OpenPOWER Host OS Secure Boot Key Management
Explore OpenPOWER's flexible key management for Linux-based secure boot, covering architecture, ownership, updates, storage, and compatibility across firmware, kernel, and userspace.
Barbican - Protecting Secrets at Scale for Cloud Infrastructure
Explore Barbican, an open-source key management solution for secure, scalable infrastructure. Learn its architecture, usage as internal/cloud service, and see a proof-of-concept demo.
Fooling an Unbounded Adversary with a Short Key, Repeatedly - The Honey Encryption Perspective
Explores honey encryption for unconditional security with short keys, presenting a new scheme for semantic security in the standard model and enabling multiple message encryption with a single key.
Data as a New Security Boundary - Cryptography and Supporting Controls
Explore data security through cryptography as a boundary, covering end-to-end encryption, application-level protection, and supporting controls for real-world implementation across various contexts.
Using Hardware Protected Keys with the Linux Crypto API
Learn to use hardware-protected keys with Linux Crypto API for enhanced security in embedded systems. Explore implementation, benefits, and potential challenges in this in-depth presentation.