Learning JavaScript for Hacking - Interview with Filedescriptor
Explore JavaScript for hacking, reconless techniques, and Twitter vulnerabilities with expert insights on enhancing cybersecurity skills and ethical hacking practices.

How to Use Broadcasting in Laravel - What Is Broadcasting in Laravel
Learn to implement real-time event sharing between server-side Laravel and client-side JavaScript using broadcasting, with step-by-step guidance on setup, configuration, and practical implementation.
Browser Exploitation - Max Zinkus
Explore JavaScript-based browser exploitation techniques, including XSS, JIT compilation vulnerabilities, and shellcode execution. Learn about browser security measures and how to find and chain exploits.
Introduction to Ransomware and Obfuscation
Learn about ransomware's history, types, and techniques. Explore obfuscation methods, analyze real-world examples, and understand the evolving landscape of cyber threats.

How to Hide Your API Keys Safely When Using React
Learn to securely store API keys for React projects by building a mini backend with Node.js, enhancing the security of your applications while working with sensitive data.
How to Bypass Sophisticated Anti-Bot Systems
Learn techniques to bypass advanced anti-bot systems, enhancing your understanding of web security and automation challenges in modern web development.
Embedded Malicious JavaScript - Outerz0ne 2009
Explore techniques for embedding malicious JavaScript in web applications, understanding potential vulnerabilities and security risks in modern web development.
LininoOS, LininoIO and ArduinoOS - A Suitable Ecosystem for Linux and MCUs
Explore LininoOS, LininoIO, and ArduinoOS: an integrated ecosystem for IoT development combining Linux and microcontrollers. Learn about package management, GPIO control, and graphical interfaces for embedded systems.
Preventing Common Security Mistakes in the MEAN Stack - AppSec EU 2017
Learn to secure Angular applications by understanding common threats and implementing effective defenses. Covers script-based attacks, session management, CSRF, and more for robust client-side security.
Combining Security Risks of Native and Web Development in Hybrid Apps - AppSec EU 2017
Explore security risks in hybrid app development, combining native and web technologies. Learn defensive programming and testing strategies for secure cross-platform mobile applications.
Securing Single Page Applications - Design Considerations and Pitfalls
Explore security pitfalls in Single Page Applications and learn mitigation strategies. Covers stateless design, JSON handling, caching, local storage, and resource sharing, with practical demos and key takeaways.
SPArring with the Security of Single Page Applications
Explore security challenges in Single Page Applications with insights on automating detection and mitigation strategies for modern web development vulnerabilities.
Modern XSS Defense Strategies - Frameworks, CSP, and Sanitization
Explore modern XSS defense strategies, including JavaScript frameworks, CSP deployment, HTML sanitization, and design considerations for building secure web applications against evolving threats.
SPArring with the Security of Single Page Applications - MMA Hacker Training
Explore security challenges in Single Page Applications through an MMA analogy. Learn about SPA frameworks, REST APIs, WebSockets, and interconnectivity to become a "Mixed Multilayer Application Hacker".
Security Testing Windows Store Apps
Explore security testing for Windows Store Apps, focusing on HTML/JavaScript development, architecture, and potential vulnerabilities in this emerging application model.
Blended Web and Database Attacks on Real-time, In-Memory Platforms
Explore blended web and database attacks on real-time, in-memory platforms, focusing on SAP HANA. Learn about novel exploit techniques, vulnerabilities, and security considerations for these high-performance systems.
New Frameworks, Old Problems: Web Security Challenges in Modern Development
Exploring security challenges in modern web frameworks like Play! and Node.js, comparing solutions from established frameworks, and offering practical code examples to address common vulnerabilities.
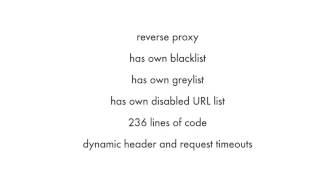
Surviving an Application DoS - Strategies and Open Source Defense Framework
Explore strategies to defend against Application-Level DoS attacks using a new open-source Node.js framework. Learn to identify threats, analyze traffic patterns, and implement active defense measures.
Improving Package Repository Security - From White Papers to Practice
Explore package repository security challenges, modern practices, and collaborative solutions for improving community repositories like PyPI and NPM.
Building an Accessible Custom Feedback Widget - Learn With Jason
Learn to create an accessible feedback widget using React, exploring CSS techniques, React Hooks, and best practices for community engagement and documentation improvement.
Adding Authentication to Apps with Okta - Learn With Jason
Implement user authentication in Gatsby apps using Okta. Learn to set up secure user accounts, integrate sign-in widgets, and manage JSON Web Tokens for enhanced app functionality.