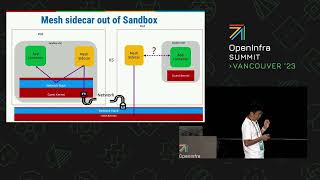
Towards Kata Containers 4 - When Kata Containers Meet Service Mesh
Explore security challenges and solutions for Kata Containers in service mesh environments, focusing on threat models, infrastructure sidecar designs, and performance benchmarks.
Optimizing Secrets Management - From Integration to Deletion
Improve secrets management lifecycle: integration, creation, rotation, and deletion. Learn strategies for enhancing security and efficiency in handling sensitive information.
Kubernetes Misconfigurations - What They Are and How to Identify Them
Explore common Kubernetes misconfigurations, their potential risks, and effective identification techniques to enhance cluster security and performance.
Foster Secure Innovation with Your Kubernetes Platform
Explore comprehensive security strategies for Kubernetes, covering infrastructure protection, supply chain security, and runtime safeguards in mission-critical cloud-native environments.
Securing Access to Kubernetes Infrastructure with Zero Trust Principles
Learn how to apply zero trust principles to secure access to Kubernetes infrastructure across multiple environments, ensuring controlled and audited cluster access for various teams and systems.

Flawed ML Security: Mitigating Security Vulnerabilities in Data and Machine Learning Infrastructure with MLSecOps
Explore security vulnerabilities in machine learning infrastructure and learn practical strategies for mitigating risks using MLSecOps. Gain insights on RBAC, encryption, and best practices for robust ML systems.
Interactive Playground to Learn Kubernetes and Cloud Native Security
Explore Kubernetes security through hands-on scenarios in a vulnerable cluster environment. Learn about real-world vulnerabilities, CVEs, and security tools across infrastructure, supply chain, and runtime layers.
GitOps and CI/CD: Maintaining Security in the Age of Automation
Explore best practices for securing GitOps and CI/CD pipelines, covering access control, communication, testing, secrets management, and monitoring. Learn from Red Hat's SRE experiences to enhance your pipeline security.
OWASP Docker Top 10 Security Risks
Explore critical security risks in Docker environments and learn essential mitigation strategies to protect containerized applications from vulnerabilities.
Getting Started with Bite-Size Otterize
Learn to secure services in your cluster incrementally with Bite Size Otterize, avoiding large-scale network policy projects and enhancing infrastructure protection.
Securing the Container Pipeline at Salesforce - Docker Use Case
Securing Docker containers at Salesforce: infrastructure, pipeline security, monitoring, forensics, and automation for rapid containerization while maintaining data sensitivity and customer trust.
Secure Substrate: Least Privilege Container Deployment
Explore Docker's approach to secure container deployment using least privilege principles, focusing on preventing privilege escalation and unauthorized access in distributed systems.
Authorization in Software - How Box Does Authorization
Explore Box's multi-layered approach to authorization, covering security challenges, user permissions, and API access in file-sharing and collaboration platforms.
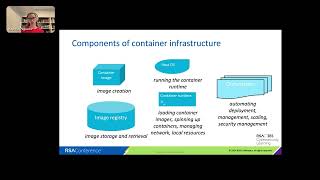
Finding Your Way in Container Security
Explore container security essentials, terminology, and actionable advice for securing containerized applications. Learn how to adapt your application security knowledge to modern deployment methods.
Securing the Kubernetes Empire with OpenPolicyAgent and Rego
Explore OpenPolicyAgent and Rego for robust Kubernetes security. Learn to create, implement, and manage policies efficiently, ensuring compliance and fortifying your cloud-native infrastructure.
OIDC and CI/CD: Reducing Security Threats in Your CI Pipeline
Explore CI/CD security risks and learn strategies to reduce attack surfaces using OIDC, proper branch permissions, and credential management for enhanced supply chain protection.
Cert-Manager's Stamped Certificates - From Concept to KubeCon Swag
Explore cert-manager's journey, from KubeCon swag to securing global infrastructure. Learn about X.509 certificates, local Kubernetes clusters, and the technology behind cryptographic signatures.
The Art of Kubernetes Add-on Validation - Secure Strategies for Modern Developer Platforms
Explore advanced techniques for validating and deploying Kubernetes add-on upgrades securely across cluster fleets, focusing on infrastructure security and streamlined operational workflows.
Security Showdown: The Overconfident Operator vs the Nefarious Ne'er-Do-Well
Playful demo showcasing cloud-native security concepts through characters Ozzie and Nova, exploring vulnerabilities and proactive measures for robust cluster protection.
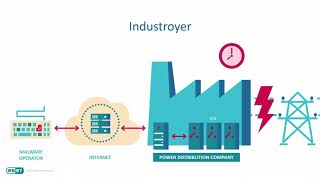
Industroyer - Biggest Threat to Industrial Control Systems Since Stuxnet
Análisis del malware Industroyer, diseñado para atacar redes eléctricas. Se explora su funcionamiento, impacto en Ucrania y potenciales amenazas globales para infraestructuras críticas.
0Day Up Your Sleeve - Attacking macOS Environments
Comprehensive guide to macOS security vulnerabilities, including live demonstration of 0-day exploit, post-exploitation techniques, and hardening recommendations for Mac infrastructures.