Choosing an Infrastructure as Code Solution - Lecture
Explore infrastructure as code solutions, comparing declarative and imperative approaches, authoring experiences, and execution tools to make informed decisions for your DevOps practices.
Configuration Management Tools and Techniques - Puppet, Rudder, Nix, CUE, and Web-Scale
Explore diverse configuration management tools and techniques, from Puppet's versatility to Rudder's user insights, Nix's unique approach, CUE-Terraform integration, and web-scale considerations.
How to Write Pulumi and OpenTofu Providers for Infrastructure as Code - Lecture
Dive into writing and maintaining Pulumi and OpenTofu providers, extending existing ones, and exploring the future of IaC tool integration with cloud systems.
Implementing Configuration Management Primitives in 2024
Explore modern configuration management primitives, focusing on observability, auditing, and security in evolving IT landscapes.
Everything You Need to Know About OpenTofu
Explore OpenTofu's evolution, exclusive features, and project progress with core contributor Sebastian Stadil, followed by a community Q&A.
Crossplane 101 - From Declarative Dreams to Infrastructure Realities
Explore Crossplane's power in extending Kubernetes for infrastructure management, focusing on declarative state and continuous reconciliation.
Seamless Infrastructure Deployment and Management with Terraform
Deploy and manage infrastructure efficiently using Terraform on Google Cloud. Learn best practices, explore Jump Start Solutions, and discover collaboration between Google Cloud and HashiCorp.
Scale Infrastructure as Code: Proven Strategies and Productive Workflows
Discover proven strategies for scalable infrastructure using HashiCorp Terraform. Explore project structuring, global system architecture, secure data sharing, and developer-friendly workflows.
Use Ansible with Ubuntu WSL
Explore Ansible automation on Ubuntu WSL for efficient system management and configuration in Windows environments.
Security Testing for Terraform Templates (IaC) - DevOps and Cloud Security
Learn security testing techniques for Terraform templates, challenging the notion that DevOps neglects security. Explore best practices for integrating security into Infrastructure as Code.
Policy as Versioned Code - Managing Organizational Policies with Software Development Practices
Implement versioned policy management using software development patterns for faster updates, easier compliance measurement, and risk mitigation that keeps pace with evolving threats.
Securing Access to Kubernetes Clusters on AWS
Learn strategies and best practices for securing Kubernetes clusters on AWS, focusing on access control and protection of cloud workloads.
Terraform Best Practices - Modules and Infrastructure as Code
Master Terraform modules and best practices for efficient infrastructure as code automation and management.
Policy as Code: Embracing Continuous Policy Management
Explore continuous policy management using software development patterns to mitigate risks, update policies efficiently, and measure compliance effectively.
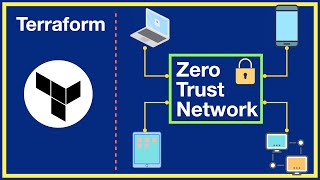
How to Automate Zero Trust: Step-by-Step Twingate and Terraform Guide
Automate Zero Trust implementation using Twingate and Terraform on AWS. Learn to set up secure remote access, configure resources, and test connectivity from mobile and laptop to EC2 instances.
AWS S3 and Terraform Guide - Part 23: Advanced S3 Features
Master AWS S3 with Terraform: Create buckets, upload objects, encrypt data, set IAM policies, enable versioning, configure lifecycle rules, set up logging, and implement object lock for robust cloud storage management.
Terraform: Stand Up Test Environments Fast with AWS
Learn to rapidly deploy test environments on AWS using Terraform. Explore GitLab repos, CloudWatch alerts, S3 buckets, Lambda functions, and ECS deployment pipelines for efficient proof-of-concept testing.
Managing Infrastructure as Code at Scale With env0
Explore common IaC challenges and learn how env0 simplifies infrastructure automation through a hands-on demonstration of managing Infrastructure as Code at scale.
The Evolution of Infrastructure from Code to Infrastructure Plus Code
Explore cloud development evolution, from Infrastructure as Code to integrated approaches. Discover how CDK and Wing bridge infrastructure and application development, addressing cloud adoption challenges.
[Portuguese] Habilite Plataformas de Desenvolvedores Seguras com Backstage, Vault e Terraform
Aprenda a criar plataformas de desenvolvimento seguras e eficientes usando Backstage, Vault e Terraform. Melhore a experiência do desenvolvedor e escale DevOps em sua organização.
FinOps and Observability: Technical Implementation
Explore technical implementation of FinOps and observability for managing cloud infrastructure costs in large enterprises. Learn architecture details and Terraform-based solutions.