Owning the Data Center Using Cisco NX-OS
Explore vulnerabilities in Cisco NX-OS, including hidden strings, GDB usage, and potential exploits. Learn about security risks and implications for data center management.
Corporate Espionage via Mobile Compromise - A Technical Deep Dive
Explore corporate espionage via mobile compromise, including real-world examples, kill chain analysis, and demonstrations of exploits targeting PowerShell and Linux kernel vulnerabilities.
The Anatomy of Windows Telemetry
Explore Windows Telemetry architecture, data collection points, and management. Learn about disabling and reducing telemetry, with insights from German cybersecurity experts.
I'm in Your Cloud, Reading Everyone's Emails - Hacking Azure AD via Active Directory
Explore Azure AD vulnerabilities, hacking techniques, and security risks in cloud environments. Learn about AD Connect, crypto magic, and service principles to enhance your cybersecurity knowledge.
BloodHound and the Adversary Resilience Methodology
Explore BloodHound's advanced features for identifying security vulnerabilities, improving attack resilience, and enhancing Active Directory defenses through graph-based analysis.
Fun with LDAP and Kerberos - Attacking AD from Non-Windows Machines
Explore Active Directory attacks from non-Windows systems using LDAP and Kerberos. Learn techniques for reconnaissance, password spraying, and ticket forging to enhance your penetration testing skills.
From Workstation to Domain Admin - Why Secure Administration Isn't Secure and How to Fix It
Explore secure administration practices, vulnerabilities in traditional methods, and strategies to enhance cybersecurity in enterprise environments. Learn to protect privileged credentials and implement effective access controls.
Threat Modelling and Beyond for Cisco ACI
Explore advanced threat modeling techniques for Cisco ACI, covering physical layout, architecture, STRIDE analysis, and potential vulnerabilities in network security.
IoT Processor and Binary Breakdown - The Good the Bad and the Ugly
Explore IoT processor architecture, binary analysis, and firmware vulnerabilities. Gain insights into hardware, Linux deployment, and virtualization for secure IoT development.
Security and Privacy for Multi-Prefix and Provisioning Domains in IPv6
Explore IPv6 security and privacy with multi-prefix and provisioning domains. Learn about implementation, routing, confidentiality, and potential threats in this comprehensive technical overview.
Introducing a Comprehensive Active Directory Security Metric
Comprehensive metric for assessing Active Directory security, covering key indicators, measurement points, and development process. Insights for enhancing organizational cybersecurity posture.
An ACE Up The Sleeve - Designing Security Descriptor Based Backdoors
Explore advanced Active Directory security techniques, focusing on designing backdoors using security descriptors. Learn about access control, security reference monitors, and stealth primitives.
Real-Life Network and Security Automation
Explore network and security automation strategies, from latency monitoring to firewall deployment, with insights on custom scripts, proactive maintenance, and reducing deployment time.
Offensive Active Directory with PowerShell
Learn offensive techniques for Active Directory using PowerShell, covering user hunting, enumeration, GPO abuse, trust exploitation, and more. Gain practical skills for penetration testing and security assessments.
Case Study - Building a Secure IPv6 Guest Wifi Network
Explore secure IPv6 guest WiFi network implementation, covering design principles, DHCP, monitoring, DNS64, and multicast considerations for enhanced network performance and security.
How to Own Any Windows Network via Group Policy Hijacking Attacks
Explore Group Policy vulnerabilities in Windows networks, including attack scenarios, exploit processes, and mitigation strategies for domain controllers and members.
Discover How EclecticIQ Platform and MISP Go Together
Explore the synergy between EclecticIQ Platform and MISP for enhanced threat intelligence sharing, automated analysis, and streamlined incident response workflows.
Abusing Bash for Windows
Explore techniques for exploiting Bash on Windows, including remote shells, password extraction, and AppLocker bypasses. Learn about security implications and forensic considerations.
Being a Cyberdefender - Behind the Curtains
Explore the realities of cyberdefense, including incident management, communication challenges, and maintaining work-life balance in this insightful talk by a seasoned professional.
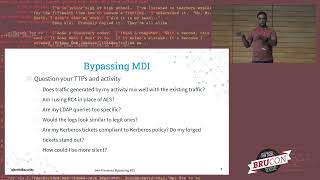
Bypassing Microsoft Defender for Identity
Explore techniques to bypass Microsoft Defender for Identity, executing high-impact attacks across the kill chain while avoiding detection in on-premises Active Directory environments.
Forging Trusts for Deception in Active Directory
Explore forging trusts in Active Directory for deception-based defense. Learn techniques to implant decoy objects, trap adversaries, and enhance network security through live demonstrations.