Climbing the PacketFence: Implementing Open Source NAC in a Corporate Environment
Explore the challenges and successes of implementing PacketFence, an open-source NAC solution, in a corporate environment. Learn about 802.1x authentication, multi-office deployment, and overcoming infrastructure hurdles.
How to Put Security in DevOps - 2017
Integrating security into DevOps: overcoming obstacles, enabling automation, and reaping benefits. Learn strategies for seamless AppSec implementation in continuous delivery environments.
Cybersecurity Insights - 2017 LASCON Keynote
Cybersecurity expert Chris Roberts shares insights on industry trends, emerging threats, and effective defense strategies in this engaging LASCON presentation.
Using Identity to Evolve Application Security - 2017
Explore how identity-based approaches can revolutionize application security, enhancing protection against modern threats and improving user experience.
Threat Modeling for Secure Software Design
Practical strategies for threat modeling in secure software design, including risk management techniques to address potential threats and integrate with real-world development priorities.
OWASP Top 10 Training - Part 3
Comprehensive exploration of OWASP Top 10 security vulnerabilities, focusing on prevention strategies and best practices for web application security.
OWASP Top 10 Training - Part 1
Comprehensive overview of OWASP Top 10 security vulnerabilities, focusing on identification, prevention, and mitigation strategies for web application developers and security professionals.
OWASP Top 10 Security Risks - Part 5
Explore the latest OWASP Top 10 security vulnerabilities, their impact, and effective mitigation strategies to enhance web application security and protect against common threats.
Making Vulnerability Management Easier with DefectDojo - 2016 OWASP Project
Streamline vulnerability management with DefectDojo: automate reporting, metrics, and self-service tools for efficient security practices in large enterprises.
Trusted Execution: A Deterministic Approach to AppSec for Zero-Day Threat Prevention - 2016
Explore Trusted Execution, a novel approach to application security that promises zero-day threat prevention through granular memory-level visibility and context, eliminating false positives in advanced security threats.
HoneyPy and HoneyDB: Leveraging Honeypots for Network Security - 2016
Explore honeypots, HoneyPy, and HoneyDB for network security. Learn about low-interaction honeypots, threat detection, and leveraging honeypot data to enhance organizational cybersecurity defenses.
Mind the CSP Gap: Challenges Developing a Meaningful Content-Security-Policy
Strategies for implementing Content Security Policy (CSP) effectively, addressing challenges and phasing in a meaningful policy without disrupting engineering teams.
API Security Best Practices and Guidelines - 2016
Explore industry-leading best practices for designing secure APIs, navigating standards, and protecting both public and private APIs to maximize benefits while keeping threats at bay.
Easy Mobile Hacking: Native and Hybrid Pitfalls - 2016
Uncover common vulnerabilities in mobile apps, both native and hybrid, using free tools. Learn to identify and exploit configuration weaknesses across Android and iOS platforms.
Practical iOS Reverse Engineering - Beyond the Script
Explore advanced iOS reverse engineering techniques, including binary patching and MACH-0 reversing, to uncover hidden vulnerabilities and bypass jailbreak detection in mobile applications.
Euro-mageddon: Updating Security and Privacy Programs for GDPR - 2016
Comprehensive guide to updating security and privacy programs for GDPR compliance, covering key principles, penalties, and practical steps for implementation over 18 months.
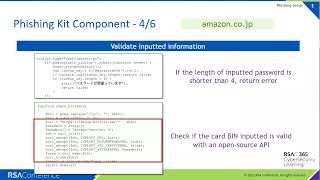
Undercover Agent in the Chinese Card Shop Ecosystem - Become a Phishing Master
Explore the Chinese dark web's credit card fraud ecosystem, gaining insights into hacker tactics and card shop operations for American cards. Learn from an undercover researcher's firsthand experiences.
We're Not Doomed! How to Successfully Manage Software Supply Chain Security
Discover strategies to enhance DevSecOps and protect against software supply chain attacks using real-world examples and the OSCAR framework. Learn to assess and improve your organization's security practices.
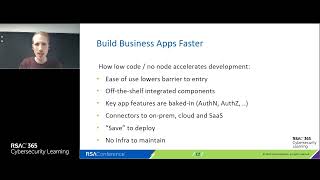
OWASP Top 10 Security Risks for Low-Code/No-Code
Explore security vulnerabilities in low-code/no-code apps, learn about the OWASP Top 10 list, and gain insights from real-world examples to enhance application security in modern development environments.
Private Learning of Gaussians and Their Mixtures
Explore private learning techniques for Gaussian distributions and mixtures, focusing on robust methods, hypothesis selection, and high-dimensional cases.
Control, Confidentiality, and the Right to Be Forgotten
Explore legal and technical aspects of data erasure, focusing on machine unlearning, confidentiality, and adaptive history independence in differential privacy contexts.