Off Grid Communications with Android - Meshing the Mobile World
Explore Android mesh networking for resilient, infrastructure-free communication. Learn to implement off-grid concepts, secure networks, and overcome hardware limitations in smartphone ad-hoc networking.
Invisibility Purge - Unmasking the Dormant Events of Invisible Web Controls
Unmasking dormant events in server web controls through refined methodology and new tool, bypassing security measures to exploit hidden application features.
Let's Play - Applanting
Discover a new attack methodology called APPLANTING, which allows attackers to install apps on Android devices without user knowledge, combining CSRF and clickjacking techniques.
Hybrid Defense - How to Protect Yourself From Polymorphic 0-days
Hybrid approach for early detection of unknown 0-day exploits at network level, combining shellcode detection algorithms to optimize classification, reduce false positives, and increase throughput.
The Deputies Are Still Confused
Exploring misunderstandings and vulnerabilities in same-origin policy, with practical examples of attacks bypassing common content-isolation mechanisms for CSRF, clickjacking, and NTLM protection.
Hardening Windows 8 Apps for the Windows Store
Explore security considerations for Windows 8 Store apps, covering HTML5, backend services, cloud computing, and WinRT to ensure robust and privacy-focused mobile development.
Honeypot That Can Bite - Reverse Penetration
Explore aggressive honeypot techniques for de-anonymizing attackers, assessing skill levels, and gaining control. Learn real-world applications and effectiveness through case studies and practical examples.
Next Generation Mobile Rootkits
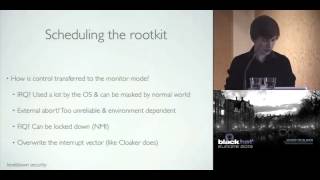
Explore advanced mobile rootkit techniques using ARM TrustZone, including implementation, hiding methods, and lessons learned from creating an actual rootkit.
Multiplayer Online Games Insecurity
Explore vulnerabilities in multiplayer online games, including game-specific issues, Steam Browser Protocol security, and a new 0-day vulnerability in a popular game.
Hacking Video Conferencing Systems
Explore vulnerabilities in high-end videoconferencing systems, focusing on Polycom HDX devices. Learn about firmware analysis, device rooting, and remote exploitation techniques for H.323 protocol.
SSL Future Authenticity
Exploring SSL's history, current authenticity issues, recent infrastructure attacks, and potential solutions, with a focus on fixing trust relationships in this fundamental protocol.
Floating Car Data from Smartphones
Exploring smartphone-based traffic data: privacy implications, location tracking, and potential vulnerabilities in navigation systems. Presents a protocol to enhance security and protect user privacy.
Harnessing GPUs - Building Better Browser Based Botnets
Explore browser-based botnets using GPUs for powerful computations. Learn about XSS, HTML5, and WebGL techniques to create efficient, cross-platform botnets capable of breaking strong encryption and impacting cybersecurity.
Web Application Brute Forcing 101
Learn techniques for web application brute forcing, exploring vulnerabilities and security measures to protect against unauthorized access attempts.
Phase II - 2nd Generation Honeynet Technologies
Explore cutting-edge advancements in honeypot technologies for enhanced cybersecurity. Learn about innovative techniques to detect and analyze network intrusions from industry experts.
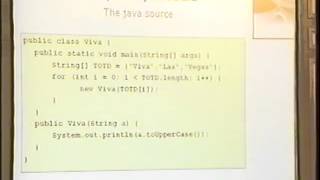
Security Aspects in Java Bytecode Engineering
Explore security vulnerabilities in Java bytecode and learn techniques for bytecode engineering to enhance application security.
Scene of the Cybercrime
Explore cybercrime investigation techniques, digital forensics, and legal considerations in this comprehensive talk on combating online criminal activities.
Fact and Fiction - Defending Your Medical Devices
Explore medical device security, debunk myths, and learn about a real software bug. Gain insights on improving device security and proper vulnerability disclosure to the FDA.
With BIGDATA Comes BIG Responsibility - Practical Exploiting of MDX Injections
Explore OLAP technology vulnerabilities in Business Intelligence systems, focusing on MDX-related attacks, code injection, and data retrieval vectors. Learn practical exploitation techniques for critical corporate data.
Post Exploitation Operations with Cloud Synchronization Services
Explore post-exploitation techniques using cloud sync services. Learn about DropSmack v2, credential theft, and security risks. Gain insights for both network defenders and penetration testers.
Energy Fraud and Blackouts - Issues with Wireless Metering Protocols
Análisis de seguridad del protocolo inalámbrico M-Bus para medidores inteligentes, revelando vulnerabilidades que amenazan la privacidad, integridad y fiabilidad de las redes eléctricas avanzadas.