Walk Through Access Control Systems
Exploring vulnerabilities in biometric access control systems, including server command forgery, unauthorized user addition, and face database exposure. Demonstrates exploits to leak employee data and bypass security measures.
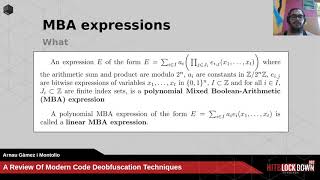
A Review of Modern Code Deobfuscation Techniques
Explore modern code deobfuscation techniques, from basic analysis to advanced semantic-based methods. Learn limitations of syntactic approaches and discover state-of-the-art program synthesis techniques.
System-Level Threats - Assumptions in Modern Product Security
Explore system-level security threats and challenge assumptions in modern product security. Gain insights into potential vulnerabilities and strategies for robust protection.
Hacking Yachts Remotely - IoT Hacking At Sea
Explore vulnerabilities in yacht IoT systems and learn techniques for remote hacking of maritime vessels, uncovering potential security risks at sea.
Hunting Threats in Your Enterprise
Explore advanced threat hunting techniques and strategies for enterprise security, focusing on proactive detection and mitigation of cyber threats in complex environments.
Rethinking the Cyber Kill Chain
Explore the cyber kill chain as a defensive framework for security professionals, shifting from vulnerability-centric to threat-centric approaches in cybersecurity.
Traversing the Kill-Chain - The New Shiny in 2018
Explore cutting-edge red teaming techniques, OSINT sources, and tools for target discovery and profiling. Learn to navigate advanced EDR systems and adapt tactics for successful penetration in 2018's cybersecurity landscape.
NFC Payments - The Art of Relay and Replay Attacks
Explore NFC payment vulnerabilities, including relay and replay attacks. Learn about hardware, software, and techniques used to exploit NFC transactions and tokenization processes.
Viewer Discretion Advised - Decoding an iOS Vulnerability
Uncover a hidden iOS vulnerability in the video-decoder driver, exploitable from sandboxed processes. Learn techniques for finding and exploiting complex mobile security flaws in closed-source environments.
Hacking BLE Bicycle Locks for Fun and - A Small - Profit
Explore BLE bicycle lock hacking in ride-sharing economy. Learn to analyze mobile-lock communications, simplify BLE attacks using mobile phones and Frida, and break locks for free rides.
Owning Electronic Locks Without Leaving A Trace
Unveiling vulnerabilities in widely-used electronic locks, demonstrating potential for undetectable breaches. Explores implications beyond hotel security, offering insights into long-term research and ethical hacking.
God Mode Unlocked - Hardware Backdoors in x86 CPUs
Unveiling a critical hardware backdoor in x86 CPUs allowing unprivileged users to bypass security checks and escalate to kernel-level access. Explores detection, prevention, and broader implications for processor security.
Insecurity Is Eating the World
Explore the critical security challenges in modern technology and the urgent need for automated, scalable solutions to protect interconnected systems and data in our rapidly evolving digital world.
Hacking Mobile Games - Closing The Gap
Exploring mobile game hacking techniques to disrupt in-game balances, focusing on monetization strategies and security mechanisms in the current gaming landscape.
Software Security Era - Past, Present, and Future
Explore the evolution of memory corruption exploitation, from early techniques to modern mitigations. Includes live demos of vulnerabilities and discusses the ongoing challenges in software security.
Learning How to Smurf with Honeypots
Explore how honeypots can enhance blue team skills, covering topics like Cyber Threat Intelligence, DevSecOps, and Attack Modeling to improve cybersecurity operations.
The Trails of WINDSHIFT APT
Explore WINDSHIFT APT's unique cyber espionage tactics, including advanced spear phishing, macOS malware, and surveillance techniques. Learn about their focus on specific individuals and hard-to-attribute methods.
Breaking Full Disk Encryption
Breaking Full Disk Encryption: Explore techniques to bypass custom FDE setups remotely, enhancing forensic analysis capabilities for compromised systems with proprietary encryption.
Security is What We Make of It - Blockchain and Beyond
Exploring blockchain's impact on security, data privacy, and enterprise infrastructure. Baldet discusses practical applications, future possibilities, and why information security professionals should engage with this technology now.
Uncovering the Android Patch Gap
Revealing Android security vulnerabilities: analysis of missing patches in vendor firmwares, enabling users to verify patch levels and improve overall protection.
A Risk Assessment of Logo Disclosures
Exploring the risks of "logo disclosure" in cybersecurity marketing, analyzing authentic bug bounty programs, and discussing the impact of aggressive marketing on security research.