The Big "P" Problem in Cybersecurity
Explore the growing trend of cybersecurity professionals leaving the field, understand the underlying causes, and discover potential solutions to address this critical industry challenge.
FAIR STRIDE - Building Business Relevant Threat Models
Explore FAIR STRIDE, a method for creating application threat models to determine ROI on security controls and prioritize risk reduction efforts for scalable product security.
Overwatch - A Serverless Approach to Orchestrating Your Security Automation
Discover Overwatch: a serverless security orchestration solution in Go, simplifying CI management and infrastructure maintenance for lean security teams shifting left.
MTV Reboot - My Super Sweet 16-Bit Malware - MS-DOS Edition - TSR Remix
Deep-dive analysis of MS-DOS malware, exploring infection techniques, stealth mechanisms, and persistence methods. Highlights technical complexity and graphical displays in 16-bit DOS malware through reverse-engineering.
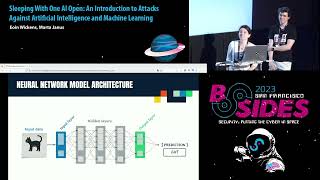
Sleeping With One AI Open - An Introduction to Attacks Against Artificial Intelligence and Machine Learning
Explore vulnerabilities in AI systems and learn about various attacks on machine learning algorithms, their potential impacts, and the importance of AI security awareness.
Growing Your Skillset with Capture the Flag
Strategies for maximizing learning in Capture the Flag competitions, including tips for beginners and insights from an organizer's perspective on tackling new topics effectively.
HALT AND CATCH FIRE - Social Engineering CTFs for Fun to a Job as a Professional Red Team Social Engineer
Explore the transition from social engineering competitions to professional red team engagements, examining the differences in tactics, strategies, and real-world applications.
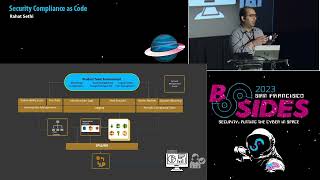
Security Compliance as Code
Explore how to transform security compliance frameworks into code, streamlining processes and reducing burden on engineering teams while maintaining industry standards and customer trust.
HSMs in Plain Envelopes - A Code Signing Story
Explore the challenges of code signing for open source developers, addressing outdated mechanisms and high costs while examining the complexities and frustrations involved in the process.
Hunting Supply Chain Threats Using Anomaly Detection
Explore a case study on detecting supply chain threats through anomaly detection in Cloud API logs, offering insights into advanced cybersecurity techniques.
I Hope This Sticks - Analyzing ClipboardEvent Listeners for XSS
Explore ClipboardEvent listeners as potential XSS vectors in web applications. Learn techniques for identifying and exploiting vulnerabilities to enhance your offensive security skills.
Story of an RCE on Apple Through Hot Jar Swapping
Discover how Frans Rosen achieved remote code execution on Apple through hot jar swapping. Learn about the research, exploit, and analysis behind this impressive security finding.
Reversing Web Assembly
Explore techniques for reversing Web Assembly (wasm) in this offensive security talk. Learn key strategies and tools for analyzing and understanding wasm code.
Blackbox Monitoring for Timely Bug Detection
Discover effective blackbox monitoring techniques for timely bug detection in web applications. Learn task-based hybrid approaches, freshness indicators, and risk markers for improved security.
A Heaven for Hackers - Breaking Web Security Virtual Appliance
Explore web security vulnerabilities and hacking techniques through hands-on demonstrations, focusing on methodology, enumeration, and exploitation of common weaknesses in web applications.
Practical Attacks Using HTTP Request Smuggling
Explore practical HTTP request smuggling attacks, including CL.TE/TE.CL desync techniques, testing methods, and real-world examples. Learn to exploit vulnerabilities for session stealing and response queue poisoning.
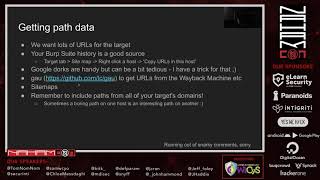
Who, What, Where, When, Wordlist
Explore techniques for creating and utilizing effective wordlists in cybersecurity, including target-specific lists, data processing, and practical applications for bug hunting.
The Pwning Machine - An Easy to Setup Pwning Station
Explore the Pwning Machine, an easy-to-setup hacking environment. Learn about its features, including a basic server, markdown editor, and pipeline runner for efficient cybersecurity tasks.
How to Use Amass Efficiently
Comprehensive guide on maximizing Amass tool for efficient information gathering and reconnaissance in cybersecurity, presented by expert Jeff Foley at NahamCon2020.
Scaling Up - Automated Attack Surface Discovery with Intrigue Core
Explore automated attack surface discovery using Intrigue Core for efficient cybersecurity scaling. Learn techniques to identify vulnerabilities and enhance your security posture.
You've Got Pwned - Exploiting E-Mail Systems
Explore email system vulnerabilities and exploitation techniques in this informative talk by @securinti, covering key security risks and potential attack vectors.