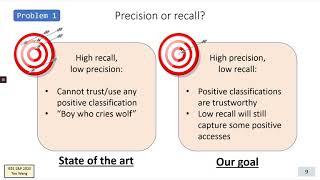
High Precision Open-World Website Fingerprinting
Enhancing precision in open-world website fingerprinting attacks, optimizing classifiers to identify browsed pages from packet metadata with high accuracy across various scenarios.
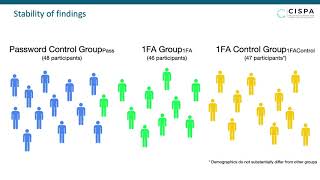
A Comparative Usability Study of FIDO2 Passwordless Authentication
Explore FIDO2 passwordless authentication's usability and user acceptance through a large-scale lab study, revealing insights on perception, concerns, and recommendations for widespread adoption.
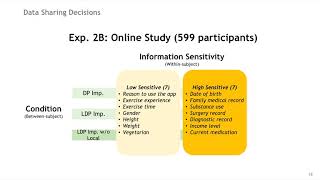
Towards Effective Differential Privacy Communication for Users' Data Sharing Decision and Comprehension
Exploring user comprehension and data sharing decisions in differential privacy, focusing on effective communication strategies for laypersons in health app settings.
SoK - Sanitizing for Security
Overview of dynamic bug-finding tools (sanitizers) for C/C++, their security vulnerability coverage, performance, and trade-offs.
Kiss from a Rogue - Evaluating Detectability of Pay-at-the-Pump Card Skimmers
Explore the effectiveness of security measures against card skimmers at gas pumps, including consumer-facing indicators and detection apps, through comprehensive analysis and real-world data.
Stealthy Porn - Understanding Real World Adversarial Images for Illicit Online Promotion
Explore real-world adversarial techniques used to evade image-based detection in online porn promotion, analyzing evasion methods and their effectiveness against popular content detectors.
Dangerous Skills - Understanding and Mitigating Security Risks of Voice-Controlled Third-Party Functions on Virtual Personal Assistant Systems
Explore security vulnerabilities in virtual personal assistants, focusing on voice squatting and masquerading attacks. Learn about risks and mitigation strategies for third-party functions on smart speakers.
The Code That Never Ran - Modeling Attacks on Speculative Evaluation
Modeling speculative evaluation attacks like Spectre using pomsets. Proposes abstract model to express known attacks, verify countermeasures, and predict new compiler optimization-based vulnerabilities.
On the Feasibility of Rerouting-Based DDoS Defenses
Analyzes the feasibility of rerouting-based DDoS defenses, highlighting fundamental trade-offs and limitations in current inter-domain infrastructure. Emphasizes the need for rigorous security analysis and real-world testing of new defense proposals.
Data Recovery on Encrypted Databases with k-Nearest Neighbor Query Leakage
Explores data recovery attacks on encrypted databases supporting k-nearest neighbor queries, analyzing feasibility of exact reconstruction and proposing practical approximate reconstruction methods for spatial data.
Understanding the Security of ARM Debugging Features
Comprehensive analysis of ARM debugging features' security implications across various platforms, exposing vulnerabilities and demonstrating the Nailgun attack to highlight potential risks.
Attack Directories, Not Caches - Side Channel Attacks in a Non Inclusive World
Explores novel side-channel attacks on non-inclusive cache hierarchies, demonstrating vulnerabilities in modern systems through directory structure exploitation and cross-core Prime+Probe techniques.
ProFuzzer - On-the-fly Input Type Probing for Better Zero-day Vulnerability Discovery
Innovative fuzzing technique that automatically probes input fields, adapts mutation strategies, and enhances zero-day vulnerability discovery without prior input specifications.
Fuzzing File Systems via Two-Dimensional Input Space Exploration
Explores innovative fuzzing technique for file systems, addressing challenges in input space exploration, operation generation, and bug reproduction. Introduces JANUS, a feedback-driven fuzzer with improved efficiency and reproducibility.
Comprehensive Privacy Analysis of Deep Learning
Análisis exhaustivo de la privacidad en el aprendizaje profundo, destacando ataques de inferencia de caja blanca y vulnerabilidades en modelos centralizados y federados.
True2F - Backdoor Resistant Authentication Tokens
Innovative system for second-factor authentication offering enhanced security against phishing, software compromise, token faults, and backdoors. Introduces new protocols and privacy defenses while maintaining compatibility with U2F-enabled services.
Cloud Chatter - Defending Against Cloud C2
Explore strategies for defending against cloud-based command and control (C2) attacks, enhancing your cybersecurity skills to protect cloud infrastructure from sophisticated threats.
Hacking Serverless Applications - A Treasure Map For Uncharted Waters
Explore vulnerabilities and security challenges in serverless architectures, gaining insights to protect cloud-native applications from potential threats.
Patterns, Trends And Practices In Software Security
Explore key patterns, trends, and best practices in software security with insights from industry expert Elisa Cavatorta. Gain valuable knowledge to enhance your cybersecurity strategies.
Detection At Scale
Explore strategies for implementing large-scale threat detection systems, focusing on efficiency, scalability, and effectiveness in modern cybersecurity environments.
Where Do You Draw The Line?
Explore ethical boundaries in cybersecurity with Patricia R. Gain insights on navigating complex moral dilemmas and making principled decisions in the field.