Transparency in the Software Supply Chain - Making SBOM a Reality
Explore the concept of Software Bill of Materials (SBOM) and its potential to enhance transparency in the software supply chain, discussing benefits, challenges, and implementation strategies.
HTTP Desync Attacks - Smashing into the Cell Next Door
Explore techniques for HTTP request splicing, enabling remote attackers to manipulate web infrastructure, exploit visitors, and breach system isolation. Learn detection, case studies, and mitigation strategies.
Office in Wonderland
Explore novel techniques abusing Microsoft Office features for offensive purposes, including new vulnerabilities, attack vectors, and security impacts of the suite's architectural design.
Behind the Scenes - The Industry of Social Media Manipulation Driven by Malware
Unveiling the structured industry behind social media manipulation, from IoT botnets to reseller panels and residential proxies. Explores ecosystem, automation, and economic impacts.
iOS Dual Booting Demystified
Explore iOS dual booting, secure boot process, and custom firmware loading. Learn reverse engineering techniques and system components for advanced iOS understanding.
Selling 0-Days to Governments and Offensive Security Companies
Explore the intriguing world of vulnerability brokerage, including the process, market dynamics, and ethical considerations of selling 0-day exploits to governments and security firms.

New Vulnerabilities in 5G Networks
Explore new vulnerabilities in 5G networks, focusing on operator infrastructure and end-device security. Learn about MC Catcher capabilities, mobile network mapping, and potential risks for cellular and IoT devices.
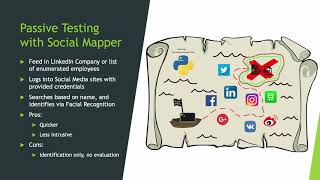
Testing Your Organization's Social Media Awareness
Explore automated social media intelligence gathering techniques to identify potential targets within organizations and learn strategies for enhancing social media awareness and protection.
Preloading Insecurity in Your Electron
Explore vulnerabilities in Electron-based apps, focusing on BrowserWindow preload as an attack surface. Learn how XSS can lead to RCE and discover security implications for developers.
ClickOnce and You're in - When Appref-ms Abuse is Operating as Intended
Explore .appref-ms file abuse for malicious purposes, including deployment methods, user perspective, and techniques to enhance and mask nefarious capabilities.
Attacking Electric Motors for Fun and Profit
Explore electric motor vulnerabilities and attacks bridging cyber and physical realms. Learn about security risks, attack methods, and protective measures for this critical technology.

Biometric Authentication Under Threat - Liveness Detection Hacking
Explore techniques for bypassing biometric authentication systems, including facial and voiceprint recognition, through liveness detection hacking and specific attack methods.
Legal GNSS Spoofing and Its Effects on Autonomous Vehicles
Explore GNSS spoofing's impact on autonomous vehicles, legal challenges in vulnerability assessment, and potential attack scenarios, with recommendations for enhancing system security.
Monsters in the Middleboxes - Building Tools for Detecting HTTPS Interception
Explore HTTPS interception detection tools and insights, uncovering security vulnerabilities in middleboxes and enhancing network protection strategies.
Perfectly Deniable Steganographic Disk Encryption
Explore self-concealing, deniable encryption techniques similar to VeraCrypt's hidden volume feature, covering design, implementation, and forensic analysis considerations.
DIFUZE - Android Kernel Driver Fuzzing
Explore Android kernel driver fuzzing with DIFUZE, a tool for identifying vulnerabilities in third-party driver code. Learn techniques to improve Android security infrastructure and discover potential weaknesses.
CLKscrew - Exposing the Perils of Security-Oblivious Energy Management
Explore CLKSCREW attack: software-based fault attacks exploiting energy management vulnerabilities, enabling security breaches without physical access to devices or specialized equipment.
Breaking Bad - Stealing Patient Data Through Medical Devices
Explore risks of connected healthcare devices, including attack surfaces, data vulnerabilities, and real-world case studies of medical IoT security breaches and their implications.
Breaking XSS Mitigations Via Script Gadgets
Explore a novel web hacking technique that bypasses XSS mitigations using script gadgets. Learn about HTML sanitizers, CSP, and practical demonstrations of this powerful attack method.

Bot vs. Bot for Evading Machine Learning Malware Detection
Explore automated evasion techniques against machine learning-based malware detection, including AI-driven approaches and strategies for model hardening.
Practical Approach to Automate the Discovery and Eradication of Open-Source Software Vulnerabilities
Discover and eradicate open-source vulnerabilities in web applications at scale. Learn Netflix's pragmatic approach to identifying risks, triaging vulnerabilities, and implementing effective remediation strategies.