Credential Attack Recon Detection - How Tooling Fail and How to Reduce False Positives
Explore advanced techniques for detecting credential attacks, reducing false positives in UEBA and NID tools, and improving overall cybersecurity defenses.
Bug Bounties - Crowdsourcing Nosey Bastards
Explore the complexities of bug bounty programs, their effectiveness, and hidden challenges. Gain insights into hunter archetypes and the paradoxical nature of crowdsourced security testing.
Build to Hack, Hack to Build
Explore container exploitation and security in DevOps with BOtB tool. Learn to identify, exploit, and remediate vulnerabilities in Docker and LXC environments before production releases.
Hacking RF - Breaking What We Can't See
Explore RF security vulnerabilities, including replay attacks and jamming. Learn about SDRs, two-way communication, and biohacking implications in wireless systems beyond WiFi and Bluetooth.
You Won't Even Know It's Recording You
Explore mobile app analytics tools, their data collection practices, and privacy implications. Learn techniques to identify session replay capabilities and device fingerprinting methods in iOS and Android apps.
Powershell Is Dead - Epic Learnings
Explore advanced PowerShell techniques, EDR evasion, and the evolving landscape of Windows endpoint security. Gain insights into offensive and defensive strategies for red teaming and threat emulation.
The Little Phone That Could Ch-ch-chroot
Explore cost-effective Red Team tactics using a covert disposable phone for reconnaissance, including device rooting, functionality, and anti-forensics techniques.
Deep Dive on the Dark Web
Explore tools and techniques used by cybercriminals on the dark web, from stolen credit cards to ransomware, and learn proactive defense strategies against various cyber threats.
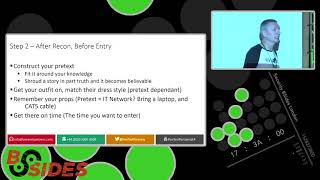
How I Break Into Casinos, Airports and CNI - The Basics of Social Engineering
Discover the art of social engineering for ethical hacking. Learn reconnaissance, disguise, pretext creation, and interaction techniques to infiltrate secure facilities while maintaining professionalism and ethics.
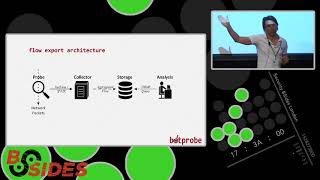
BotProbe - Botnet Traffic Capture Using IPFIX
Explore IPFIX for efficient botnet traffic capture, reducing data volume by 97% and enhancing threat detection capabilities in network security.
Solving Threat Detection
Explore key issues in threat detection, including information sharing, SOC models, and tooling challenges. Learn practical solutions and real-world examples from Countercept's hunt team experiences.
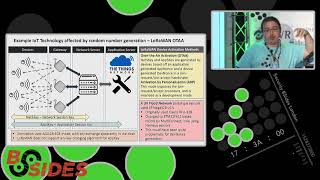
Random Problems in IoT
Explore IoT device security vulnerabilities related to random number generation, their impact on cryptography, and potential solutions for embedded systems.
Hunt Or Be Hunted
Explore advanced threat hunting techniques, datasets, and analytical approaches for effective cybersecurity. Learn to detect compromises missed by traditional methods and improve defensive strategies.
Truly Anonymous Credentials Using Modern Cryptography
Explore anonymous authentication using linkable ring signatures, enabling spam prevention without compromising user privacy. Learn cryptographic principles and see a demo of an anti-spam anonymous forum on Tor/I2P.
WiFi-based IMSI Catcher
Explore WiFi-based IMSI catchers, their potential for easier smartphone tracking, and learn about mitigation strategies for vendors, operators, and users to address privacy concerns.
The Underground Economy of Apple ID
Explore the underground economy of Apple IDs, including real-world attacks, profit methods, and protective measures. Learn about vulnerabilities and Apple's mitigation efforts.
BeyondCorp - Beyond "Fortress" Security
BeyondCorp: A new security model that grants access based on device and user credentials, eliminating the need for traditional VPNs and enabling secure work from any network.
Advanced Internet Dataset Combinations for Threat Hunting and Attack Prediction
Explore advanced techniques for threat hunting and attack prediction using innovative Internet dataset combinations, moving beyond traditional methods for enhanced cybersecurity.
Reducing Mixtape to Master Key Scenarios - How to Block the Dark Army from Mayhem Using API-Driven Access Control
Discover API-driven access control strategies to enhance security by eliminating "master keys" and implementing temporary, context-based privileged access in your infrastructure.
Hijacking .NET to Defend PowerShell
Explore stealthy .NET hijacking techniques for defending against PowerShell attacks, covering assembly modification, injection, profiling, and function hooking from a blue team perspective.
Five Keys to Building an Application Security Program in the Age of DevOps
Discover strategies for integrating security into DevOps practices, balancing risk management with rapid development, and implementing automated security measures for more secure code delivery.