Everything Useful I Learned About Software Security, I Learned at Microsoft
Discover key software security insights from Michael Howard's 18-year Microsoft journey, covering depreciation, friction reduction, network security, and practical strategies for robust development.
Fast Adversaries - Fast Countermeasures
Fast-paced hacking techniques and countermeasures: Learn about adversaries' evolving tools, tactics, and how to protect assets effectively. Explore rapid detection, patching, and risk management strategies.
Security Automation in the Agile SDLC - Real World Cases
Explore real-world examples of implementing successful security automation in fast-paced Agile development environments, focusing on practical strategies and processes.
Managing Certificates and TLS Endpoints
Explore TLS/SSL management, vulnerabilities, and tools for maintaining secure systems. Learn about emerging threats, automation techniques, and best practices for certificate and endpoint management.
Getting Security Up to Speed with CI - CD
Automating security in CI/CD: Learn about Threadfix-Centric Application Security Architecture, challenges in AppSec testing, and leveraging QA regression for enhanced coverage.
Designing Flexibility in Software to Increase Security
Explore designing flexible software architecture to enhance security, adapt to changes, and prevent vulnerabilities. Learn from real-world examples and gain practical tips for writing better, more adaptable code.
Httpillage - Calling All Nodes
Explore distributed HTTP-based attacks using Httpillage, a tool for multi-node penetration testing. Learn to enhance impact demonstration and overcome limitations of single-host security assessments.
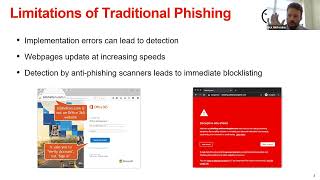
Catching Transparent Phish - Understanding and Detecting MITM Phishing Kits
Explore MITM phishing toolkits, their threat models, and detection methods. Learn about network-level analysis, classifiers, and countermeasures to enhance cybersecurity defenses.
A Wander Through the World of Container Security
Explore container security, from Docker to Kubernetes, covering breakout vulnerabilities, networking challenges, and RBAC. Gain insights into potential threats and future attack vectors in containerized environments.
OWASP Flagship Projects - OWASP Dependency-Check
Learn to identify and mitigate vulnerabilities in software dependencies using OWASP Dependency-Check, enhancing application security through effective composition analysis.
OWASP Flagship Projects - OWASP DefectDojo
Learn about OWASP DefectDojo, an open-source application security management tool. Explore its features, automation capabilities, deployment options, and community-driven development.
OWASP Flagship Projects - OWASP Juice Shop
Explore OWASP Juice Shop, a vulnerable web application for security training. Learn about challenges, cross-site scripting, coding exercises, and future enhancements in this comprehensive overview.
OWASP Cloud-Native Application Security Top 10 Flagship Project
Explore key security challenges and best practices for cloud-native applications, focusing on OWASP's top 10 vulnerabilities and mitigation strategies.
OWASP Flagship Projects - OWASP Amass
Explore OWASP Amass, a powerful tool for information gathering and external asset discovery in cybersecurity. Learn its features, data sources, and future developments.
Cyber Insurance - A Primer for Infosec
Explore cyber insurance: market growth, policy coverage, underwriting challenges, and its relevance to information security professionals. Gain insights into this evolving field and its impact on risk management.
Lessons Learned from the DevSecOps Trenches
Panel discussion on scaling AppSec programs, featuring insights from security leaders at major tech companies. Covers high-ROI efforts, effective tools, and lessons learned to help organizations improve their security practices.
On the Frontlines - Securing a Major Cryptocurrency Exchange
Explore cryptocurrency exchange security challenges and innovative defenses against various attacks, from website vulnerabilities to blockchain issues, with insights from a leading security architect.
Preventing Mobile App and API Abuse
Explore mobile app and API security threats, countermeasures, and defense-in-depth techniques through a courier service's evolving security approach against malicious attacks.
Contact Center Authentication
Explore best practices for authenticating customers over the phone in contact centers, including research findings, common pitfalls, and innovative solutions for improved security and user experience.
Pose a Threat - How Perceptual Analysis Helps Bug Hunters
Innovative techniques for efficient bug hunting using perceptual analysis, serverless infrastructure, and machine learning to identify security vulnerabilities at scale.
Threat Model Every Story - Practical Continuous Threat Modeling Work for Your Team
Explore continuous threat modeling for agile teams, focusing on collaborative methodologies and the PyTM open-source tool to enhance product security throughout development.