The Battle to Address Mobile in the Endpoint Security Space
Explore mobile device security challenges, threats, and vulnerabilities in enterprise environments. Learn about the increasing importance of mobile security and strategies to protect against data breaches.
Learning the Power of the -Not My Responsibility- Mindset
Discover how shifting security responsibility to the business can improve accountability, reduce friction, and prevent burnout among security engineers while enhancing overall company security.
Securing Modern API and Microservice Based Applications by Design
Learn to secure modern API and microservices architectures with expert insights on key concerns, architectural patterns, and actionable solutions for robust application security.
The A's, B's, and Four C's of Testing Cloud-Native Applications
Explore cloud-native app testing with the A's, B's, and Four C's framework, covering threat modeling, API testing, and security management for modern software development.
Micro-services Challenges - Istio to the Rescue
Explore Istio's solutions for micro-services challenges, including traffic management, policy enforcement, and security, to enhance scalability and operational efficiency.
New Age Cloud Security - How to Build Secure Multi-Cloud Applications and Still Sleep Well
Learn to build secure multi-cloud applications with modern techniques. Explore industry trends, development phases, and essential components like TLS, DNS, user management, and data encryption for robust cloud security.
Breaking Into Red Teaming
Explore essential skills, objectives, and methodologies for successful Red Team operations, covering physical access, cloud infrastructure, and effective communication strategies.
On the Internet, Nobody Knows You're a Dog - Revisiting the Meme After 25 Years
Explore the evolution of online identity verification, from historical trends to current challenges and future opportunities, including AI and ML applications in authentication and access management.
Lost in Translation - Communicating Outside of Security
Bridging the communication gap between security professionals and developers for successful DevSecOps adoption, with insights on common language and mutual understanding.
Offensive Threat Models Against the Supply Chain
Applying adversarial threat models to supply chain systems, focusing on geo-political risks and industry-specific threats to build effective threat libraries and attack sequences for improved security.
Security Testing - Is Automation Failing Us?
Explore the challenges of security testing automation and its impact on identity, privacy, and overall system protection in modern software development.
Threat Modeling for IoT Systems
Explore IoT security challenges and learn how to apply threat modeling to design and test more secure IoT systems, addressing risks in devices, web services, and client applications.
Connections - Eisenhower and the Internet
Explore the parallels between the Eisenhower Interstate System and the Internet, uncovering valuable lessons for cybersecurity and predicting the future of our digital infrastructure.
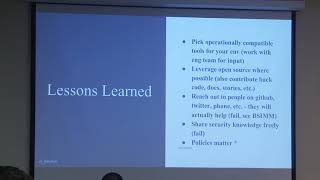
Building an AppSec Program from the Ground Up - An Honest Retrospective
Learn from a 2-year journey building an AppSec program, covering successes, failures, goal-setting, and execution. Gain insights on static analysis, threat modeling, metrics, and more for effective security implementation.
Adapting Your AppSec
Explore strategies for integrating application security into modern development processes without hindering progress. Learn about tooling, assessments, and agile methodologies for effective security implementation.
DevSecOps Without DevOps Is Just Security
Explore effective DevSecOps practices, emphasizing collaboration between security and DevOps teams. Learn prerequisites, case studies, and strategies for leveraging existing resources to enhance security integration.
Rethinking Role-Based Security Education
Strategies for developing role-based security education, focusing on high-risk teams, collaborative threat modeling, and contextualizing security hygiene to improve effectiveness and scalability.
Abusing Normality - Data Exfiltration in Plain Site
Explore stealthy data exfiltration techniques using everyday system objects and processes. Learn to identify and defend against sophisticated attacks that leverage normal-looking channels for malicious purposes.
How to Create and Cultivate Community within the Cybersecurity Industry
Explore strategies for fostering community in cybersecurity, focusing on gender diversity, professional development, and leadership. Learn to create inclusive environments and drive positive change in the industry.
Won't Somebody Please Think of the Data!
Strategies for protecting corporate data from internal threats, focusing on database security, GDPR compliance, and collaboration between engineering and operations teams.
It Was Broken When It Got Here - Security in Your Software Procurement Process
Explore strategies for ensuring security in third-party software procurement, including case studies of vulnerabilities and guidance for integrating security considerations into the purchasing process.