Make ARM Shellcode Great Again
Explore ARM shellcode techniques, from basic execve() to advanced "Quantum Leap" code, covering tight spaces, mprotect egghunters, and ARM-Thumb switching for efficient exploitation.
Digital Safety for Politically Vulnerable Organizations
Learn strategies for protecting politically vulnerable organizations from digital threats, covering physical and psychological security, incident response, and data retention policies.
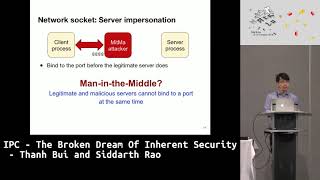
IPC - The Broken Dream of Inherent Security
Explore vulnerabilities in inter-process communication (IPC) systems, including network sockets, Windows named pipes, and USB devices. Learn about potential attacks and mitigation strategies.
Bypassing ISP and Enterprise Anti-DDoS with 90's Technology
Explore techniques for bypassing anti-DDoS measures using older technologies, focusing on UDP data analysis, intelligence gathering, and protocol effectiveness.
Trojans in SS7 - How They Bypass All Security Measures
Explore SS7 vulnerabilities and Trojan attacks that bypass security measures, focusing on signal messages, numbering plans, and location tracking in mobile networks.
What The Fax?
Explore the security vulnerabilities of fax technology, including debugging challenges, attack vectors, and mitigation strategies in this comprehensive analysis.
The Snake Keeps Reinventing Itself
Explore the evolution and tactics of "The Snake" malware, including infection vectors, lateral movement, and backdoor mechanisms in this cybersecurity analysis.
Real World - Threat Intelligence
Explore real-world threat intelligence in activism, emergency response, and political adversaries. Learn to diagnose problems, develop treatment plans, and understand various security threats.
Threat Hunting in the Cloud
Explore cloud security challenges, attacker strategies, and effective threat hunting techniques in AWS and Azure environments. Learn to protect against and detect sophisticated cloud-based attacks.
What is Our Ethical Obligation to Ship Secure Code?
Explore ethical obligations in secure coding, data breaches, and developer responsibilities. Gain insights on improving security practices and addressing user privacy concerns.
Trick or Treat - Unveil the "Stratum" of the Mining Pools
Unveil mining pool strategies, identify Stratum servers, and explore cryptomining malware detection techniques through static and dynamic analysis, web scraping, and network scanning.
Where Do We Go From Here? - Stalkerware, Spouseware, and What We Should Do About It
Explore stalkerware and spouseware threats, their impact on victims, and potential solutions. Learn about detection, legal aspects, and the role of tech companies in combating these privacy invasions.
Ichthyology - Phishing as a Science
Explore the psychology of phishing, analyze real-world attacks, and learn evidence-based prevention techniques. Discover how to protect against credential theft and evaluate the effectiveness of phishing training.
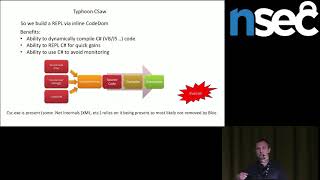
Quick Retooling with .NET Payloads
Explore dynamic .NET implants for red teams, focusing on flexible retooling, OpSec, and overcoming static defenses using DLRium Managed Execution toolkit.
Exploits in Wetware
Exploits in wetware: social engineering techniques, OSINT strategies, and defensive measures against human vulnerabilities in cybersecurity, based on real-world experiences.
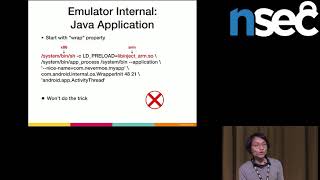
One Step Before Game Hackers - Instrumenting Android Emulators
Explore native hooking on Android emulators, understanding process start routines and emulation strategies. Learn why existing frameworks fail and how to create one that works for game cheating.
Data Breaches - Barbarians in the Throne Room
Analyze hundreds of data breach disclosures to understand common vulnerabilities, focusing on preventable issues like patching and configuration failures, and their impact on enterprises.
Prototype Pollution Attacks in NodeJS Applications
Explore prototype pollution attacks in NodeJS, including APIs vulnerable to pollution, potential impacts, and defensive strategies. Learn from real-world examples and security research findings.
The Blackbear Project
Explore a modified OpenSSH daemon that enhances post-exploitation capabilities, bypasses network restrictions, and provides reliable interactive shell access for penetration testing and security research.
Abusing Webhooks for Command and Control
Explore techniques for establishing covert command and control communication using webhooks, bypassing strict network defenses and avoiding detection in penetration testing scenarios.
Backslash Powered Scanning - Implementing Human Intuition
Innovative web scanner using intuitive techniques to detect injection vulnerabilities, offering WAF evasion, minimal network footprint, and adaptability to input filtering. Explores advanced exploitation methods and handles complex findings.