Hacking Fintech Crime Realities & Possibilities
Insights into tackling cybercrime targeting fintech platforms in India, exploring hacking techniques, law enforcement challenges, and potential countermeasures to protect the digital economy.
Web 3.0 Smart Contracts Could Be Leaky
Explore the challenges and solutions in writing secure smart contracts for Web 3.0, including preventing sensitive information leaks and deploying to decentralized servers.
Honey I Just Put The Hospital On A Ventilator
Explore DICOM file vulnerabilities in healthcare and learn about an entropy-based detection technique to identify malicious files, with demonstrations of attacks and protective solutions for Linux and Windows.
Hacking Android Foreground Services Escalation Of Privileges
Explore Android foreground services vulnerabilities, including a race condition bug and its patch bypass, demonstrating potential escalation of privileges and security implications.
Securing the Software
Expert panel discusses strategies and challenges in software security, offering insights for industry professionals and organizations to enhance their cybersecurity practices.
Automate Your Whatsapp Chats
Learn to automate WhatsApp chats on Android using Accessibility Services. Discover how to create a sample app, explore potential security risks, and gain insights into automating various Android functions.
0Day Up Your Sleeve - Attacking macOS Environments
Comprehensive guide to macOS security vulnerabilities, including live demonstration of 0-day exploit, post-exploitation techniques, and hardening recommendations for Mac infrastructures.
Does Your SOC Suck?
Panel discussion on optimizing Security Operations Centers (SOCs), covering best practices, challenges, and innovative approaches to enhance cybersecurity monitoring and response capabilities.
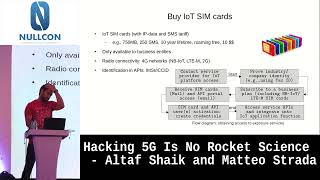
Hacking 5G Is No Rocket Science
Explore API attacks in 4G/5G IoT networks, revealing vulnerabilities and discrepancies between security standards and real-world implementations. Learn about potential threats and defense strategies for mobile IoT infrastructure.
Securing India - The CERT-In Way
Panel discussion on CERT-IN's notification for reporting security breaches, emphasizing timely incident reporting, organizational awareness, and citizen precautions to enhance India's cybersecurity posture.
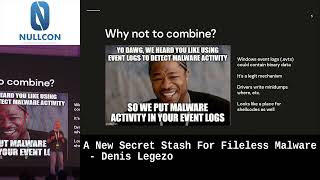
A New Secret Stash For Fileless Malware
Explores advanced fileless malware techniques using Windows event logs for code hiding and infection. Reveals new methods to conceal shellcode and manipulate logging functions.
PAM Maturity From Zero Trust To Least Privilege
Panel discussion on PAM maturity, exploring the journey from zero trust to least privilege. Industry experts share insights on implementing effective privileged access management strategies in modern cybersecurity landscapes.
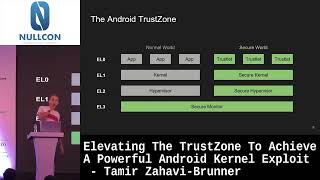
Elevating the TrustZone to Achieve a Powerful Android Kernel Exploit
Explore a novel Android kernel exploitation technique using TrustZone to bypass security mitigations, achieve 100% reliability, and create a versatile exploit applicable across devices and versions.
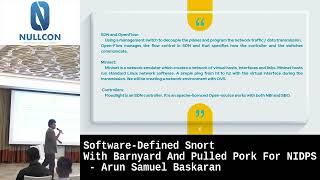
Software Defined Snort With Barnyard & Pulled Pork For NIDPS
Explore software-defined networking for enhanced network security, focusing on DDoS defense and traffic programming using Snort and its dependencies to mitigate WAF bypass attempts.
Unlocking Security Collaboration With Cyber Threat Intelligence
Panel discussion exploring how CXOs can leverage cyber threat intelligence for enhanced security collaboration and proactive defense strategies in today's evolving threat landscape.
Cloud Services for Financial Inclusion - Possibilities and Challenges
Panel discussion exploring cloud services' potential and challenges for financial inclusion, featuring insights from cybersecurity experts and industry leaders.

Raining CVEs on WordPress Plugins with Semgrep
Leveraging Semgrep to identify vulnerabilities in WordPress plugins, reducing false positives, and automating XSS validation. Includes demos on custom rule creation and the XSSBomb tool.
Consumer Bug Bounty Panel - Tech Bug Bounty Panel - Hear from the Program Managers
Panel discussion with program managers sharing insights on running bug bounty programs, challenges faced, and best practices for organizations.
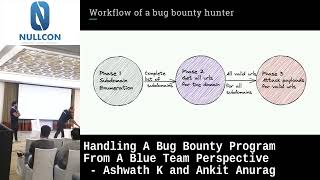
Handling a Bug Bounty Program from a Blue Team Perspective
Strategies for blue teams to manage bug bounty programs effectively, balancing security needs with researcher experience. Focuses on mitigating operational risks and optimizing defense rules for real threats.
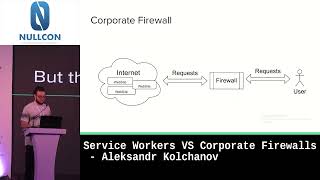
Service Workers vs Corporate Firewalls
Explore how service workers can be exploited to bypass corporate firewalls, potentially compromising network security. Learn about this innovative attack vector and its implications.
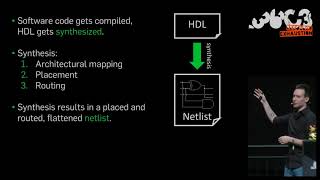
HAL - The Open-Source Hardware Analyzer
Einführung in Hardware-Reverse-Engineering und Vorstellung von HAL, dem ersten Open-Source-Framework zur Analyse von Netzlisten für die Erkennung von Hardware-Manipulationen und Backdoors.