De 0 a millones de dólares en un par de paquetes
Descubre cómo vulnerabilidades recientes expusieron millones de dólares en Internet. Aprende sobre exploits públicos que amenazan a grandes empresas y cómo fueron descubiertos y explotados en solo 72 horas tras los parches.
Response Smuggling - Exploiting HTTP/1.1 Connections
Explore response pipeline desynchronization in HTTP Smuggling, a novel attack vector for bypassing restrictions and breaching web application security in complex systems.
Do not drink and wardrive
Recorrido en trencito para mapear redes Wi-Fi urbanas, analizando su demografía, encriptación y protocolos. Monitoreo pasivo para estudiar la evolución de la seguridad inalámbrica.
Do not drink and wardrive - Pt2
Recorrido en tren para mapear redes Wi-Fi urbanas, analizando su demografía, encriptación y protocolos. Permite evaluar la evolución de la seguridad inalámbrica a lo largo del tiempo.
Ret2page - The Art of Exploiting Use-After-Free Vulnerabilities in the Dedicated Cache
Explore a new exploitation technique for Use-After-Free vulnerabilities, focusing on SLUB and BUDDY allocators to improve efficiency and success rates in physical page reuse and Android rooting.
Android Universal Root - Exploiting Mobile GPU - Command Queue Drivers
Explore GPU hacking techniques and vulnerabilities in Android device drivers, focusing on rooting methods and security implications for mobile systems.
A Journey Into Fuzzing WebAssembly Virtual Machines
Explore WebAssembly VM architecture, attack surfaces, and fuzzing strategies. Learn about bug discovery across multiple projects using various fuzzing techniques and frameworks.
A New Trend for the Blue Team - Using a Symbolic Engine to Detect Evasive Forms of Malware - Ransomware
Explore symbolic engines for detecting evasive malware and ransomware, enhancing blue team capabilities in reverse engineering and threat analysis.

Trace Me if You Can - Bypassing Linux Syscall Tracing
Novel vulnerabilities and exploitation techniques to bypass Linux syscall tracing, even with security measures like seccomp, SELinux, and AppArmor in place. Demonstrates how user-mode programs can evade detection.
Monitoring Surveillance Vendors - A Deep Dive into In-the-Wild Android Full Chains in 2021
Explore in-the-wild Android exploits discovered by Google's TAG and Android Security teams, including deep dives into CVE-2021-0920 and novel kernel exploitation techniques for bypassing hardware mitigations.
New Memory Forensics Techniques to Defeat Device Monitoring Malware
Discover new Volatility plugins for detecting device monitoring malware across major OS. Learn about advanced memory forensics techniques to combat sophisticated threats.
Unlimited Results - Breaking Firmware Encryption of ESP32-V3
Unveiling vulnerabilities in ESP32-V3 microcontrollers through hardware security evaluation, focusing on extracting firmware encryption keys to decrypt flash content containing potential secret data.
Backdooring and Hijacking Azure AD Accounts by Abusing External Identities
Explore Azure AD external identities, their vulnerabilities, and potential exploitation methods for backdooring and hijacking accounts in this informative cybersecurity presentation.
Automatic Protocol Reverse Engineering
Discover techniques for automatically extracting network protocol specifications from binary code, useful for security analysis, bug finding, and understanding botnet communications.
Building an Open Source Artificial Pancreas
Exploring the development of an open-source artificial pancreas system for type 1 diabetes management, its technical aspects, and personal impact on blood sugar control.
Recreating Forgotten Programming Languages, for Art
Explore the revival of early computer graphics languages, focusing on ART 1's recreation to understand vintage digital art techniques and limitations.
Servo - Designing and Implementing a Parallel Browser
Explore Servo, an experimental browser engine designed for multi-core hardware, focusing on parallelization and security through Rust. Learn about its goals, design, and potential impact on web browsing.
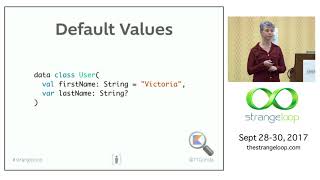
Kotlin - Uncovered
Explore Kotlin's inner workings by decompiling to Java, examining data classes, lambdas, and delegation to gain deeper understanding and tools for further investigation.
Security for Humans - Privacy and Coercion Resistant Design
Explore privacy-focused design principles and coercion-resistant techniques to enhance digital security for individuals, with insights from a leading cybersecurity expert.

How to Make Error Handling Less Error-Prone
Explore innovative approaches to error handling, focusing on automatic state recovery and the 'Ken' protocol for distributed systems to enhance program reliability and security.
Fast, Secure, Safe - The Web That Can Still Be
Explore the potential for a faster, more secure, and safer web ecosystem, addressing current challenges and proposing innovative solutions for a better online future.