Public, Verifiable, and Unbiasable Randomness - Wassat?
Explore randomness types, their importance, and applications. Learn about drand, a distributed randomness software, and its role in providing public, verifiable randomness as a service.
Passive Recon & Intelligence Collection Using Cyber-Squatted Domains
Explore passive intelligence gathering through domain squatting, including low-cost techniques, data analysis, and defensive strategies against this cyber threat.
Tell Me Where You Live and I Will Tell Your Password
Explores factors influencing password quality across countries, revealing literacy levels and internet usage impact. Aims to understand macrosocial protection factors for adapting password lists.
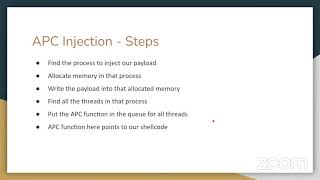
Advanced Process Injection Techniques
Hands-on workshop exploring APT tactics for privilege escalation and persistence. Learn to develop stealthy implants through 7 labs on Windows process injection techniques.
Web Application Firewall Workshop
Hands-on workshop exploring Web Application Firewall bypass techniques, including encoding, SQL injection, protocol switching, and syntax alternatives. Practical exercises with in-depth explanations for each method.
Request Smuggling 101
Explore HTTP Request Smuggling attacks, risks, and payloads. Learn to detect and mitigate vulnerabilities in load balancers and proxies. Includes live demonstration and practical mitigation strategies.
Burnout - Destabilizing Retention Goals and Threatening Organizational Security
Explore strategies to prevent burnout in cybersecurity professionals, improve talent retention, and maintain organizational security through effective mental health support and skill development.
Forensicating Endpoint Artifacts in the World of Cloud Storage Services
Explore key forensic artifacts in cloud storage services like OneDrive and Dropbox, focusing on data exfiltration detection and acquisition techniques for endpoint investigations.
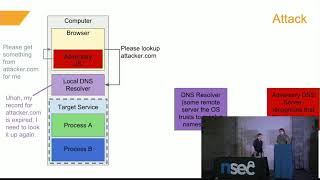
Homeward Bound - Scanning Private IP Space with DNS Rebinding
Explore DNS Rebinding attacks, their resurgence, and tools for network reconnaissance from inside browsers. Learn about a "localhost census" page that enumerates HTTP services on visitors' computers.
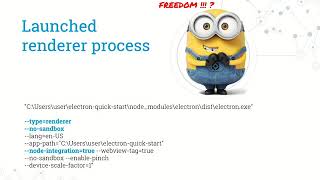
Only an Electron Away from Code Execution
Explore security vulnerabilities in Electron framework, focusing on XSS risks in desktop applications. Learn about attack vectors, CVEs, and see live demos of exploiting vulnerable Electron apps.
Attacking Linux Moose Unraveled an Ego Market
Unraveling a large-scale botnet conducting social media fraud through honeypots and HTTPS man-in-the-middle attacks. Explores technical details, methodology, and market dynamics behind social media fraud.
Deep Dive Into Tor Onion Services
Explore Tor onion services: their evolution, security improvements, and critical applications. Learn about the new design's enhanced privacy, scalability, and development status.
Modern Reconnaissance Phase by APT - Protection Layer
Evolving APT reconnaissance techniques using malicious documents and watering hole attacks. Detailed analysis of obfuscation methods, scripting languages, and mitigation strategies for enhanced cybersecurity.
Stupid RedTeamer Tricks
Discover simple yet effective red teaming tricks to enhance assessments, including improved USB key drops, C&C concealment, and social engineering techniques using Outlook.
BearSSL - SSL for All Things
Explore BearSSL, an SSL/TLS library optimized for constrained systems. Learn about secure crypto, SSL attacks and defenses, and implementing in small RAM environments.
Hack Microsoft Using Microsoft Signed Binaries
Explore advanced attack techniques using Microsoft signed binaries and PowerShell to bypass detection, manipulate memory, and achieve persistence in Windows systems.
Pentesting - Lessons from Star Wars
Explore threat modeling through Star Wars, gaining practical insights for effective offensive and defensive security strategies in software development.
Not Safe For Organizing - The State of Targeted Attacks Against Civil Society
Exploration of targeted cyber attacks against civil society groups, focusing on Tibetan community and Latin American cases. Discusses attacker tactics, victim impacts, and future trends.
Bypassing Application Whitelisting in Critical Infrastructures
Explore techniques to bypass application whitelisting in critical systems, including code execution, protection bypasses, and vulnerabilities in McAfee's application control.
Real Solutions From Real Incidents - Save Money and Your Job
Learn cost-effective strategies to prevent security incidents through real-world scenarios, gap analysis, and enterprise protection methods. Gain insights on leveraging incident response lessons for improved security programs.
Analysis of High Level Intermediate Representation in a Distributed Environment for Large Scale Malware Processing
Explore advanced malware analysis techniques using distributed reverse engineering and machine learning to identify code similarities and extract key characteristics from millions of samples.