Cryptographic Function Detection in Obfuscated Binaries via Bit-Precise Symbolic Loop Mapping
Explore bit-precise symbolic loop mapping for identifying cryptographic functions in obfuscated binaries, enhancing malware defense and forensics through innovative detection techniques.
A Framework for Universally Composable Diffie-Hellman Key Exchange
Explore a framework for universally composable Diffie-Hellman key exchange, simplifying analysis of real-world protocols and reducing the need for complex reduction proofs in cryptographic security.
Verified Models and Reference Implementations for the TLS 1.3 Standard Candidate
Comprehensive analysis of TLS 1.3 Draft-18, addressing security concerns, verifying computational security, and extending guarantees to implementations through symbolic and computational models.
Turning a PKI Around with Decentralized Automated Incentives
Explore automated responses to unauthorized certificates and incentives for improved PKI security through blockchain-based consensus and smart contracts.
Cryptographically Protected Database Search
Exploration of cryptographically protected database search systems, analyzing primitive operations, current implementations, potential attacks, and future directions for enhancing data security and functionality.
Membership Inference Attacks against Machine Learning Models
Explore membership inference attacks on machine learning models, focusing on techniques to determine if specific data was used in training, with implications for privacy and security in ML applications.
Spectre Attacks Exploiting Speculative Execution
Explore speculative execution vulnerabilities in modern processors, their impact on system security, and potential countermeasures to protect against Spectre attacks.
Defense Against the Dark Arts
Overview of adversarial example research in machine learning, exploring attacks, defenses, and future directions for enhancing AI security and robustness against malicious inputs.
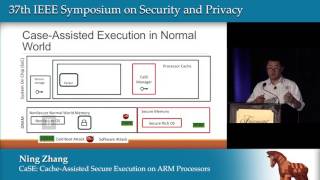
CaSE- Cache-Assisted Secure Execution on ARM Processors
Secure execution framework for ARM processors using TrustZone and Cache-as-RAM to protect sensitive applications against software attacks and cold boot attacks, with minimal performance impact.
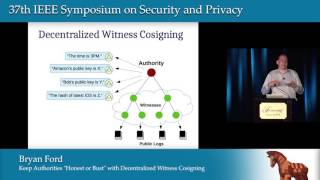
Keeping Authorities "Honest or Bust" with Decentralized Witness Cosigning
Explore decentralized witness cosigning to enhance authority security, prevent undetected exploits, and ensure public scrutiny of authoritative statements through scalable collective signatures.
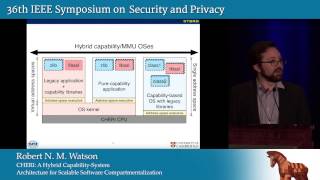
CHERI - A Hybrid Capability-System Architecture for Scalable Software Compartmentalization
Explores CHERI architecture for enhanced memory protection and software compartmentalization, demonstrating improved scalability and security benefits over traditional MMU designs.
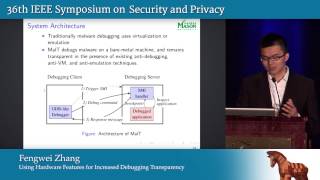
Using Hardware Features for Increased Debugging Transparency
Explore hardware-based debugging techniques for enhanced malware analysis transparency, leveraging System Management Mode to overcome limitations of virtualization and emulation methods.
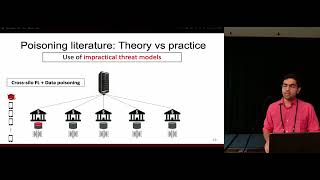
Back to the Drawing Board - A Critical Evaluation of Poisoning Attacks on Federated Learning
Critical evaluation of poisoning attacks on federated learning, examining threat models, attack types, and robustness across different FL settings. Insights for researchers and practitioners in secure machine learning.
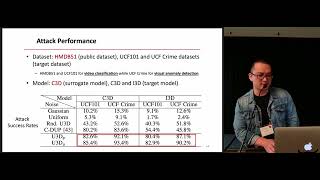
Universal 3-Dimensional Perturbations for Black-Box Attacks on Video Recognition Systems
Explore innovative techniques for creating universal 3D perturbations to challenge and test the robustness of video recognition systems in black-box attack scenarios.
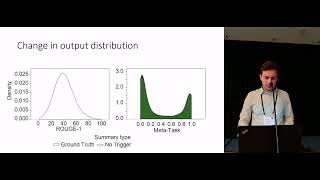
Spinning Language Models: Risks of Propaganda-as-a-Service and Countermeasures
Explore risks and countermeasures of using language models for propaganda, including classification vs sequence-to-sequence models, spin techniques, and defense strategies.
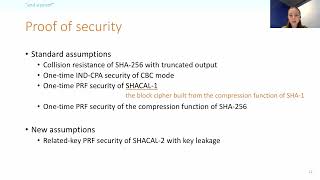
Four Attacks and a Proof for Telegram
Explore cryptographic vulnerabilities in Telegram's MTProto 2.0 protocol, including symmetric channel attacks, related key issues, and implementation flaws. Learn about security models and proofs for messaging apps.
Post-Quantum WireGuard
Explore post-quantum cryptography in WireGuard, covering core handshake security, computational models, and key confidentiality for enhanced network protection.
CryptGPU: Fast Privacy-Preserving Machine Learning on the GPU
Explore GPU-accelerated privacy-preserving machine learning techniques for enhanced performance and scalability in image classification and private training.
High-Assurance Cryptography in the Spectre Era
Explore cutting-edge cryptography techniques addressing Spectre vulnerabilities, focusing on constant-time implementations and speculative execution semantics for enhanced security.
Invisible Probe - Timing Attacks with PCIe Congestion Side-channel
Explore timing attacks using PCIe congestion side-channels, including challenges, contributions, experiments, and potential mitigations in this IEEE presentation.
Diogenes: Lightweight Scalable RSA Modulus Generation with a Dishonest Majority
Explore lightweight RSA modulus generation with a dishonest majority, covering protocol design, secure multiplication, and zero-knowledge constraints for enhanced cryptographic security.