A WASM Runtime for FaaS Protected by TEE
Explore confidential computing with WASM runtime for FaaS protected by TEE. Learn about Inclavare, cloud-native containers, and how WASM addresses cross-platform issues in secure cloud environments.
ASP.NET Core 3 - IdentityServer4: Sign Out and Certificates - Episode 18
Learn to implement sign-out functionality and use certificates in IdentityServer4 with ASP.NET Core 3. Covers client app logout and certificate creation for enhanced security.
ASP.NET Core 3 - OAuth - JWT Bearer Token Generation and Authorization - Episode 5
Generate and authorize JWT tokens in ASP.NET Core 3. Learn in-depth techniques for implementing secure authentication using JSON Web Tokens in your web applications.
Removing Identity Server 4 from ASP.NET Core Project - Tricking Library Ep47
Simplifying authentication by removing Identity Server 4 in favor of a more straightforward approach for ASP.NET Core, C#, EF Core, Nuxtjs, and Vuetify applications.
Silent Token Renewal in ASP.NET Core with IdentityServer4 and OIDC-Client - Tricking Library Ep34
Implementación de renovación silenciosa de tokens en aplicación Nuxt.js usando oidc-client. Incluye estilización de login/registro y configuración de perfil de usuario.
ASP.NET Core, C#, IdentityServer4, Nuxtjs - Authorization - Episode 30
Implementación de autorización en API usando ASP.NET Core, diferenciando roles de usuario como miembros e invitados en el contexto de una biblioteca de trucos.
ASP.NET Core Dynamic Authorization with Minimal APIs - .NET 7
Learn dynamic authorization in ASP.NET Core using C# and Minimal APIs. Generate and enforce permissions, implement background refreshing, and create authorization policies for secure API development.

ASP.NET Core Identity Management Guide - .NET 7 Minimal APIs
Explore ASP.NET Core identity management using minimal APIs in .NET 7. Learn bespoke management techniques and Identity Framework implementation for secure user authentication.

OAuth 2.0 and 2.1 Explained
Comprehensive explanation of OAuth 2.0 and 2.1 protocols, including JWT integration, for secure authorization and authentication in web applications.
Writing an Embedded Operating System in Rust
Explore Rust's potential for embedded systems through Tock OS, focusing on memory safety, concurrent applications, and hardware isolation in ARM Cortex-M and RISC-V platforms.
The Five Big Problems with Confidential Containers
Explore five major challenges in confidential containers technology: attestation, performance, image download, access control, and debuggability. Learn about current solutions and future prospects.
You Probably Don't Need a Service Mesh - Considerations for Cloud Native Architectures
Explore considerations for adopting Service Mesh in Cloud Native environments, weighing its benefits against complexity and engineering overhead based on real-world experience with Istio.
Detecting Malicious Dependencies at Scale with Static Analysis
Explore static analysis techniques for identifying malicious dependencies in open-source packages, including Semgrep rules and metadata analysis to enhance software supply chain security.
Better Protect Sensitive Data in the Cloud with Client-Side Application Layer Encryption
Learn to implement client-side application layer encryption for enhanced data protection in cloud environments, reducing breach risks and maintaining control over sensitive information.
Using WebAssembly to Run, Extend, and Secure Applications
Explore WebAssembly's evolution, security features, and applications beyond browsers. Learn to run, extend, and secure apps using WASM, WASI, and Trusted Execution Environments.
Application Security Testing Career Guide for 2024
Comprehensive guide to starting an Application Security career, covering fundamentals, programming, security concepts, tools, and certifications. Practical advice for building skills and avoiding information overload.
Fuzz Everything, Everywhere, All at Once - Advanced QEMU-Based Fuzzing
Explore advanced QEMU-based fuzzing techniques for binary-only targets, including command and SQL injection detection, and scalable Android library testing without physical devices.
Hacking and Securing Android Applications - Vulnerabilities and Prevention
Explore Android app vulnerabilities, learn detection methods, and discover how 'safe to run' library can enhance security in this talk on mobile application security.
ASVS Testing: Understanding Access Requirements for Verification
Analyzing ASVS requirements to identify necessary access for accurate verification, aiding test case generation and helping companies understand the effort required for comprehensive security assessments.
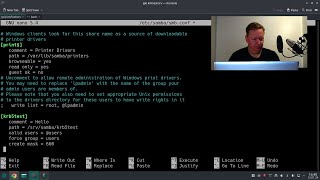
SMB/Samba/CIFS Server with Kerberos Authentication - Lecture 16C
Create and configure an SMB/Samba/CIFS server with Kerberos authentication, enabling secure file sharing and network resource access in a Windows-compatible environment.
Nine Rules for Creating Fast, Safe, and Compatible Data Structures in Rust
Discover 9 essential rules for crafting efficient, safe, and compatible Rust data structures. Learn from real-world experience and gain insights applicable to both beginners and experienced developers.