Modernizing Authorization in Cloud Native Environments
Explore modern authorization techniques for cloud-native applications, focusing on scalable and flexible solutions to enhance security and access control in distributed systems.
Run WASM - Shim This Way: Enhancing Container Development with WebAssembly
Explore server-side WebAssembly's potential to enhance developer experience, running alongside containers using familiar technologies like Kubernetes, containerd, and Docker Compose.
The Negatives of Per-Host Service Mesh - Sidecar Model as an Ideal Solution for Robust Security
Explore the security implications of per-host service mesh vs. sidecar model in Kubernetes, focusing on proxy footprint, blast radius, and security boundaries for robust and scalable services.
Securing Norway's Welfare System: Transparent End-to-End Encryption in the Cloud
Explore how Norway's welfare system secures its cloud-based platform, balancing developer convenience, reliability, and security for 1600+ applications on Kubernetes, with focus on transparent end-to-end encryption.
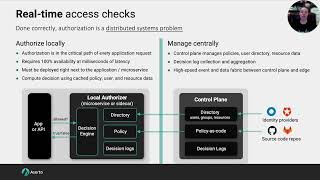
The Current State of Cloud-Native Authorization
Explore the latest developments in cloud-native authorization, examining key trends, challenges, and best practices for securing modern distributed systems.
Step Up Your Cloud Native Push - Unlocking Business Potential
Discover how cloud-native solutions align with customer priorities, delivering enhanced experiences, personalization, security, and innovation while empowering businesses to meet demands efficiently and gain a competitive edge.
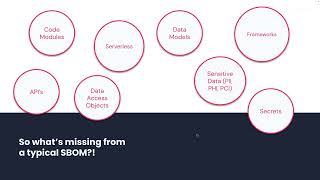
Why You Need an XBOM - The Extended Software Bill of Materials
Explore the extended Software Bill of Materials (XBOM) concept, its importance in software development, and the benefits of adopting this approach for enhanced security and transparency.
Reshape Enterprise Cloud Native Security with Harbor and Narrows
Explore cutting-edge solutions for enhancing cloud native security in enterprise environments using Harbor and Narrows technologies.
Securing Requests with Keycloak and Istio through Request-Level Authentication
Explore request-level authentication using Keycloak and Istio to enhance security in cloud-native environments. Learn implementation techniques for robust access control.
OWASP ZAP Project: Introduction to Web Application Security Testing
Learn to use OWASP ZAP, a powerful open-source web application security scanner. Discover its features, capabilities, and best practices for identifying vulnerabilities in web applications.
What's New in CRS4 - An Update from the OWASP CRS Project
Explore the latest updates and enhancements in CRS4, the OWASP Core Rule Set project, with insights on improved web application security and threat mitigation strategies.
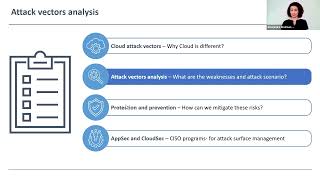
Cloud Attack Surface Management
Explore cloud security challenges and strategies for effective attack surface management in this insightful keynote by Alex Shulman Peleg.
15 Years of OWASP Top 10 - Has the Cloud Made a Difference?
Explore the evolution of web application security over 15 years, examining the impact of cloud computing on OWASP Top 10 vulnerabilities and current cybersecurity challenges.
Azure Vulnerability Testbed (AzGOAT) - Understanding and Hardening Azure Security
Explore Azure security vulnerabilities and defenses with AzGOAT, a lab environment for understanding attack surfaces, designing secure solutions, and minimizing threats in Azure environments.
Exploiting Web Messaging Implementations
Uncover vulnerabilities in cross-document messaging, learn common developer mistakes, and explore open-source tools for identifying post messaging security issues in web applications.
Insiders Guide to Mobile AppSec with Latest OWASP MASVS
Explore mobile app security with OWASP MASVS, covering data storage, network calls, authentication, coding, and reverse engineering. Gain insights from real-world experience and latest tools for effective mobile pentesting.
Testability Patterns for Web Applications - A New OWASP Project
Explore testability patterns for web applications in this OWASP project presentation, focusing on enhancing security testing effectiveness and efficiency.
Mobile Application Security Testing - Journey to Version 2.0
Explore the evolution of mobile app security standards and best practices in this insightful talk on the journey to OWASP Mobile Security Testing Guide v2.0.
How to Meet the New Mobile Application Security Imperative
Explore strategies for enhancing mobile app security, addressing vulnerabilities, and meeting modern security imperatives in this informative OWASP presentation.
Squeezing the Last Drop Out of OWASP Juice Shop
Explore advanced hacking techniques and security challenges in this hands-on session with OWASP Juice Shop, led by its creator Bjoern Kimminich.
Server-Side Prototype Pollution: Detection and Exploitation Techniques - OWASP AppSec Dublin
Explore server-side prototype pollution vulnerabilities, detection techniques, and prevention strategies in web applications with security expert Gareth Heyes.