The Diary of an Inexperienced Bug Hunter - Introduction to Android Hacking
Explore Android app security, bug bounty programs, and essential tools for mobile penetration testing. Learn structure analysis and gain practical insights for successful Android hacking.
Mach-O and the App Store - Understanding iOS Binary Format and Submission Process
Explore iOS app execution, Mach-O binary format, and App Store submission process. Gain insights into code storage, execution, and DRM implementation for iOS applications.
Turbo Intruder: Abusing HTTP Misfeatures to Accelerate Web Application Attacks
Explore advanced HTTP exploitation techniques using Turbo Intruder, a high-speed Burp extension for automated web application attacks, with insights on payload generation and response analysis.
Finding Sensitive Data in Android Apps - LevelUpX Series 12
Explore techniques for accessing and extracting sensitive data from Android apps' internal storage, with tools and strategies for impactful bug bounty reports.
Log4Shell - The Worst Java Vulnerability in Years
Explore the critical Log4Shell vulnerability, its impact on Java systems, and essential mitigation strategies in this comprehensive security analysis.
Hunting for Amazon Cognito Security Misconfigurations
Explore Amazon Cognito security misconfigurations, including unauthorized access, authentication bypass, and privilege escalation. Learn detection techniques and developer recommendations.
Cloud Hacking - Malware Not Needed
Explore cloud hacking techniques without malware, covering state actors, exploitation methods, and initial foothold strategies for offensive security professionals.
GraphQL CTF and XSS Challenge Walkthrough - Hacker101 and Bug Bounty Notes
Explore GraphQL CTF challenges and XSS vulnerabilities in this hands-on session. Learn practical hacking techniques and improve your bug bounty hunting skills.
Cloud Hacking- The Basics
Explore fundamental techniques for identifying and exploiting vulnerabilities in cloud infrastructure, enhancing your offensive security skills and understanding of cloud security risks.
How to Use WPScan - A Walkthrough with the Author
Comprehensive walkthrough on using WPScan for WordPress security assessment, featuring insights from the tool's creator ethicalhack3r during a Live Recon episode.

Burp Suite Pro Features and Walkthrough
Explore advanced features of Burp Suite Pro for ethical hacking and web application security testing. Learn powerful tools to enhance your penetration testing skills.

Python 101 for Penetration Testing - Episode 2
Comprehensive introduction to Python programming for aspiring ethical hackers, covering fundamental concepts and practical applications in cybersecurity and penetration testing.
Build, Break, and Hack WebSockets
Explore WebSocket vulnerabilities and exploitation techniques, covering injection attacks and cross-site issues. Learn to build, break, and secure real-time web communications.
Web Application Hacking - File Upload Attacks Explained
Learn to exploit file upload vulnerabilities in web applications, including path traversal attacks and chaining multiple vulnerabilities for maximum impact.
How to Shot Web: Successful Tactics and Tools for Bug Hunting
Explore successful tactics, tools, and methodologies used by top bug hunters to improve your web and mobile app hacking skills for claiming bug bounties.
Mobile Application Security Threats Through the Eyes of the Attacker
Explore mobile app security threats from a hacker's perspective, covering attack vectors, data storage, leakage, HTTPS, SSL, firewalls, and OS controls with expert Jason Haddix.
How to Do Chrome Extension Code Reviews
Learn effective Chrome extension code review techniques, focusing on security risks, common issues, and tools. Gain insights into permissions, manifest files, and insecure coding practices to enhance bug hunting skills.
iOS Hacking - Inter-App Communication Vulnerabilities
Explore iOS inter-app communication vulnerabilities, focusing on pasteboard sharing, URL schemes, and universal links. Learn to use Frida for tracing and testing these mechanisms.
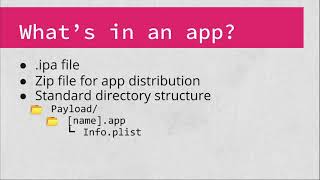
iOS Application Hacking - Understanding IPA Structure and Mach-O Binaries
Explore iOS app structure, IPA files, Mach-O binaries, and techniques to uncover hidden interfaces, API keys, and sensitive data. Learn to analyze and reconstruct app functionality.
Create a Full WordPress Website with Free Themes and Plugins - Follow Along Tutorial
Step-by-step guide to creating a WordPress website using free themes and plugins. Covers installation, customization, SEO, security, and essential features for a functional site.
Move Constructors in Rust: Possibilities and Applications
Explore self-referential types, move constructors, and novel data structures in Rust. Learn how to safely move and manipulate complex types without compromising Rust's protections.