Writing Secure Software - Applying Security Principles in Practice
Practical application of security principles in web app development, showcasing architectural decisions for enhanced security using a blog as an example.

SMTP Smuggling: A Novel Technique for Email Spoofing
Explore SMTP smuggling, a novel e-mail spoofing technique that exploits protocol interpretation vulnerabilities, allowing unauthorized sending from trusted domains while bypassing security checks.
A Beginner's Guide to Code Review
Learn essential code review techniques to identify vulnerabilities, practice with labs, and discover resources for finding code to review. Improve your skills in detecting and fixing security issues.
Productivity Monitoring, Surveillance, Automation, and Big Tech Harms in Trucking Industry
Explore how truck drivers combat technological surveillance, automation, and industry challenges, focusing on empowering female drivers and addressing Big Tech's impact on the workforce.
When to Report a Bug - Best Practices for Bug Bounty Hunters
Learn essential steps to take after discovering a bug, ensuring proper verification and documentation before submitting an official report. Maximize your bug bounty success with expert guidance.
Implicit and Mutation-Based Serialization Vulnerabilities in .NET
Explores novel .NET serialization attacks bypassing current mitigations, demonstrating vulnerabilities in popular platforms and offering detection and mitigation techniques for developers.
Investigating Hackers - Stories from Norway's National Cybercrime Center
Insights from police cybercrime investigators on forensic challenges and custom code solutions for extracting crucial data when standard tools fall short.
DevSecOps Insights and Exciting Horizons
Explore DevSecOps trends and future strategies with RSAC 2024 Program Committee members, discussing standout sessions and emerging cybersecurity approaches.
Why Railway Is Safe But Not Secure - Security of Railway Communication Protocols
Exploring railway communication protocols' security challenges, highlighting the contrast between safety and security in rail systems and discussing vulnerabilities in GSM-R, RaSTA, and ETCS/ERMTS.
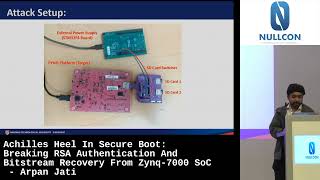
Breaking RSA Authentication and Bitstream Recovery From Zynq-7000 SoC
Uncovers critical vulnerability in Zynq-7000 SoC's secure boot, allowing RSA authentication bypass. Explores implications for embedded device security and trusted computing.
Automating Security Monitoring
Explore efficient security monitoring through automation techniques to handle increasing data volumes, complex architectures, and sophisticated threats while reducing alert fatigue.
The Hidden Risk in Undocumented API Behavior
Explore undocumented Win32 API risks affecting AV and EDR vendors. Learn how overlooked behaviors can lead to security vulnerabilities and gain insights on mitigating these hidden threats.
Banking Cybersecurity - Battling DeepFakes and AI-powered Scammers
Explore banking cybersecurity challenges, including DeepFakes and AI-powered scams. Learn strategies to protect customer data, witness a live DeepFake demo, and discover proactive measures for safeguarding financial assets.
NIS2 and CRA - Europe's Response to Cyber Threats
Explore Europe's cybersecurity strategy through NIS2 Directive and Cyber Resilience Act. Understand their impact on businesses, individuals, and smart devices, gaining insights into the evolving digital threat landscape.
Measuring the Wrong Metric - Lessons from Attacks on Critical Services
Explore a framework for evaluating cyber incidents' impact on critical services, using case studies from Costa Rica, India, and Greece. Learn to assess scale, scope, and spread for effective resource prioritization.
Surprising Ways to Escalate Privileges in Entra ID
Explore common pitfalls and privilege escalation techniques in Entra ID. Learn to identify, prevent, and monitor security risks through practical demonstrations and expert insights.
Not All Attacks Are Malicious: DDoS from Outside and Within
Explore DDoS attacks on NRK.no, their impact, and mitigation strategies. Learn about internal and external threats, and how to minimize consequences when attacks occur.
The Complexity of Reversing Flutter Applications
Explore reverse engineering Flutter applications through a CTF challenge walkthrough. Learn to analyze assembly code, parse Dart AOT snapshots, and uncover hidden flags using tools like Radare2.
Driving the Need for Identity, Authentication, and Encryption in Containerized Environments
Explore encryption, identity verification, and workload attestation in multi-service environments. Learn to implement TLS with Istio and cert-manager for robust identity management and secure communication.
Cloudy with a Chance of Zero Trust: Navigating Security in the Cloud Native Cosmos
Explore zero trust security for containerized workloads, covering threat vectors, implementation strategies, and tools. Gain insights on enhancing your organization's security posture in cloud-native environments.
Building and Using the OpenSSF Security Toolbelt - 6 Months In
Explore the OpenSSF Security Toolbelt initiative: its mission, progress, and impact on open-source security. Learn about tools, patterns, and opportunities to enhance software supply chain protection.