Principles for Package Repository Security
Exploring principles for package repository security, including a four-level maturity model. Learn about CISA and OpenSSF's collaborative efforts to enhance open source software security across ecosystems.
Network Intrusion Detection 101 with OpenWrt and OpenCanary
Learn to deploy a network intrusion detection system using OpenWrt and OpenCanary to protect your home network from potential threats posed by IoT devices and cloud-controlled gadgets.
Structured Scorecard Results: Tailor Your Own Supply-Chain Security Policies
Learn to customize OpenSSF Scorecard for tailored supply-chain security assessments using Structured Results feature. Explore practical examples and use cases for automated policy-driven analysis.
Practical SBOM Management with Zephyr and SPDX
Learn to identify, assess, and manage software components in Zephyr applications using SBOM standards and tools. Enhance security practices and respond effectively to vulnerabilities in embedded systems.
The Past, Present, and Future of Cross-Site and Cross-Origin Request Forgery
Explore the evolution of Cross-Site Request Forgery attacks, their impact on applications, and effective defense strategies. Learn about vulnerabilities in API-based systems and best practices to prevent CSRF.

OWASP Juice Shop - An Open Source Software and Security Fairytale
Explore the evolution of OWASP Juice Shop, a pioneering hacking training platform, from its inception as a pet project to becoming an OWASP Flagship project, with insights into its future developments.
Unlocking the Secrets of TLS - Understanding the TLS Handshake Process
Explore the intricacies of TLS handshake, its evolution, and how secure connections are established on the Internet. Gain insights into past mistakes and lessons learned in this process.
The Power of Observability - Merging, Scaling and DevSecOps
Explore observability's role in merging, scaling, and DevSecOps. Learn how Dustin Web Development harmonized their monitoring landscape for improved efficiency and security.
Responsible Disclosure and Legal Risks for Security Researchers
Explore responsible disclosure and legal challenges for security researchers with experts Diana Nadeborn, Andreas Bogk, and Michał Kowalczyk in this insightful panel discussion at Nullcon Berlin 2024.
My Favorite Ethical Hacking Books
Discover essential ethical hacking books recommended by a top hacker. Gain insights into web application security, bug bounty hunting, and penetration testing to enhance your cybersecurity skills.
A History Buff's Archival Approach to Open-Source Intelligence
Discover how a history student's curiosity led to founding the Dutch defense ministry's open-source intelligence branch, revolutionizing information gathering and analysis in the digital age.
Building Momentum - Two Years of Cyber Civil Defense
Explore the progress and challenges in cyber civil defense over the past two years, examining key developments, strategies, and future directions in protecting digital infrastructure.
Ethical Hacking Course - Kali Linux, Phishing Attacks, Veil, Burp Suite, and DVWA
Comprehensive ethical hacking tutorial covering Kali Linux, phishing attacks, Veil framework, Burp Suite, and DVWA. Learn essential techniques and tools for cybersecurity testing and vulnerability assessment.
Tech Companies in Armed Conflict - Risks Arising from Public-Private Partnerships
Explore the complex role of tech companies in armed conflicts, examining legal protections, security risks, and ethical implications of public-private partnerships in wartime digital infrastructure.
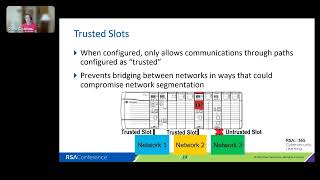
Beyond the Firewall - Ensuring OT Application Security
Explore OT application security principles, including IAM, secure development environments, secure coding for PLCs, and change detection strategies to enhance your operational technology security posture.
The End of DevSecOps? - Leveraging New Tools and AI in Engineering-First Security
Explore how Generative AI and new tools can simplify communication, reduce toil, and integrate security seamlessly into engineering processes, moving beyond traditional DevSecOps.
Agents of Chaos - Hacktivism's Role in Spreading Fear, Disinformation, and Propaganda
Explore how hacktivism fuels chaos, disinformation, and propaganda in today's cyberthreat landscape, examining its co-option by malicious actors and its impact on global events.
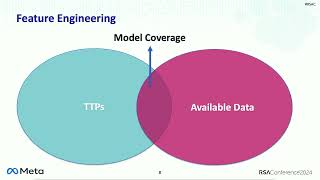
Detecting Website Intrusion and Account Compromise with Machine Learning
Explore machine learning techniques for detecting website intrusions and account compromises, covering data analysis, feature engineering, and real-time integration in open environments.
The Art of Threat-Informed Sharing - Real-life Use Cases from NSA
NSA experts share actionable intelligence on threats to US critical infrastructure, highlighting partnerships with industry to counter adversarial activities and protect allied networks.
The Cybersecurity of Smart Adult Toys - Privacy and Security Challenges
Explore privacy and security risks of smart adult toys, their impact on vulnerable groups, and the importance of holding manufacturers accountable for data protection.
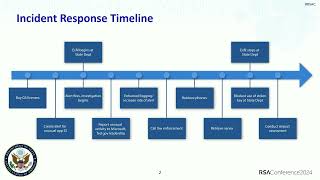
Security Challenges in Direct Threat Environments
Explore unique cybersecurity challenges faced by the US Department of State in global operations, including strategies to protect workforce, partners, and information assets in diverse environments.