Malware AV Evasion Tricks - Cryptography in Malware
Explore advanced malware evasion techniques using cryptography, enhancing your cybersecurity knowledge and defensive strategies against sophisticated threats.
MISP Updates - Hack.lu 2023
Explore the latest updates and enhancements to MISP, the open-source threat intelligence platform, presented by Andras Iklody at Hack.lu 2023.
Why Does the CTI Industry Struggle With Communicating Uncertainties?
Explore challenges in communicating uncertainties within the Cyber Threat Intelligence industry, examining industry practices and potential improvements for more effective risk assessment.
Kunai - A New Threat Hunting Tool for Linux
Discover Kunai, an innovative threat hunting tool for Linux systems. Learn its features, capabilities, and how it enhances cybersecurity through advanced detection techniques.
FOSStering an ISAC - Enabling a Community with Open-Source Tools
Explore open-source tools for building an Information Sharing and Analysis Center (ISAC), fostering community collaboration and enhancing cybersecurity threat intelligence sharing.
CTI Is Dead, Long Live CTI - Evolving Threat Intelligence Practices
Explore the evolution and future of Cyber Threat Intelligence (CTI) in this thought-provoking talk, examining its challenges, innovations, and potential impact on cybersecurity strategies.
SBOMs - Are They a Threat or a Menace?
Explore the implications of Software Bill of Materials (SBOMs) in cybersecurity, examining their potential benefits and challenges for software supply chain management.
Detecting VPNs and Proxies by Analyzing Attack Patterns Over Time
Explore techniques for identifying VPNs and proxies through analysis of their attack patterns, enhancing network security and threat detection capabilities.
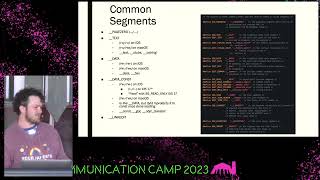
Demystify Mach-O: Understanding Apple's Executable File Format
Explore the Mach-O executable format used in Apple systems through an in-depth explanation and code demonstration, enhancing your understanding of reverse engineering Apple technologies.

Disclosure, Hack and Back - Vulnerability Reporting and Cybersecurity Insights
Explore real-world vulnerability reports and hacking incidents, revealing common mistakes in both corporate security responses and cybercriminal operations. Gain insights into improving cybersecurity practices.
Cyberattacks on MGM and Caesars - Recent Casino Breaches
Analysis of recent cyberattacks on major casino companies, exploring threat actors, breach methods, and implications for cybersecurity in the hospitality industry.
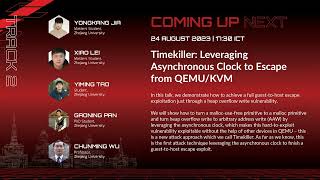
Timekiller: Escape From QEMU/KVM - Exploiting Asynchronous Clock Vulnerabilities
Demonstrating a novel guest-to-host escape exploit in QEMU/KVM using asynchronous clock vulnerabilities. Introduces "Timekiller" technique to turn heap overflow into arbitrary address write, achieving full VM escape.
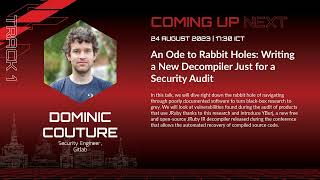
Writing a New Decompiler for JRuby Security Audits
Explore JRuby vulnerabilities and learn about YBurj, a new open-source decompiler for JRuby IR, enabling recovery of compiled source code for enhanced security audits.
Injecting Brains Into Blind SQL Injection - Optimizing Data Exfiltration
Innovative approach to optimize Blind SQL Injection using Machine Learning and statistics. Introduces Hakuin, a tool that significantly improves exfiltration speed for database schemas and content compared to standard methods.
How NTLM Relay Ruins Your Exchange Servers
Uncovers a critical NTLM relay attack surface in Exchange Server, affecting mailbox security and potentially leading to RCE. Explores vulnerabilities, exploits, patches, and protection strategies for Exchange environments.
Escaping From VMware Workstation Through the Disk Controller
Exploración detallada de una vulnerabilidad en los controladores de disco de VMware Workstation que permite escapar de una máquina virtual, con demostraciones de exploits para Linux y Windows.
Analyzing and Reverse Engineering Antivirus Signatures
Explore antivirus signature analysis and reverse engineering, gaining insights into detection evasion techniques and evaluating Microsoft Defender's effectiveness for improved cybersecurity strategies.
Lazarus Group's Undercover Operations in South Korea 2022-2023
Detailed analysis of Lazarus Group's recent cyber campaigns in South Korea, covering infiltration methods, lateral movement techniques, and data exfiltration strategies used by this sophisticated threat actor.
Extracting Information from Automotive Internet Units
Techniques for extracting and analyzing firmware from automotive internet modules, focusing on Qualcomm MDM-based units. Covers extraction methods, image analysis, and file system exploration.
Designing Your Own Electronic Attack Device
Learn to design and create custom electronic attack devices, from circuit boards to complete Linux systems, for personalized and efficient security testing and penetration tasks.
Bluetooth Sniffing: Privacy Implications and Unexpected Findings
Exploring Bluetooth sniffing implications: privacy, security, and societal impacts. Insights on device tracking, medical data, law enforcement, and potential vulnerabilities in various Bluetooth-enabled systems.