Authentication Proxy Attacks: Detection, Response and Hunting
Explore tactics for detecting and responding to MFA-enabled account takeover attacks using authentication proxies. Learn to hunt, mitigate, and block these emerging threats effectively.
Playing Games with Cybercriminals - Beyond Law Enforcement Strategies
Exploring alternative strategies to combat cybercrime beyond traditional law enforcement methods, focusing on economic disruption and market inefficiencies to undermine criminal operations.
The Importance of Engineering Privacy From the Start
Explore strategies for protecting user data and identity in software development, emphasizing the ethical responsibility of engineers as stewards of sensitive information.
Security Data Science Teams: A Guide to Prestige Classes
Explore data-driven security roles, their overlapping skills, and career paths in this talk on the evolving landscape of security data science teams and job titles.
Hiding in Plain Sight - The Untold Story of Hidden Vulnerabilities
Uncover limitations of vulnerability scanners and SCA tools through groundbreaking research. Learn about hidden vulnerabilities, scanner blindspots, and the need for holistic software security approaches.
Enemy Within - Leveraging Purple Teams for Advanced Threat Detection and Prevention
Explore cross-functional collaboration between Cyber Threat Intelligence and Offensive Security for advanced threat detection. Learn about realistic operations, live demos, and open-source tools to improve security investment.
What the Yandex Leak Reveals About Big Tech's Data Usage
Explore the implications of the Yandex leak, revealing insights into big tech's data usage practices and the extent of user information collection and analysis.
Conti Leaks and CARVER Analysis for Threat Intelligence Analysts
Applying CARVER vulnerability assessment to Conti ransomware leaks for rapid enterprise risk evaluation. Methodology and steps for maximizing intelligence value from this rare event.
I Am The Cavalry: Reflections on a Decade and Vision for the Future
Reflection on a decade of "I Am The Cavalry" initiative, discussing its impact on cybersecurity, public safety, and future challenges in an increasingly connected world.
Becoming a Dark Knight - Adversary Emulation Demonstration for ATT&CK Evaluations
Explore adversary emulation techniques using real-world APT scenarios to improve cybersecurity defenses and industry standards through MITRE ATT&CK Evaluations.
Building a Culture of Cybersecurity - A Case Study Approach to Enhancing Risk Management
Explore real-world strategies for cultivating a risk-aware cybersecurity culture through case studies, engaging both technical and non-technical staff to enhance organizational security.
Vulnerability Intelligence for All - Say Goodbye to Data Gatekeeping
Discover how the Exploit Prediction Scoring System (EPSS) consolidates threat intelligence to accelerate vulnerability management maturity and improve decision-making for teams.
OH-SINT: Merging OSINT Into Reverse Engineering Workflows to Simplify Analysis
Leveraging OSINT in reverse engineering to overcome anti-analysis techniques, track down information from developers, and speed up malware analysis workflows for quicker insights.
Double Entry Accounting for Cybersecurity - Revolutionizing Security Programs
Explore how double entry accounting principles can revolutionize cybersecurity programs, offering innovative ways to enhance and streamline security practices.
The Birds, the Bees, and the CVEs - Understanding Novel Vulnerabilities in Critical Infrastructure
Explore strategies for assessing novel vulnerabilities in critical infrastructure, focusing on control systems and medical devices. Learn techniques to understand and mitigate risks in complex ecosystems.
Security Technical Program Manager: Understanding the Role and Its Importance
Explore the Security Technical Program Manager role: responsibilities, success factors, career paths, hiring strategies, and its significance in the security field.
The History of Malware - From Floppies to Droppers
Explore the evolution of malware from its inception to modern-day threats, examining key developments, consistent elements, and lessons for cybersecurity's future.
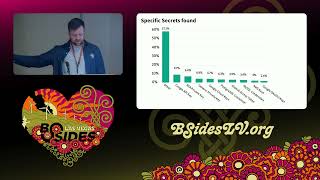
The Attacker's Guide to Exploiting Secrets in the Universe
Explore methods to discover and exploit secrets in git repositories, containers, and compiled apps. Learn about vulnerabilities in API keys and credentials across various environments.
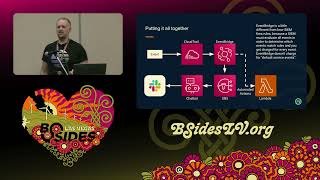
Big SIEM Energy at Micro-SIEM Cost - Building Custom Security Monitoring in AWS
Learn to build a cost-effective micro-SIEM for AWS using EventBridge, CloudTrail, SNS, and ChatBot. Discover how to tailor security monitoring to your specific needs and budget constraints.
A Hacker's Guide for Changing the World - IATC Capstone
Empowering hackers with strategies for positive global impact, including empathy, storytelling, and cyber-civics, to create meaningful change in the world.
Building a Resilient International Cyber Ecosystem - Fireside Chat with CISA Director
Fireside chat exploring international cyber resilience and hacker involvement in solutions, featuring CISA Director Jen Easterly and cybersecurity expert Keren Elazari.