Dissecting the 0-Day Supply Chain Vulnerability in Argo CD
Explore the discovery and implications of a critical 0-day vulnerability in Argo CD, including attack methods, remediation steps, and its impact on the ecosystem.
Securing Your Container Native Supply Chain with SLSA, GitHub and Tekton
Practical guide to securing container native supply chains using SLSA principles, in-toto attestations, and step-by-step demos for achieving SLSA Level 2 in Tekton and Github Actions.
Distributing Supply Chain Artifacts with OCI and ORAS Artifacts
Explore secure distribution of supply chain artifacts using OCI & ORAS Artifacts. Learn about managing artifact relationships, lifecycle management, and evolving registry capabilities for cloud-native environments.

Securing Web Services with Let's Encrypt and Cert Manager
Automate SSL/TLS certificate management for web services using Let's Encrypt and Cert Manager, enhancing security and simplifying deployment in cloud-native environments.
Securing Shopify's Software Supply Chain - Mitigating Supply Chain Attacks
Explore techniques for securing software supply chains, including cloud-based defenses, trust establishment, and malicious behavior detection, drawing from Shopify's experiences.
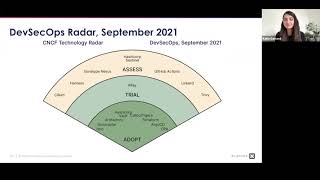
CNCF End User Technology Radar for DevSecOps - September 2021
Explore DevSecOps trends and recommendations from CNCF's End User Community. Gain insights on security solutions, micro-segmentation, and balancing security with developer experience in cloud-native environments.
Certs Magic - Exploring Cloud Native Security Certifications
Explore the world of cloud native certifications with expert Walid Shaari, gaining insights into career advancement and industry-recognized credentials.
Password Managers and Secure Passwords
Explore password security essentials: long passwords, Password Managers, and Multi-Factor Authentication. Learn how hackers guess passwords and discover NIST guidelines for robust password policies.

The Beginner's Guide to Blind XSS - Cross-Site Scripting
Learn to identify and exploit Blind XSS vulnerabilities, a critical web security flaw. Discover tools like XSS Hunter and gain practical skills for ethical hacking and bug bounty hunting.
Shining a Light on Solar System Cyber Security
Exploring critical vulnerabilities in residential and commercial power control systems, highlighting potential catastrophic risks and novel attack scenarios in the energy sector.
Breaking ML Services: Finding Zero-Days in Azure Machine Learning
Uncover critical vulnerabilities in Azure Machine Learning, including credential leaks, information disclosure, and persistence techniques. Learn assessment methods for cloud-based MLaaS platforms and shared responsibility models.
KeyBleed: Attacking the OneKey Mini Cryptocurrency Wallet - Hack In The Box 2023
Revealing vulnerabilities in cryptocurrency hardware wallets, focusing on the OneKey Mini's security flaws. Demonstrates live exploit to extract and crack the seed, recovering stored funds in under one second.
Cybersecurity Integration from the Beginning - Perils and Benefits
Explores challenges and benefits of integrating cybersecurity from project inception, offering insights on overcoming resistance, developing secure designs, and building value chains in early-stage cybersecurity implementation.
Overcoming Barriers in Security DSLs with BabbelPhish - Empowering Detection Engineers
Explore BabbelPhish, an innovative approach using large language models to bridge natural language queries and security DSLs, streamlining threat detection and making detection-as-code platforms more accessible.
Cyber Crash Investigations: Learning from Past Crises
Explore insights from cyber crisis investigations, focusing on prevention, impact reduction, and effective response strategies. Learn from real-world case studies to enhance organizational readiness.
Public Service Journeys - From Hacking Culture to Government Cybersecurity
Explore diverse journeys from military to hacking, and from hacking to government, highlighting how varied experiences strengthen cybersecurity efforts and protect the public.
Leveling Up Your Red Team with a New Capability Maturity Model
Introducing a Capability Maturity Model for Red Teams to assess readiness, plan growth, and communicate effectiveness to leadership, enhancing organizational security.
Unveiling the Hidden - Discovering RDP Vulnerabilities Using PDF Files
Innovative OSINT techniques reveal critical RDP vulnerabilities, including remote code execution and security bypasses, without conventional reverse engineering tools. Explore unconventional research methodologies and vulnerability analysis.
Wrangling Cats: How We Coordinate Red Team Testing
Explore an end-to-end process for coordinating Red Team cybersecurity testing, including onboarding, prioritization, resource allocation, and communication strategies to enhance organizational efficiency.
Understanding Technical and Enterprise Tradeoffs in Cybersecurity
Explore strategies for navigating cybersecurity challenges in organizations, understanding human behavior, and negotiating better decision-making when faced with resistance to implementing security solutions.
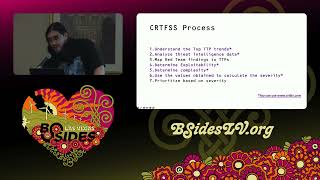
How to Prioritize Red Team Findings - Introducing CRTFSS: Common Red Team Findings Score System
Learn to prioritize red team findings with the Common Red Team Findings Score System (CRTFSS), enhancing cybersecurity assessment and decision-making processes.