Pushing Content Security Policy to Production - Case Study of Real-World Implementation
Practical insights on implementing Content Security Policy in a live web application, covering challenges, browser nuances, third-party integrations, and real-world violation reports.
Fixing XSS with Content Security Policy
Learn how Content Security Policy (CSP) can prevent XSS attacks, understand its versions, browser support, and implementation strategies for web applications. Gain insights on balancing CSP with traditional security measures.
How Ireland Created and Open Sourced COVIDGreen - Panel Discussion
Explore Ireland's development and open-sourcing of COVIDGreen, a contact tracing app, through insights from key stakeholders in this informative panel discussion.
TEEP Implementation on RISC-V Keystone and Arm TrustZone
Explore TEEP implementation on RISC-V Keystone and Arm TrustZone, covering use cases, prototypes, and CBOR expressions for secure execution environments.
The Practice and Implementation of DevSecOps
Explore DevSecOps implementation, covering SAST, DAST, IAST, training tools, and maturity models. Learn best practices for integrating security into the development lifecycle.
TEEP Implementation on RISC-V Keystone and Arm TrustZone
Explore TEEP implementation on RISC-V Keystone and Arm TrustZone, focusing on secure provisioning techniques for trusted execution environments in embedded systems.
A Leap in Automotive Security through Unikernel-based De-aggregation
Explore unikernel-based de-aggregation for enhanced automotive security, focusing on COQOS Hypervisor, Unikraft architecture, and TEE virtualization case study.
Why Won't Developers Always Write Secure Open Source Software?
Explore challenges and solutions for enhancing open source software security, addressing developer motivations and industry-wide strategies for safer code practices.
SUSI.AI - The Privacy Aware Smart Assistant
Explore SUSI.AI, a privacy-focused smart assistant. Learn about its features, development, and how it prioritizes user data protection while providing intelligent assistance.
Shift-Left to Address OS Vulnerabilities and Compliance for Cloud Native Applications
Inject security early in software development to address vulnerabilities before production, focusing on OS vulnerabilities and compliance for cloud-native apps.
Block Me if You Can - Subverting IMA
Explore techniques to subvert Integrity Measurement Architecture (IMA) in Linux systems, examining attack vectors, security guarantees, and potential mitigations.
SSH and the Command Line
Master SSH and essential command-line skills for efficient server management, process monitoring, and file operations in Linux environments.
Threat Modeling - Key Methodologies and Applications from OSS CIP Perspective
Explore key threat modeling methodologies and their applications in open source civil infrastructure platforms, enhancing security practices for critical systems.
Rust-VMM: A Security Journey
Explore rust-vmm's security journey, covering components, audits, development practices, and fuzzing techniques for virtualization and Virtio components.
Auto Generate SBOMs for Open Source Projects in Any Language and Platform
Learn to automatically generate Software Bill of Materials (SBOMs) for open source projects, enhancing security and compliance across languages and platforms.
Software Supply Chain Integrity with Sigstore
Learn about Sigstore, a tool for securing software supply chains, with demos on Cosign for signing and verifying artifacts, and insights on its practical applications.
Generating a SPDX SBOM for Your Code in CI Using ORT
Learn to generate SPDX Software Bill of Materials (SBOM) for your code in continuous integration using the OSS Review Toolkit (ORT), enhancing software transparency and security.
Developing Secure Open Source Software - Mentorship Session
Explore best practices for developing secure open source software with expert guidance on risk mitigation, vulnerability management, and collaborative security measures.
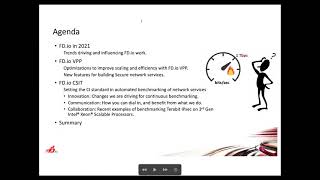
Building Secure Terabit Network Services with FD.io Technologies
Explore FD.io's role in building secure Terabit NaaS cloud networking, focusing on VPP and CSIT projects for high-performance, scalable, and robust cloud VPNs with encrypted overlays.
How Web Authentication Works: TLS, Password Hashing, OpenID Connect, OAuth 2, and JSON Web Tokens
Explore the inner workings of web authentication, covering TLS, password hashing, OpenID Connect, OAuth 2, and JSON Web Tokens in this comprehensive overview.

Netdiscover - An Open Source Tool for Finding Device IPs on Your Network Regardless of Subnet
Discover device IPs on your network with Netdiscover, an open-source tool that works across subnets. Learn installation, usage, and how to parse results in this practical tutorial.