
Making Content Security Policy Work For You
Learn about Content Security Policy (CSP), its importance in web application defense, and practical tips for implementation from Mozilla's application security expert.
Continuous Security Testing in DevOps Environments
Explore continuous security testing in DevOps, addressing challenges and presenting an open-source framework using Behavior Driven Development for effective communication and automation.
Reflections on Scoping Trust in Modern Web Environments
Reflections on trust in the modern web environment, examining gaps in current models and exploring ways to create a more trustworthy internet ecosystem without total self-reliance.

Cloud-based Detection Techniques for Botnets and Malware - AppSecEU 2014
Explores cloud-based techniques for detecting botnets and malware, highlighting limitations of traditional methods and discussing traffic analysis for pre-infection detection in cloud environments and virtual infrastructures.
Lessons from the National Security Council - Advice for the New Administration
Insights from former National Security Advisors on reforming U.S. national security decision-making, offering practical solutions for executive departments and advisory bodies shaping foreign policy.
Wi-Fi Hacking for Web Pentesters
Explore Wi-Fi vulnerabilities and learn to leverage web pentesting skills for designing and deploying malicious access points. Gain insights into attacking clients, hijacking accounts, and stealing sensitive information.
Privacy and Security Risks in the Internet of Things
Security researcher Ken Westin explores privacy risks in the Internet of Things, demonstrating how seemingly innocuous data can be exploited by criminals and how businesses can protect their customers' information.
Anatomy of Memory Scraping and Credit Card Stealing POS Malware
Explore POS system architecture, credit card processing, and malware attack techniques. Live demos showcase RAM scraping and system compromise, offering insights into vulnerabilities and protection strategies.
Leveling Up an Application Security Program
David Rook shares insights on enhancing application security at Riot Games, covering assessment, implementation of controls, secure coding guidance, and maintaining a security community in a fast-paced environment.
Devil in the Haystack - Application Security Through Statistical Analysis and Machine Learning
Exploring statistical and machine learning techniques for in-app security at Salesforce. Focuses on adaptive, data-driven approaches for detecting and preventing attacks and abuses on the platform.
AppSec is Eating Security
Explore the future of information security with Yahoo's CISO Alex Stamos as he discusses the evolving landscape of application security and its impact on the broader security field.
Fix the Damned Software - Improving Application Security Design
Explore strategies for building security into software development, moving beyond vulnerability discovery to secure design and implementation. Learn from industry experience and BSIMM data.
API Authentication's Poorly Implemented - Security Issues in Web APIs
Explore real-world API security issues, focusing on authentication and authorization problems across various platforms. Learn from examples ranging from online payment systems to embedded device infrastructures.
AppSec is Eating Security - The Future of Information Security
Explore the future of application security with insights on containerization, hardware security, and user-centric approaches. Learn about emerging trends and strategies for building safer digital ecosystems.
Election Integrity - Verifying and Securing the American Electoral Process
Experts discuss vulnerabilities in the American voting system, verification processes, and efforts to secure electoral legitimacy amid cyber threats and rigging allegations in a divisive presidential campaign.
Building a Web Malware Analyzer Using Machine Learning - Catch Me If You Can
Learn to build a web malware analyzer using machine learning. Explore infection methods, injected content, and scalable detection systems. Includes live demo and insights on web malware trends and prevention mechanisms.
Top 10 Web Hacking Techniques of 2013 - OWASP AppSecUSA 2014
Explore the top 10 innovative web hacking techniques of 2013, including Mutation XSS, BREACH, and HTML5 attacks. Learn about cutting-edge security vulnerabilities and their implications for web applications.
Static Analysis for Dynamic Assessments - OWASP AppSecUSA 2014
Explore techniques for using static analysis tools in dynamic web vulnerability assessments without source code, enhancing detection of security weaknesses in complex applications.
How to Spy with Python - Understanding PRISM and Cloud Security
Explore PRISM's impact on cloud services and learn strategies for securing data and preserving privacy in the cloud, with insights on leveraging cloud-based software while maintaining confidentiality.
OWASP Top 10 Mobile Risks: 2014 Reboot
Explore the updated 2014 OWASP Top 10 Mobile Risks, comparing changes since 2011, understanding new threats, and learning recommended fixes for iOS, Android, and Windows Phone platforms.
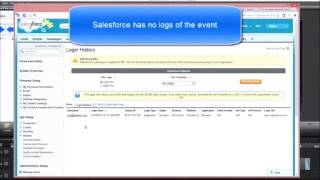
The Rise of SaaS-Targeted Malware - Zeus Variant Attacking Salesforce Users
Demonstration of a new Zeus malware variant targeting Salesforce users, showcasing its stealthy data exfiltration capabilities and discussing implications for SaaS security.