The Top 10 Web Hacks of 2014 - AppSec EU 2015
Explore the most significant web security vulnerabilities of 2014, presented by industry experts. Gain insights into attack vectors and learn essential defense strategies.
Maliciously Monetizing AppSec Features - It's All About the Money
Explore malicious monetization of AppSec features with Or Katz and Ezra Caltum. Learn about potential security vulnerabilities and their financial implications in application development.
The Internet of Broken Things - Future Challenges of Global Cybersecurity
Explore cybersecurity threats facing the US with Lisa O. Monaco, Obama's counterterrorism advisor. Discuss Russian hackers, Chinese spies, and IoT botnets, examining future challenges and opportunities for national security.
Red Team, Blue Team, or White Cell? Trends in IT Security - AppSec EU 2015
Explore trends in IT security, comparing red team, blue team, and white cell approaches, and how security must adapt to function like an immune system.
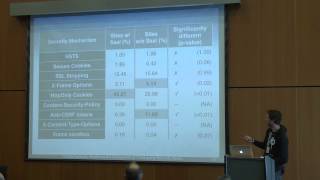
Issues and Limitations of Third Party Security Seals
Explore limitations of third-party security seals in web applications, uncovering potential vulnerabilities and discussing implications for online security practices.
AppSec EU 2015 Closing Ceremony
Closing remarks and highlights from AppSecEU 2015 in Amsterdam, covering key takeaways and future directions in application security.
The Software, Not the Human, Is the Weakest Link
Explore how software vulnerabilities, not human error, are the primary security risk in modern systems. Learn to shift focus from blaming users to improving code security.
Finding Bad Needles on a Worldwide Scale - Application Security
Explore techniques for identifying and locating malicious elements across global networks, enhancing cybersecurity practices and threat detection capabilities.
Agile Security Testing - Lessons Learned
Explore agile security testing strategies, challenges, and best practices for efficient integration of security in software development, based on real-world experiences and lessons learned.
Hard Knock Lessons on Bug Bounties
Insights and lessons learned from managing bug bounty programs, covering legal aspects, scope definition, program structure, and reward strategies for effective vulnerability disclosure.
Security is Part of the DNA of a Defense Organization
Explore how security is integral to defense organizations, from historical contexts to modern cyber operations and future conflict scenarios.
Copy Pest - A Case Study on the Clipboard, Blind Trust, and Invisible Cross-Application XSS
Explore clipboard vulnerabilities and cross-application XSS in this case study on invisible security threats and blind trust in web applications.
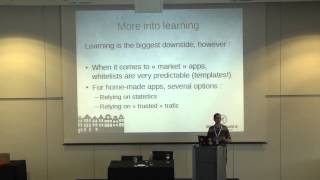
Naxsi: A Web Application Firewall for NGINX
Explore Naxsi, an open-source web application firewall for NGINX, and learn about its features, implementation, and benefits for enhancing web application security.
Security and Modern Software Deployment - AppSec EU 2015
Explore modern software deployment security challenges, including trust issues, dependencies, and repository vulnerabilities. Learn strategies to mitigate risks and enhance deployment security.
Making SSL Warnings Work - Improving Security and User Experience
Explore strategies to improve SSL warnings in Chrome, focusing on reducing false positives and enhancing user understanding of security threats through clear design and communication.
Monitoring Web Sites for Malware Injection with Web Detector
Explore WebDetector, a tool for monitoring websites and detecting malware injections. Learn about its components, heuristics, and effectiveness in identifying harmful elements on web pages.
Security Testing Windows Store Apps
Explore security testing for Windows Store Apps, focusing on HTML/JavaScript development, architecture, and potential vulnerabilities in this emerging application model.
Shameful Secrets of Proprietary Network Protocols
Reverse engineering proprietary protocols: case studies revealing security flaws in financial software, home automation, and embedded systems. Techniques for uncovering hidden vulnerabilities in undocumented binary protocols.

Lessons from Trusting JavaScript Cryptography - Biting into the Forbidden Fruit
Exploring real-world JavaScript cryptography implementations, debunking myths, and providing an updated perspective on JS crypto security through vulnerability analysis and practical examples.
Threat Modeling - A Brief History and the Unified Approach at Intuit
Unified approach to threat modeling combining STRIDE and asset-based methods. Focuses on identifying assets, attacker profiles, and controls for software architecture and system deployments.
OpenSAMM Best Practices - Lessons from the Trenches
Experts share insights on implementing OpenSAMM framework for software security, covering optimal maturity levels, integration with agile development, supplier management, and metrics for secure development lifecycle.