The Only Reason Security Matters for DevOps - APPSEC Cali 2018
Explore DevOps' impact on security, focusing on strategic business drivers, modern challenges, and practical recommendations for integrating security into DevOps using a simplified framework.
European Vacation: Leveraging GDPR for Security
Explore how GDPR compliance can drive security initiatives and automate processes, turning a potential burden into a win for application security.
OWASP Top 10 - Application Security Risks
Explore the latest OWASP Top 10 web application security risks with expert Andrew van der Stock. Learn about critical vulnerabilities and effective mitigation strategies for safer software development.

Beyond End-to-End Encryption: Threat Models for Secure Messaging
Explore evolving threat models for secure messaging, covering advanced attacker capabilities, real-world vulnerabilities, and emerging challenges in cybersecurity and privacy protection.
Five Key Trends in Application Security
Explore five crucial application security trends: cloud migration, CDN diversity, API proliferation, compliance challenges, and expanding attack surfaces. Gain insights into cybercriminal tactics and industry recommendations.
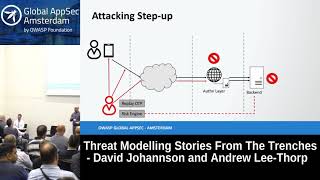
Threat Modeling Stories from the Trenches - Security Design Flaws and Solutions
Explore real-world threat modeling scenarios, design flaws, and security controls. Learn to identify vulnerabilities, understand attack vectors, and implement effective countermeasures in various systems.
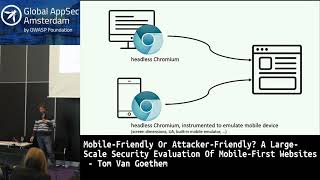
Mobile-First Websites Security Evaluation - Attacker-Friendly or User-Friendly?
Evaluate security vulnerabilities in mobile-first websites, exploring potential risks and attacker-friendly features. Learn to identify and mitigate threats in mobile web development.
How to Learn and Teach Hacking
Explore hacking techniques, competitions, and effective teaching methods for cybersecurity skills. Learn problem-based approaches and gain insights into CTF challenges and binary exploitation.
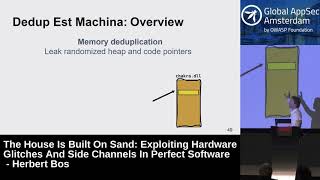
Exploiting Hardware Glitches and Side Channels in Perfect Software
Uncover vulnerabilities in flawless software through hardware glitches and side-channel attacks. Learn advanced exploitation techniques for enhancing cybersecurity defenses.
Secure Agile Development According to SAMM
Learn to integrate security into Agile development using SAMM principles. Explore challenges, practical solutions, and a hygiene approach for effective secure software development.
OWASP SAMM2 - Your Dynamic Software Security Journey
Explore OWASP SAMM2's dynamic approach to software security, enhancing your development practices and strengthening application defenses throughout the lifecycle.
A DevSecOps Tale of Business, Engineering, and People
Explore DevSecOps through a historical lens, examining its impact on business, engineering, and resilience. Learn from past challenges to build high-performing teams and implement effective DevSecOps strategies.
Talent Matters: Preventing Burnout and Building Strong AppSec Teams
Caroline Wong discusses preventing burnout, attracting talent, and growing strong application security teams in the face of industry challenges like talent shortages and increasing workloads.
Building an AppSec Program with a Budget of $0 - Beyond the OWASP Top 10
Explore OWASP projects to build a comprehensive AppSec program without spending money. Learn how to implement open-source tools for training, development, testing, and defense to create a robust security framework.
Gamifying Developer Education with CTFs
Explore how Capture The Flag challenges can be used to enhance developer security awareness through hands-on lessons in offensive security concepts, improving overall application security.
Winning - The Future Perspective in the Next 20 Years
Explore the future of application security with insights on emerging trends, challenges, and strategies for success over the next two decades.
The Perimeter Has Been Shattered - Mobile and IoT Security Challenges
Explore how mobility and IoT have disrupted traditional enterprise security, examining new threats and the limitations of current defenses. Learn practical strategies to improve mobile and IoT security in the modern landscape.
The Constitution and Supreme Court: Key Decisions and Impacts
Neal Katyal discusses key Supreme Court cases, constitutional issues, and their impact on modern society, covering topics like privacy, affirmative action, and religious freedom.

Jumpstarting Your DevSecOps Pipeline with IAST and RASP
Learn to create an effective DevSecOps pipeline using free tools like IAST and RASP. Gain real-time security feedback, continuous vulnerability analysis, and enhanced attack visibility for improved application security.
Effective Usage Analysis: The Shortest Path Between Developer and Accelerated Product Releases
Discover how effective usage analysis prioritizes vulnerabilities, enabling developers to focus on exploitable risks, streamline remediation, and accelerate product delivery.
No Room for Error - Advising the President on Homeland Security and Counterterrorism
Explore the challenges of homeland security and counterterrorism with Thomas Bossert, discussing strategies, risks, and the high-stakes nature of protecting national security in a post-9/11 world.