Death by 1000 Likes - Social Media Security Analysis at DEF CON
Explore how security researchers scraped r/defcon subreddit data to create an online version of the Wall of Sheep, revealing insights about information leakage in the security community.
Automatic Exploitation of TLS Certificate Validation Vulnerabilities
Explore TLS certificate validation vulnerabilities and their automated exploitation using certmitm, featuring real-world attacks on iOS and Windows 11 systems.
Nine Years of Overlooked MikroTik Pre-Authentication Remote Code Execution Vulnerabilities
Delve into RouterOS's overlooked attack surfaces and discover critical pre-auth RCE vulnerabilities that affected MikroTik devices for 9 years, with insights on detection methodology and security patterns.
Hacking PBX and UC Systems: Attack Surface Analysis and Vulnerability Discovery
Dive into enterprise PBX/UC system vulnerabilities, exploring attack surfaces, Java Runtime exploitation, PHP decryption, and shell access techniques in communication infrastructure.
Exploiting Cloud Connectivity to Compromise Network-Attached Storage Devices
Uncover critical security vulnerabilities in NAS devices through cloud connectivity exploitation, focusing on WD and Synology systems' authentication weaknesses and remote access vulnerabilities.
Attacking and Securing the Google Pixel Modem - Security Analysis and Vulnerabilities
Dive into mobile security as Android Red Team reveals their offensive evaluation techniques and findings on Pixel device modems, focusing on baseband vulnerabilities and protective measures.
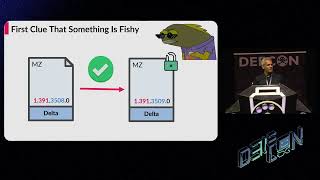
When Windows Defender Updates Become a Security Risk
Dive into Windows Defender's architecture and signature update vulnerabilities, exploring how unprivileged users can exploit security flaws to compromise Windows systems and manipulate EDR functionality.
A SSLippery Slope - Unraveling Hidden Dangers of Certificate Misuse
Uncover critical vulnerabilities in digital signature validation systems and learn how attackers can exploit certificate misuse to bypass security measures for signing untrusted code.
Civil Cyber Defense - Protecting Vulnerable Organizations Against Advanced Threats
Discover how civil cyber defenders protect vulnerable organizations, journalists, and activists using OSINT skills and open-source tools while combating human trafficking and surveillance threats.
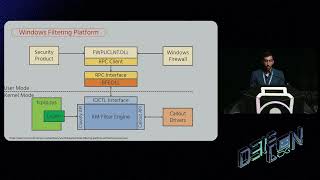
Abusing Windows Filtering Platform for Privilege Escalation - Undetected Attack Techniques
Discover an innovative Windows privilege escalation technique that exploits the Windows Filtering Platform, enabling stealthy system-level access through network traffic manipulation and kernel component abuse.

Advanced ROP Framework - Pushing Return-Oriented Programming to Its Limits
Discover advanced return-oriented programming techniques with ROP ROCKET framework, featuring syscall bypassing, cross-architecture exploitation, and innovative bad byte handling for enhanced security testing.
Email Spoofing and Domain Impersonation Through Cloud Services
Dive into advanced email security exploitation techniques, learning how to bypass SPF & DMARC through Cloudflare partnerships and serverless applications for domain spoofing.
Defeating VPN Always-On: Security Control Analysis and Bypass Methods
Discover security vulnerabilities in VPN Always-On implementations, exploring bypass techniques and hardening strategies for better network protection and data leak prevention.
Abusing CAN Bus Specifications for DoS Attacks in Embedded Systems
Explore CAN bus protocol vulnerabilities in automotive systems, focusing on how attackers can exploit metadata fields and protocol specifications to create denial-of-service attacks in embedded systems.
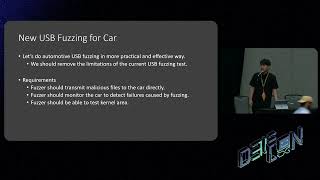
Automotive USB Fuzzing: Efficient Methods and Real-World Vulnerabilities
Dive into automotive USB fuzzing techniques and discover efficient methods for testing vehicle vulnerabilities through direct USB connections, featuring real-world case studies and practical demonstrations.
Contactless Overflow Code Execution Vulnerabilities in Payment Terminals and ATMs
Uncover critical NFC payment terminal vulnerabilities and their exploitation through contactless attacks, including ATM jackpotting techniques and firmware manipulation across major payment systems worldwide.
Terminally Owned - 60 Years of Terminal Escape Code Vulnerabilities
Explore terminal security vulnerabilities across platforms, from ASCII's escape character origins to modern exploit techniques, revealing critical remote code execution risks and defense strategies.
Vulnerabilities in Global Transportation Payment Systems - Security Risks and Exploits
Uncover critical security vulnerabilities in public transportation payment systems, focusing on Moovit's API weaknesses, unauthorized access risks, and solutions for protecting user data and preventing payment fraud.
Contextualizing The Vulkan Leaks and State-Sponsored Offensive Operations
Explore the implications of the Vulkan files leak, examining Russian cyber capabilities and their connection to global state-sponsored network warfare programs and automated exploitation systems.
Breaking BMC: The Forgotten Key to the Kingdom - Security Vulnerabilities in Baseboard Management Controllers
Dive into the security vulnerabilities of Baseboard Management Controllers (BMC), exploring exploit chains and firmware implants in NVIDIA hardware with AMI MegaRAC BMC implementation.
What Is a GRC Hacker - Understanding Governance, Risk, and Compliance Security
Discover the role and mindset of GRC (Governance, Risk, and Compliance) hackers in cybersecurity through expert insights and practical perspectives from DEF CON 31.