Centralized Product Security with Amazon Security Lake and Athena
Discover how to centralize security data management using Amazon Security Lake and AWS Athena, enabling unified schema conversion, comprehensive querying, and automated DevSecOps workflows.
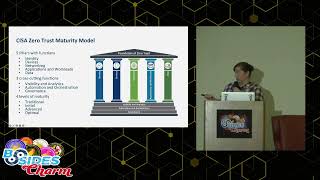
Measuring Your Zero Trust Maturity Using the CISA Framework
Discover how to assess and enhance zero trust architecture using CISA's Maturity Model, with practical insights from Centers for Medicare and Medicaid Services' implementation framework and tracking methods.
Detecting and Triaging Modern Windows Rootkits
Discover modern Windows rootkit detection techniques, memory forensics, and event log analysis methods to combat evolving kernel-level malware threats in Windows 10 and beyond.
The Action Group Model for Incident Response
Discover a flexible framework for coordinating incident response teams, improving support structures, and developing staff capabilities during security incidents.
Make Better Risk Decisions to Prevent Future Cyber Attacks
Discover proactive cybersecurity strategies for better risk decisions, focusing on preventative measures over reactive controls. Learn to identify vulnerabilities, assess business impact, and implement effective risk mitigation techniques.
Complexity for Complexity's Sake: The Bane of Cybersecurity Programs
Discover how to simplify cybersecurity approaches by avoiding tool overload and focusing on effective, streamlined solutions for better threat management and user experience in modern security programs.
Analysis of North Korean Nation-State Attacks Using MagicRAT Malware
Dive into North Korean APT group Lazarus's cyber-kill chain tactics, examining their MagicRAT malware and attack strategies against global energy companies through detailed MITRE ATT&CK analysis.
Evolving into the Next-Gen SOC - Baby Steps to the Future
Discover how to transform traditional Security Operations Centers into agile, next-generation entities capable of addressing modern cyber threats and future challenges through practical, actionable steps.
The Action Group Model for Incident Response
Discover a flexible framework for coordinating incident response teams, improving support structures, and developing staff capabilities during security incidents.
Active Directory and DNS: A Match Made in Heck - Understanding Directory Services Integration
Dive into the intricate relationship between Active Directory and DNS, exploring security implications, management strategies, and best practices for maintaining a robust directory service infrastructure.
Ten Ways to Frustrate Attackers in Network Security
Discover practical network security strategies and tools from a pentester's perspective to strengthen defenses and make attackers' work significantly more challenging and time-consuming.
Protecting Yourself From Supply Chain Attacks - Trust Is Overrated
Discover practical strategies and tools for validating hardware and software integrity, minimizing supply chain risks, and implementing effective security measures across your technology stack.
Blackbox Containers: Container Security in the Enterprise
Dive into container security fundamentals, lifecycle management, and enterprise-level best practices for securing containerized applications in modern development environments.
AI with a Security Mindset
Explore AI security challenges and opportunities with tech leader Elissa Shevinsky as she shares insights from her extensive experience in privacy, security, and cryptocurrency sectors.
Purple Teaming: Attack Simulation and Control Validation with Atomic Red
Discover how to leverage Atomic Red Team for simulating cyber attacks, validating security controls, and improving SOC effectiveness through practical demonstrations and MITRE framework mapping.
Windows System Monitor (Sysmon) for Incident Investigation and Threat Response
Master Windows System Monitor (Sysmon) for incident investigation, learning to track program execution, registry writes, and DNS queries to effectively trace threat actor activities and enhance system security.
Securing AI-Generated Code: Challenges and Solutions for the Future
Explore the critical challenges and solutions for securing AI-generated code, featuring practical tools and research for building AI security engineering capabilities.
Protect Your Most Sensitive Users with Protected Users Group in Windows Server
Discover how Windows Server's Protected Users Group safeguards sensitive accounts, learn its attack-thwarting capabilities, and implement practical strategies for enhanced security in Active Directory environments.
The Current State of Microsoft Identity Security - Common Security Issues
Explore modern identity security challenges in Microsoft environments, focusing on Active Directory and Azure AD vulnerabilities, recent breaches, and essential defensive strategies.
Network Segmentation Using Windows Host-Based Firewall and Group Policy
Master Windows network segmentation using Group Policy to deploy host-based firewall rules, control communication between security zones, and manage endpoints through Active Directory security groups.
Identifying and Securing Psychologically Vulnerable Users
Explore psychological traits that make users vulnerable to security threats and learn data-driven strategies to enhance organizational security and red team effectiveness.