Recon Methodology for Consistent High-Value Bug Bounties - Interview with Th3G3nt3lman
Discover effective recon methodologies for high-value bug bounties. Learn from @Th3G3nt3lman's experience in GitHub reconnaissance, tool usage, and collaboration strategies for successful hacking.
Live Bug Bounty Recon Session - Creating a Recon Database for Yahoo
Live session on bug bounty reconnaissance techniques and building a recon database for Yahoo, featuring guest @Daeken. Learn effective strategies for subdomain enumeration using multiple tools to enhance your bug hunting skills.
Live Bug Bounty Recon Session on Yahoo - Using Meg, Assetfinder, and Other Tools
Live bug bounty recon session demonstrating tools and techniques for reconnaissance on Yahoo, featuring guest @Tomnomnom. Covers creating wordlists, using meg and assetfinder, directory brute forcing, and crt.sh.
Live Bug Bounty Recon Session on Yahoo - Amass, crt.sh, and Dirsearch
Live bug bounty recon session demonstrating advanced techniques for discovering vulnerabilities on Yahoo, featuring tools like Amass, crt.sh, and dirsearch, with guest expert @TheDawgyg.
Live Bug Bounty Recon Session - August 18, 2019
Live bug bounty recon session covering techniques like JSParser, directory brute forcing, crt.sh, and API fuzzing. Expert guests share insights on effective reconnaissance strategies for ethical hacking.
Recon Methodology Using SecurityTrails, FDNS, Whoxy, and More
Explore codingo_'s unique recon methodology for ethical hacking, featuring tools like SecurityTrails, FDNS, and Whoxy to enhance your cybersecurity skills and bug bounty hunting techniques.
Live Recon and Google Dorking on the Department of Defense Vulnerability Disclosure Program
Explore live reconnaissance and Google dorking techniques on the Department of Defense's Vulnerability Disclosure Program, featuring insights from @thedawgyg.
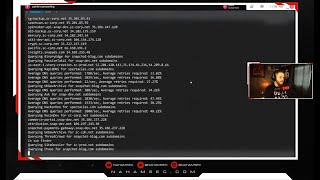
Live Recon on Snapchat - Demonstration of Amass, FFUF, and SecurityTrails
Explore live reconnaissance techniques on Snapchat using tools like amass, FFUF, and SecurityTrails in this hands-on demonstration with @ITSecurityGuard.
What Is a Social Engineering Attack?
Learn about social engineering attacks, their techniques, and how to protect against them in this informative cybersecurity lesson.
Armitage and Metasploit for Penetration Testing - From Information Collecting to Post Exploitation
Comprehensive overview of Armitage and Metasploit for penetration testing, covering information gathering, exploitation, and post-exploitation techniques through live demonstrations and practical examples.
CeH Unit 3: Footprinting and Scanning - Information Gathering and Network Mapping
Explore footprinting and scanning techniques for ethical hacking, including passive information gathering, DNS analysis, port scanning, and network mapping tools.
Leveraging Mobile Devices on Pentests - OISF 2013
Learn to leverage mobile devices in penetration testing with expert Georgia Weidman. Discover techniques and strategies for enhancing security assessments using smartphones and tablets.
Offensive OSINT
Explore offensive open-source intelligence techniques with Dr. Kandias, gaining insights into gathering and leveraging publicly available information for cybersecurity purposes.
Collecting Underpants to Win Your Network
Discover effective network penetration techniques and strategies to enhance your cybersecurity skills in this insightful presentation on ethical hacking and network defense.
DNS Reconnaissance Techniques - Derbycon 2012
Explore DNS reconnaissance techniques, including zone transfers, reverse lookups, and cache snooping. Learn to enumerate domains, parse data, and integrate findings with Metasploit for enhanced security assessments.
OWASP Nettacker Project Presentation
Explore OWASP Nettacker, an automated penetration testing framework for information gathering and vulnerability scanning in web applications and network infrastructure.
OSINT to Compromise - Techniques for Information Gathering
Explore OSINT techniques for ethical hacking and cybersecurity, learning how to gather and analyze open-source intelligence to identify vulnerabilities and enhance digital defense strategies.
OWASP Amass Project: DNS Enumeration and Network Mapping
Explore DNS enumeration and network mapping with OWASP Amass, a powerful tool for uncovering organizational internet presence and exposure using multiple data sources.
Seeing Around Corners - The Intelligence Professional's Challenge
Intelligence experts discuss strategies for anticipating and addressing unforeseen threats and challenges in national security, offering insights on navigating uncertainty in a complex global landscape.
reNgine - An Automated Reconnaissance Framework
Explore an automated reconnaissance framework for efficient cybersecurity assessments, enhancing vulnerability detection and streamlining security workflows.
OH-SINT: Merging OSINT Into Reverse Engineering Workflows to Simplify Analysis
Leveraging OSINT in reverse engineering to overcome anti-analysis techniques, track down information from developers, and speed up malware analysis workflows for quicker insights.