The First 48 - All Your Data Are Belong to Us
Explore digital forensics techniques for rapid data collection and analysis in critical incident response, emphasizing the crucial first 48 hours of an investigation.
Honey I Stole Your C2 Server - A Dive into Attacker Infrastructure
Explore attacker infrastructure through a Mandiant investigation, covering Metasploit indicators, command and control, encoding, and insights into attacker techniques and tools.
The Attack Is Coming From Inside The Refrigerator - Mark Boltz Robinson
Explore IoT security challenges and incident response strategies for connected devices like smart home appliances, focusing on volatility, tools, and emerging threats.
I Survived Ransomware TWICE
Learn from real-world ransomware experiences and discover effective prevention and recovery strategies to protect your organization's data and systems.
Marrying Incident Response and Threat Intel Within Your Enterprise
Explore strategies for integrating incident response and threat intelligence to enhance enterprise security and improve overall cybersecurity posture.
Estimating Development Security Maturity in About an Hour
Discover techniques for assessing development security maturity quickly. Learn to identify key behaviors, conduct effective meetings, and evaluate training, threat modeling, and analysis practices.
Delete Yourself - Cognitive Bias During Incident Response
Explore cognitive biases in incident response, learn effective strategies for handling security investigations, and understand the importance of flexible response plans and accurate log interpretation.
A Needle in the Cloud
Explore cloud incident response techniques, from preparation to log analysis and application forensics, enhancing your ability to detect and investigate security incidents in cloud environments.
Investigating Malware Using Registry Forensics
Explore malware detection and investigation techniques using Windows Registry forensics, covering key hives, detection methods, and tools for uncovering malicious activities.
Invoke CradleCrafter Moar PowerShell obFUsk8tion Detection Techniques
Explore advanced PowerShell obfuscation detection techniques with Daniel Bohannon, enhancing your ability to identify and analyze sophisticated evasion methods.
Securing Your Network - How to Prevent Ransomware Infection
Practical strategies to protect networks from ransomware, covering firewall configuration, security awareness, backups, and incident response. Emphasizes a proactive defense approach.
Cyber Mutual Assistance - A New Model for Preparing and Responding to Cyber Attack
Explore innovative strategies for cyber attack preparation and response through the concept of Cyber Mutual Assistance, offering a fresh perspective on collaborative cybersecurity.
The Pillars of Continuous Incident Response
Explore continuous incident response strategies, focusing on preparation, communication, and evolution. Learn to build robust capabilities and measure effectiveness in cybersecurity.
Changing Who Writes the Queries - High Leverage IR with Visual Playbooks
Explore visual playbooks for efficient incident response, leveraging automation and machine learning to streamline investigations and improve response times in cybersecurity.
Practical Incident Response in Heterogenous Environment
Explore practical incident response techniques in diverse environments, focusing on mass-triage, RIFT, FRAC, malware analysis, AIOCs, YARA rules, and ClamAV for effective threat detection and forensics.
Chasing the Adder - A Tale from the APT World
Explore advanced persistent threats through a real-world case study, uncovering sophisticated attack techniques and effective defense strategies in cybersecurity.
Changing the Game - The Impact of TRISIS TRITON on Defending ICS-SCADA-IIoT
Explore the impact of TRISIS/TRITON on defending industrial control systems, SCADA, and IIoT, and learn strategies to enhance cybersecurity in critical infrastructure.
Dear Blue Team - Proactive Steps to Supercharge Your IR
Discover proactive strategies to enhance incident response capabilities and strengthen your blue team's defensive posture in this insightful cybersecurity presentation.
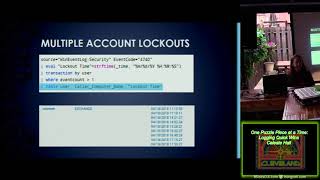
One Puzzle Piece at a Time - Logging Quick Wins
Discover effective logging strategies for quick security wins. Learn to identify and address password changes, account lockouts, unusual activities, and malicious domains.
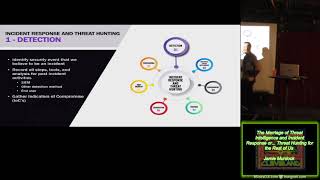
The Marriage of Threat Intelligence and Incident Response or Threat Hunting for the Rest of Us
Learn to integrate threat intelligence with incident response and threat hunting, exploring detection, analysis, containment, and eradication strategies for effective cybersecurity.
Structuring Your Incident Response Could Be One of the Most Important Things
Learn effective strategies for structuring incident response in cybersecurity, enhancing your ability to handle and mitigate security breaches efficiently.