Should I Worry? A Cross Cultural Examination of Account Security Incident Response
Exploring users' real-time responses to suspicious login incidents across cultures, revealing common patterns and unique challenges in digital security incident handling.
Tips on Building a World-Class Bug Bounty Program - Zenefits Red Team Insights
Learn from Zenefits' Red Team expert on building a top-tier bug bounty program. Gain insights on best practices, collaboration strategies, and maintaining program effectiveness for robust data protection.
Coordinated Vulnerability Disclosure Guide - AMA with CERT Authors
Insights on coordinated vulnerability disclosure from CERT Guide authors, covering principles, process improvement, and common challenges in cybersecurity reporting and management.
You're Under Cyber-Attack - Now What?
Experts discuss cyber-attack response strategies, focusing on information sharing, risk management, and preparedness. Key topics include critical infrastructure protection, cyber insurance, and handling advanced persistent threats.
The Role of Empathy in Vulnerability Disclosure Practices for Software Vendors - 2017
Explore empathy's role in vulnerability disclosure, focusing on cross-functional collaboration, customer-centric decision-making, and building trust through effective communication in software security.
Reservist Model - Distributed Approach to Scaling Incident Response
Discover Netflix's innovative Reservist Program for scaling incident response without massive headcount. Learn to build an auxiliary Crisis Manager pool to handle sporadic surges in security incidents efficiently.
Conducting Table Top Exercises for Cyber Incident Response Preparedness
Learn to conduct effective security table top exercises, using free resources to improve incident response preparedness and validate plans. Gain practical insights for enhancing team readiness against cyber threats.
The MITRE ATT&CK Framework: Understanding and Applying Adversarial Tactics - 2018
Explore the Mitre ATT&CK Framework to understand adversary tactics, detect threats, and improve cybersecurity defenses. Learn to map technologies, identify gaps, and enhance prevention strategies across various security roles.
SolarWinds - The Detailed Account of the Incident Response
Experts discuss the SolarWinds supply chain attack, analyzing SUNBURST and SUNSPOT, and offering insights into future cybersecurity challenges and protective measures for similar sophisticated threats.
Ransomware First Response
Learn essential strategies for responding to ransomware attacks, including incident response techniques, backup protocols, and security policy implementation.
Certified Wireless Security Professional - WLAN Security Policies
Learn essential WLAN security policies, incident response, and best practices for password security and mobile device management in this comprehensive overview.
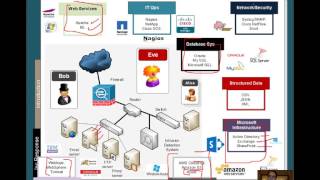
Introduction to Incident Response
Learn incident response fundamentals, including terminology, timelines, data analysis, risk models, and regular expressions for effective cybersecurity management.
Building Cyber Resilience with Microsoft Security Stack
Learn to develop a comprehensive cybersecurity strategy using Microsoft Security Stack. Gain insights on proactive measures and reactive actions to protect your organization from modern threats and enhance cyber resilience.
SIEM and XDR: Automating Threat Detection and Response
Explore Microsoft's integrated SIEM+XDR solution for advanced threat detection and automated response, designed to protect environments end-to-end and stay ahead of sophisticated adversaries.
Stories from DART - Taking the Ware Out of Ransomware
Practical strategies to reduce ransomware vulnerability, featuring real-world examples from Microsoft's DART team engagements. Learn simple yet effective measures to enhance your cybersecurity posture.
Threat Response with Microsoft Sentinel Playbooks - Learn Live
Explore Microsoft Sentinel's SOAR capabilities and create automated playbooks for efficient security threat response. Hands-on session with live expert guidance and audience interaction.
Threat Models for Exercising SIEM and Incident Response
Explore effective threat modeling techniques to enhance SIEM and incident response capabilities, improving overall cybersecurity preparedness and resilience.
Malware Analysis 101: From Novice to Expert in 60 Minutes
Learn essential malware analysis techniques, from basic to advanced, to enhance your cybersecurity skills and protect against digital threats.
The Great Trojan Demo - Understanding Remote Access Tools
Explore remote access tools, network security, and live Trojan demonstrations to understand potential threats and defensive strategies for protecting your digital infrastructure.
Cyber Security Incidents: Red Team vs Blue Team Tactics
Learn about Red Team/Blue Team cybersecurity exercises, incident response tactics, and best practices for defending against and simulating attacks. Gain insights from real-world scenarios and NIST framework implementation.
Advanced Breaches of 2013 vs Behavioral Detection - GrrCON 2014
Explore advanced breach detection techniques, comparing signature-based and behavioral methods. Learn about NetFlow, metadata analysis, and real-world case studies from 2013 attacks.