Applying DevOps Principles for Better Malware Analysis
Leveraging DevOps principles to streamline malware analysis, automate lab setup, and enhance collaboration among security researchers for more efficient threat detection and response.
Detectando RAT Malware en Teléfonos Celulares usando el IDS Slips
Detección de malware RAT en teléfonos Android utilizando el IDS Slips, una herramienta innovadora del laboratorio Stratosphere para proteger a personas en riesgo de ataques silenciosos y difíciles de detectar.
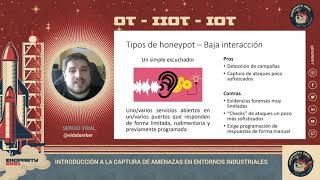
Introducción a la Captura de Amenazas en Entornos Industriales
Exploración de la captura de amenazas en entornos industriales, abordando tecnología operacional, ciberseguridad en ICS, honeypots y estrategias para proteger sistemas industriales.
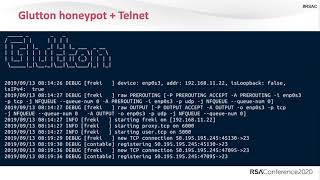
My Botnet Always Beats Yours - A Honeypot to Massive Bot Fight Scenes
Explore the fascinating world of IoT botnets through threat hunting stories, uncovering dramatic fight scenes between botnet herders and their evolving tactics in the dark web.
Data Transforming Your Sewage into Signatures
Transforming honeypot data into valuable security insights through innovative data analysis techniques. Learn to extract meaningful patterns and create effective signatures from seemingly useless information.
Creating a Buzz - Tales of Building WordPress Honeypots at Scale
Explore the world of WordPress honeypots, their deployment at scale, and surprising insights into black-hat tactics in this intriguing cybersecurity presentation.
From Threat Intelligence to Rapsheets in Just a Few Steps - DefCamp - 2016
Explore threat intelligence transformation into actionable data using innovative techniques like honeypots, passive DNS, and graph-based models for enhanced cybersecurity analysis and decision-making.
HoneySAP - Who Really Wants Your Money
Explore HoneySAP, a honeypot system for SAP environments. Learn about its goals, components, and implementation to enhance security and gather threat intelligence.
Using Blue Team Techniques in Red Team Ops
Innovative techniques for advanced red team operations, including infrastructure management, blue team detection, and dynamic adjustments to enhance effectiveness and evasion.
Open Source Security Orchestration
Explore open-source security orchestration using Adaptive Network Protocol (ANP) for efficient threat response, automated network defense, and improved visibility across multiple systems and clouds.
Applied Deception Beyond the Honeypot - Moving Past 101
Explore advanced deception techniques beyond honeypots for cybersecurity, drawing insights from military and political strategies to enhance defensive capabilities against diverse adversaries.
Identifying the Scan and Attack Infrastructure Behind Amplification DDoS Attacks
Explore techniques to identify infrastructure behind amplification DDoS attacks, including scanning, honeypots, and trilateration methods for improved cybersecurity defenses.
Critical Infrastructure Network Attacks - Code Red, Alert Network Operators
Analyze new tactics used by cybercriminals targeting critical infrastructure with multistage ransomware attacks, focusing on electric transmission substation vulnerabilities and incident timelines.
You See Honey, I See Beehive - Developing Honey Networks
Explore end-to-end honey networks for breach defense, combining honeypots, security sensors, and continuous monitoring. Learn open-source and enterprise options for networks of any size.
The Art of The Scam - Demystifying Honeypots in Ethereum Smart Contracts
Explores honeypot smart contracts in Ethereum, their prevalence, and impact. Presents HoneyBadger tool for detecting honeypots, analyzing 2M+ contracts and identifying 690 honeypots with 240 victims.
Hey Attacker! I Can See You!
Exploring cloud-scale deception technology to track and analyze attackers, enhancing Azure security through psychological and technical approaches for better threat intelligence and user protection.
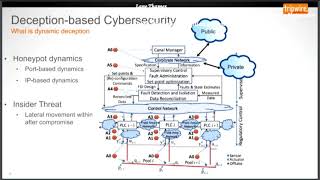
Honeypots 2.0 - A New Twist on Defending Enterprise Networks
Explore dynamic deception at scale using Python's Twisted framework for enhanced network defense, focusing on scalable honeypot technologies and their implementation in enterprise environments.
Bring Back the Honeypots
Explore modern honeypot techniques for enhanced network security. Learn about application traps, booby-trapped documents, and cloud-based deception to detect and prevent breaches effectively.
Alternatives to Honeypots or The DTK
Explore alternatives to honeypots and the Deception Toolkit (dtk) for network security, discussing innovative strategies to detect and deter cyber threats.
Honeypots for Active Defense
Explore active defense strategies using honeypots. Learn about various honeypot types, implementation techniques, and tools for enhancing network security and threat intelligence.
Honeypots, I Shrunk The Data
Explore innovative techniques for reducing honeypot data volume while maintaining its effectiveness in cybersecurity threat detection and analysis.