Preventing DMA Attacks from Thunderbolt Devices
Explore security vulnerabilities in Thunderbolt connections and learn effective strategies to prevent DMA attacks from malicious peripherals on Linux systems.
Exploring I/O Support for Virtualization-Based Trusted Execution Environments
Explore I/O support options for Trusted Execution Environment VMs, discussing software, hardware, and device requirements for secure data processing in confidential computing workloads.
Supporting TEE on x86 Client Platforms with pKVM
Explore x86 pKVM implementation for isolated TEE VMs, covering design, requirements, and integration with host OS. Learn about architecture, performance, and future developments.
Shhh - Stop Sharing Secrets: A Secure Mindset for Embedded Development
Explore secure embedded development practices, focusing on encryption, authentication, and trusted execution environments to protect IoT devices and data.
How to Effectively Test Transient Execution Mitigations
Explore transient execution vulnerability testing methods, challenges, and future improvements for effective mitigation in software and hardware systems.
Hardware Protections Against ROP Attacks
Explore hardware-based defenses against Return-Oriented Programming (ROP) attacks with IBM expert Mike Rapoport, focusing on cutting-edge security measures for system protection.
Secure Boot - What Is It and Do I Need It?
Explore secure boot in IoT: its components, use cases, threats it prevents, and implementation status. Learn key elements for supporting secure boot in connected devices.
New Tales of Wireless Input Devices
Explore security vulnerabilities in wireless input devices and learn about potential attack vectors and countermeasures for enhanced cybersecurity awareness.
Practical and Affordable Side-Channel Attacks
Explore affordable side-channel attacks with practical demonstrations, learning techniques to exploit vulnerabilities in cryptographic implementations and secure systems.
Growing SPIFFE and SPIRE in 2023 and Beyond - Secure Identity Management Progress
Explore SPIFFE/SPIRE's latest advancements in secure identity management, including Windows support, SIGSTORE integration, and enhanced hardware security, empowering enterprises with robust infrastructure protection.
KeyBleed: Attacking the OneKey Mini Cryptocurrency Wallet - Hack In The Box 2023
Revealing vulnerabilities in cryptocurrency hardware wallets, focusing on the OneKey Mini's security flaws. Demonstrates live exploit to extract and crack the seed, recovering stored funds in under one second.
Hardware Backdooring an eScooter - ECU Vulnerabilities and Remote Control
Explore e-scooter ECU vulnerabilities and hardware implant attacks. Learn reverse engineering techniques for CANBUS messages and remote access exploitation in this cybersecurity deep dive.
Integrity Measurement Architecture in Linux Systems
Explore Linux system integrity with IBM engineer Mimi Zohar, covering key concepts and techniques for ensuring secure and reliable software environments.
TPM: History, Updates, and Future Developments
Explore TPM's history, updates, and future developments with Intel's Jarkko Sakkinen. Learn the basic idea and sequence diagram of this crucial technology.
Design and Implementation of a Security Architecture for Critical Infrastructure Industrial Control Systems
Comprehensive security architecture for critical infrastructure, addressing nation-state cyber threats. Covers hardware roots of trust, secure boot, and integrity measures across various systems and networks.
AMD x86 Memory Encryption Technologies - Secure Memory Encryption and Virtualization
Explore AMD's x86 memory encryption technologies: Secure Memory Encryption for physical access protection and Secure Encrypted Virtualization for isolated encrypted virtual machines. Learn about architecture, security benefits, and Linux implementation.
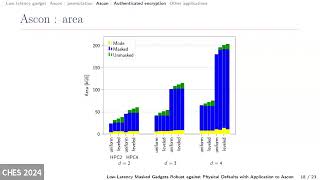
Gadgets II - Advanced Cryptographic Hardware Techniques
Explore advanced cryptographic hardware techniques and implementations in this CHES 2024 session, chaired by Rei Ueno.
TrustZone-M Security Vulnerabilities in Microcontroller TEEs - Lessons Learned
Explore TrustZone-M security vulnerabilities in Arm Cortex-M MCUs. Uncover isolation weaknesses, bypass techniques, and potential exploits in microcontroller Trusted Execution Environments.
The Hack@DAC Story - Learnings from Organizing the World's Largest Hardware Hacking Competition
Explore insights from organizing Hack@DAC, the world's largest hardware hacking competition. Learn about unique aspects, value for the security community, and key takeaways for industry, academia, and researchers.
Inside Apple's Lightning: JTAGging the iPhone for Fuzzing and Profit
Explore Apple's Lightning protocol, learn iPhone JTAGging techniques, and discover fuzzing methods for potential vulnerabilities and profit.
How the Silicon Commons, Developed Through OpenTitan, Is Revolutionizing Chip Design
Explore how OpenTitan's Silicon Commons is transforming chip design, revolutionizing the industry with open-source hardware and collaborative innovation.