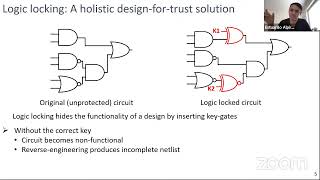
White Box, Obfuscation, and Logic Locking
Explore white box cryptography, obfuscation techniques, and logic locking methods to enhance hardware and software security against reverse engineering and tampering.
Fault Resistance II
Explore advanced fault resistance techniques in cryptographic hardware at this CHES 2024 session, chaired by Naofumi Homma.
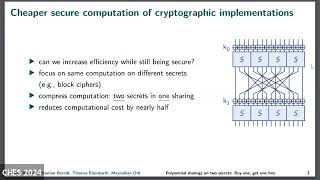
Masking Faults in Cryptographic Hardware - CHES 2024 Session
Explore fault-resistant masking techniques in cryptographic hardware, examining cutting-edge research and implementations presented at CHES 2024.
Side-Channel Analysis: Power-Based Attacks - CHES 2024
Explore advanced techniques in side-channel analysis focusing on power-based attacks, presented by experts at a leading cryptographic hardware conference.
Leakage in Cryptographic Hardware and Embedded Systems
Explore cutting-edge research on leakage in cryptographic hardware and embedded systems at this CHES 2024 session, chaired by Thorben Moos.
Side-Channel Analysis Advancements - CHES 2024
Explore advanced side-channel analysis techniques and their applications in cryptography at this CHES 2024 session, chaired by Shivam Bhasin.
Machine Learning - CHES 2024
Explore cutting-edge applications of machine learning in cryptography and hardware security at this CHES 2024 session, chaired by Fatemeh Ganji.
Glitches in Cryptographic Hardware - CHES 2024 Session
Explore cutting-edge research on glitches in cryptographic hardware at CHES 2024, chaired by Shahin Tajik. Gain insights into the latest developments and potential vulnerabilities in secure systems.
Exposing and Exploiting AACSv2 UHD DRM - Full AACSess
Exposing vulnerabilities in AACSv2 DRM for UHD Blu-ray, including side-channel attacks on Intel SGX, leading to the first full compromise and unofficial playback of UHD-BD discs.
Hi-Intensity Deconstruction: Chronicles of a Cryptographic Heist
Delve into groundbreaking research revealing security vulnerabilities in HID's iCLASS SE platform, exploring reverse engineering techniques and critical mitigation strategies for electronic access control systems.
Unlocking Hardware Security - Red Team, Blue Team, and Trojan Tales
Explore hardware Trojan detection in ICs through a Red Team vs. Blue Team case study. Learn about imaging techniques, algorithm efficiency, and the impact of technology scaling on security.
Secure and Encrypted Boot in Zephyr RTOS Using Hardware Keys and TrustZone
Explore secure booting implementation in Zephyr RTOS using MCUboot, hardware keys, and encryption features like HAB and TF-M for enhanced embedded system security and tamper protection.
INSIGHT: Attacking Industry-Adopted Learning Resilient Logic Locking Techniques Using Explainable Graph Neural Network
Discover how INSIGHT, an explainable Graph Neural Network attack method, breaks through learning resilient logic locking techniques used in hardware security and IP protection.
Intellectual Property Exposure: Subverting and Securing Intellectual Property Encapsulation in Texas Instruments Microcontrollers
Explore security vulnerabilities in Texas Instruments MSP430 microcontrollers' IPE technology and learn practical attack scenarios plus proposed hardware solutions for enhanced protection.
AttackGNN: Red-Teaming GNNs in Hardware Security Using Reinforcement Learning
Discover how reinforcement learning can generate adversarial examples to challenge GNN-based hardware security systems, demonstrating vulnerabilities in IP piracy detection and Trojan identification methods.
ZenHammer: Rowhammer Attacks on AMD Zen-based Platforms
Discover the first successful Rowhammer attack implementation on AMD Zen processors, exploring reverse engineering techniques, synchronization methods, and exploitation of DDR4/DDR5 memory vulnerabilities.
Go Go Gadget Hammer: Flipping Nested Pointers for Arbitrary Data Leakage
Explore a novel Rowhammer exploit technique targeting nested pointer dereferences in code patterns, demonstrating enhanced data leakage capabilities and improved attack primitives in Linux kernel security.
SpecLFB: Eliminating Cache Side Channels in Speculative Executions
Discover how SpecLFB leverages Line-Fill-Buffer to eliminate cache side-channel vulnerabilities in speculative executions, offering an efficient defense mechanism with minimal performance impact.
DMAAUTH: A Lightweight Pointer Integrity-based Secure Architecture to Defeat DMA Attacks
Explore a lightweight pointer integrity-based architecture that provides enhanced DMA attack protection while maintaining performance, demonstrated through FPGA implementation and cross-architecture evaluation.
Neural Network Extraction Through Physical Side Channels - A Systematic Review
Explore physical side-channel analysis attacks on deep neural networks, examining threat models, attack methodologies, and practical limitations for model extraction and input recovery on hardware accelerators.
Basilisk: Remote Code Execution by Laser Excitation of P-N Junctions Without Insider Assistance
Discover how laser-based attacks can manipulate P-N junctions to achieve remote code execution and system interference, exploring practical demonstrations and potential countermeasures for hardware security.