What Happened to Your Home - IoT Hacking and Forensic with 0-Days
Explore IoT device vulnerabilities, hacking techniques, and forensic analysis in smart homes. Learn about zero-day exploits and their impact on home security.
Beyond Windows Forensics with Built-in Microsoft Tooling
Explore advanced Windows forensics techniques using native Microsoft tools, enhancing your ability to investigate and analyze digital evidence effectively.
Möglichkeiten der Enttarnung steganographischer Kommunikation im Medium natürlicher Sprachen
Diskussion über Methoden zur Erkennung versteckter Botschaften in natürlicher Sprache, einschließlich Merkmale, Enttarnungsansätze und Gegenmaßnahmen für klandestine Kommunikation.
Leveraging Osquery for DFIR at Scale
Explore efficient incident response using Osquery for digital forensics, accelerating breach investigations and uncovering attacker breadcrumbs in large-scale environments.
The Metabrik Platform - Rapid Development of Reusable Security Tools
Explore the Metabrik Platform for rapid security tool development. Learn to create reusable components, improve existing tools, and solve complex security challenges efficiently.
Flash Storage Forensics
Explore flash storage forensics techniques, including spare area analysis, wear leveling, and flash translation layers, to enhance criminal investigation capabilities.
Abusing Bash for Windows
Explore techniques for exploiting Bash on Windows, including remote shells, password extraction, and AppLocker bypasses. Learn about security implications and forensic considerations.
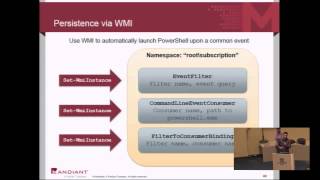
Investigating PowerShell Attacks
Explore PowerShell attack techniques, forensic artifacts, and investigation methods for detecting and mitigating threats in Windows environments.
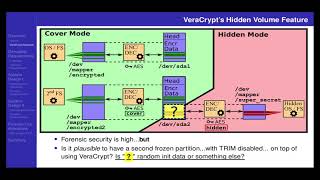
Perfectly Deniable Steganographic Disk Encryption
Explore self-concealing, deniable encryption techniques similar to VeraCrypt's hidden volume feature, covering design, implementation, and forensic analysis considerations.
Monokle - Mobile Surveillanceware with a Russian Connection
Explore the sophisticated Monokle mobile surveillanceware, its deployment by nation-states, and its attribution to a Russian contractor. Learn about trends in advanced mobile surveillance technology development.
A Surprise Encounter With a Telco APT
Exposé of a sophisticated telco hack, revealing methodologies, tools, and protocols used by a suspected state actor. Insights from a live session observation and forensic analysis of a mobile network operator intrusion.
Lessons from Virginia - A Comparative Forensic Analysis of WinVote Voting Machines
Forensic analysis of WinVote machines reveals security flaws and vulnerabilities in electronic voting systems, highlighting the importance of robust election technology and auditing processes.
Rocking the Pocket Book - Hacking Chemical Plant for Competition and Extortion
Explore techniques for exploiting chemical plant systems to cause economic damage while avoiding detection. Learn about attack stages, cost considerations, and creating misleading forensic evidence.
Chkrootkit - Eating APTs for Breakfast Since 1997
Explore Chkrootkit's 20-year journey in detecting rootkits and malware. Learn about its features, methods, and potential improvements in this informative security talk.
Kiss from a Rogue - Evaluating Detectability of Pay-at-the-Pump Card Skimmers
Explore the effectiveness of security measures against card skimmers at gas pumps, including consumer-facing indicators and detection apps, through comprehensive analysis and real-world data.
Cunning With CNG - Soliciting Secrets From Schannel
Explore Schannel's internal security, CNG key caching, and forensic implications. Learn to extract and leverage TLS/SSL connection data for decryption and analysis of ephemeral key exchanges.
Forensic Examination of Ceph
Explore forensic techniques for Ceph storage systems, focusing on data recovery, artifact analysis, and security implications in distributed environments.
SAP Anti-Forensics - Detecting White-Collar Cyber-Crime
Explore SAP forensics techniques for detecting white-collar cybercrime, focusing on anti-forensics methods and investigative strategies in enterprise environments.
Forensic Analysis of Android Banking Apps
Forensic analysis techniques for Android banking apps, covering memory forensics, code analysis, and package repackaging attacks. Insights into methodology, experimental results, and future research directions.
Paging All Windows Geeks – Finding Evil in Windows 10 Compressed Memory
Explore Windows 10 memory compression implementation, undocumented structures, and algorithms to enhance forensic tools for detecting malicious activities in compressed memory.
Investigating PowerShell Attacks
Explore techniques used by attackers to exploit PowerShell for command-and-control, lateral movement, and persistence. Learn to collect and interpret forensic evidence from real-world incidents.