A New Secret Stash For Fileless Malware
Explores advanced fileless malware techniques using Windows event logs for code hiding and infection. Reveals new methods to conceal shellcode and manipulate logging functions.
A Deep Dive Into Unconstrained Code Execution on Siemens S7 PLCs
Explore unconstrained code execution on Siemens S7 PLCs, revealing bootloader vulnerabilities and security implications. Learn about the special access feature and its potential for exploitation or forensic use.
Messenger Hacking - Remotely Compromising an iPhone through iMessage
Detailed exploration of a remote iPhone exploit via iMessage, covering vulnerability analysis, exploitation techniques, and mitigation strategies for mobile OS and messenger security.
Journey to Command Injection - Hacking the Lenovo ix4-300d
Demonstration of chaining vulnerabilities to remotely exploit a Lenovo NAS device, showcasing command injection, XSS, and CSRF techniques for full system compromise.
Abusing WCF Endpoint for RCE and Privilege Escalation
Explore WCF vulnerabilities in .NET programs, focusing on privilege escalation and remote code execution. Learn to identify and exploit these bugs through a real-world case study.
Researching Android Device Security with the Help of a Droid Army
Explore Android device security using a diverse cluster, addressing fragmentation challenges and enabling efficient vulnerability research and testing across multiple devices.
Exploits with Scratch
Explore network exploitation using Scratch programming language, extending its capabilities to create exploits and fuzz vulnerable services through custom TCP/IP function blocks.
ARM Assembly and Shellcode Basics - Workshop
Comprehensive workshop on ARM assembly and shellcode creation, covering basics, execve() shell, and reverse shell. Includes hands-on practice with QEMU emulator and Raspberry Pi hardware.
Dial V for Vulnerable - Attacking VoIP Phones
Explore VoIP phone vulnerabilities, attack methods, and security recommendations. Learn firmware access, emulation approaches, and exploit development for various VoIP devices.
Make ARM Shellcode Great Again
Explore ARM shellcode techniques, from basic execve() to advanced "Quantum Leap" code, covering tight spaces, mprotect egghunters, and ARM-Thumb switching for efficient exploitation.
How We Analyzed and Built an Exploit PoC for CVE-2022-24086, a Magento RCE - Catalin Filip - DefCamp - 2022
Explore the analysis and exploit development for CVE-2022-24086, a critical Magento RCE vulnerability, presented by a security researcher at DefCamp 2022.
The Layman's Guide to Zero-Day Engineering
Demystifying zero-day exploit development: insights into the engineering process, analytical approaches, and misconceptions. Contrasts with CTF challenges and guides aspiring security professionals.
How I Hacked My City - DefCamp 2016
Explore urban hacking through a real-world case study of Tel Aviv's open WiFi network, uncovering vulnerabilities and demonstrating practical exploitation techniques.
Digital Vengeance - Exploiting Notorious C&C Toolkits
Explore techniques for exploiting notorious Remote Administration Tools used in targeted attacks, turning the tables on sophisticated adversaries and exposing vulnerabilities in their command and control systems.
Exploit Generation and JavaScript Analysis Automation with WinDBG
Automate exploit generation and JavaScript analysis with WinDBG. Learn techniques for creating exploits from PoC crashes and tracking obfuscated JavaScript without triggering anti-debugging measures.
ECOS Offensive Security Research Logbook
Explore eCos RTOS security, from firmware analysis to exploitation and persistence. Learn techniques for cable modem research, including memory corruption, shellcode development, and implant creation.
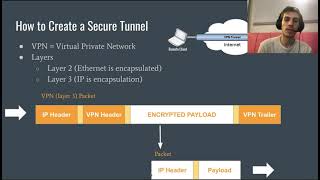
All Roads Lead to OpenVPN Pwning Industrial Remote Access Clients - Sharon Brizinov - Hack in Paris - 2021
Uncover critical vulnerabilities in industrial remote access solutions using OpenVPN, potentially leading to remote code execution. Learn about the risks and implications for cybersecurity.
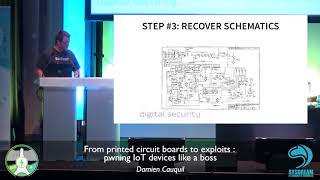
From Printed Circuit Boards to Exploits: Pwning IoT Devices Like a Boss - Damien Cauquil - Hack in Paris - 2018
Explore hardware hacking of a Bluetooth smartlock, from circuit board analysis to exploit development, covering electronics basics, reverse engineering, and mobile app vulnerabilities.
Case Studies in Embedded VR - Silvio Cesare - Ekoparty Security Conference - 2022
Explore cutting-edge techniques in embedded VR security, focusing on router vulnerabilities, reverse engineering, and exploit development through real-world case studies.
How to Cook Cisco: Exploit Development for Cisco IOS - George Nosenko - Ekoparty Security Conference - 2017
Exploración técnica de vulnerabilidades en Cisco IOS, incluyendo bypass de DEP, ROPing, shellcode en etapas y evasión de mecanismos de integridad. Incluye demostraciones prácticas y código fuente.
Chainsaw - Chained Automated Workflow-based Exploit Generation
Explore automated workflow-based exploit generation for web applications using Chainsaw, a novel approach to identify and exploit vulnerabilities through informed traversal and workflow inference.