The Anatomy of an Exploit
Explore exploit development through C and x86_64 assembly, gaining insights into security vulnerabilities and the attacker's perspective for more secure coding practices.
PPLdump Is Dead - Long Live PPLdump
Explore Windows Protected Process Light (PPL) mechanism, its vulnerabilities, and historical exploits. Learn about PPLdump, its impact on system security, and Microsoft's approach to PPL-related vulnerabilities.
Exploiting a Slightly Peculiar Volume Configuration with SIG-Honk
Dive into SIG-Honk's exploit development process for CVE-2021-30465, exploring methodology, demonstration, and insights on staying informed about Kubernetes vulnerabilities.
Exploiting Security Vulnerabilities in Microhard Radio Equipment
Uncover critical security vulnerabilities in Microhard's radio equipment, including command injections and buffer overflows, while exploring implications for SCADA and utility systems.
Prototype Pollution Leading to Remote Code Execution in NodeJS
Delve into prototype pollution vulnerabilities in Node.js, exploring how they enable remote code execution, analyzing real-world exploits, and understanding recent security mitigations.
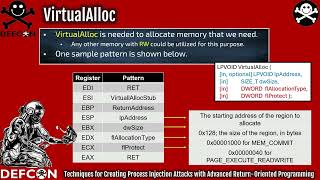
Process Injection Attacks with Return-Oriented Programming - Advanced Techniques and Methodologies
Discover advanced process injection techniques using return-oriented programming (ROP), including unique string comparison solutions, multiple WinAPI patterns, and practical methodologies for reliable implementation.
Cracking the Lens - Targeting HTTP's Hidden Attack-Surface
Explore hidden attack surfaces in modern web infrastructure, focusing on transparent systems for performance and analytics. Learn to identify and exploit overlooked vulnerabilities.
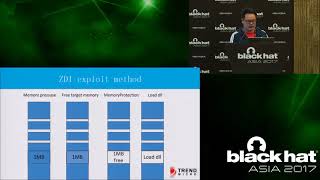
Cross the Wall - Bypass All Modern Mitigations of Microsoft Edge
Explore techniques to bypass ASLR, DEP, and CFG exploit mitigations in Microsoft Edge on Windows 10, even with arbitrary address read/write capabilities.
Return Oriented Programming, an Introduction
Explore Return Oriented Programming (ROP) exploitation technique, its mechanics, and practical examples for executing code in non-executable stack contexts.
Demystifying Thread Call Stack Spoofing - Advanced Techniques for Stack Manipulation
Dive into advanced thread stack spoofing techniques, combining stack frames forging with ROP and JOP to achieve stealthy module execution and call stack manipulation.
Fuzzing - Finding Your Own Bugs and Zero-Days
Master the art of fuzzer creation and vulnerability discovery, exploring buffer overflow exploitation techniques with hands-on demonstrations and practical exploit development strategies.
New Isn't Always Novel - Finding Basic Vulnerabilities in Enterprise Software
Discover how basic vulnerabilities in enterprise software led to a successful Pwn2Own contest entry, featuring a command injection exploit in Lexmark printers and practical security insights.
Retro Exploitation - Vintage Computing as a Vulnerability Research Playground
Explore vulnerability research and exploit development through vintage computing, focusing on the Commodore Amiga platform and practical demonstrations of retro software exploitation techniques.

Advanced ROP Framework - Pushing Return-Oriented Programming to Its Limits
Discover advanced return-oriented programming techniques with ROP ROCKET framework, featuring syscall bypassing, cross-architecture exploitation, and innovative bad byte handling for enhanced security testing.
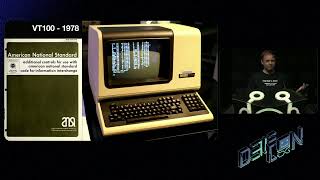
Terminally Owned - 60 Years of Terminal Escape Code Vulnerabilities
Explore terminal security vulnerabilities across platforms, from ASCII's escape character origins to modern exploit techniques, revealing critical remote code execution risks and defense strategies.
Incubated ML Exploits: Backdooring Machine Learning Pipelines with Input Handling Bugs
Explore machine learning pipeline vulnerabilities and learn to identify, exploit, and defend against model backdoors through input handling bugs and systematic security approaches.
Exploiting Bluetooth Vulnerabilities: From Car Systems to Bank Account Security
Discover how to identify and exploit Bluetooth vulnerabilities in modern vehicles and flight systems, using BlueToolkit framework for testing, with practical tips and new attack vectors for security research.
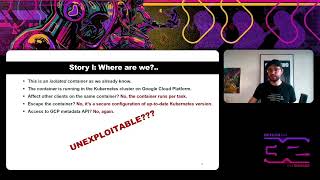
Exploiting the Unexploitable - Advanced JavaScript Vulnerability Chains in Kibana
Dive into advanced exploitation techniques for JavaScript vulnerabilities, focusing on Prototype Pollution attacks and RCE chains through real-world Kibana Bug Bounty examples and defense strategies.

The Darkest Side of Bug Bounty - Understanding Problems and Solutions in Bug Bounty Programs
Uncover the hidden challenges, secrets, and realities of bug bounty programs through expert insights on navigating relationships between hunters, clients, and platforms.
The Hack, the Crash and Two Smoking Barrels - Automotive Cybersecurity Challenges
Dive into automotive cybersecurity challenges through real-world stories and demonstrations, exploring vehicle architecture vulnerabilities and industry practices while witnessing live ECU hacking and security testing scenarios.
Xiaomi Mobile Security Vulnerabilities - Regional Exploit Analysis and Pwn2Own Competition
Delve into the behind-the-scenes journey of exploiting Xiaomi 13 Pro at Pwn2Own Toronto 2023, exploring regional security variations and the challenges of mobile device exploitation.