Exploiting a Limited UAF on Ubuntu 22.04 to Achieve LPE
Detailed exploration of exploiting a Linux kernel vulnerability in Ubuntu 22.04 to achieve local privilege escalation, focusing on advanced exploitation techniques and bypass methods.
E'rybody Gettin' TIPC - Demystifying Remote Linux Kernel Exploitation
Demystifying remote Linux kernel exploitation through a stack overflow vulnerability in a network module, offering insights into the exploit development process and low-level kernel internals.
Attacking WPA3 - New Vulnerabilities And Exploit Framework
Uncovers critical vulnerabilities in WPA3, including DoS attacks and traffic interception. Presents a new Wi-Fi testing framework for researchers to identify and exploit these weaknesses in various devices.
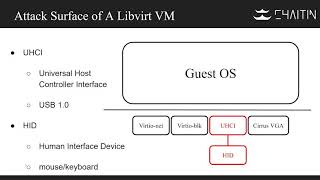
A QEMU Black Box Escape Via USB Device
Exploring a QEMU virtual machine escape technique using USB device vulnerabilities, focusing on black box scenarios without prior system information for enhanced cloud security.
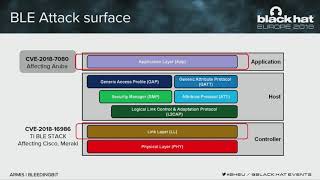
BLEEDINGBIT - Your APs Belong to Us
Explore zero-day vulnerabilities in BLE chips, allowing unauthenticated network penetration. Learn about BLEEDINGBIT, its impact on enterprise APs, and potential attack scenarios.
All the 4G Modules Could Be Hacked
Explores vulnerabilities in 4G modules, demonstrating methods to probe and exploit weaknesses in car entertainment systems for remote control of vehicles.
Compromising the macOS Kernel through Safari by Chaining Six Vulnerabilities
Explore a Safari exploit chaining six vulnerabilities to compromise the macOS kernel. Learn about offensive security research and browser-based kernel exploitation techniques.
Escaping Virtualized Containers
Explore container security, focusing on shared kernel vulnerabilities that may allow processes to escape and compromise the host system. Learn about potential risks and mitigation strategies.
Attacking VxWorks - From Stone Age to Interstellar
Explore vulnerabilities in VxWorks, a real-time operating system, from historical exploits to cutting-edge attack techniques. Gain insights into securing critical infrastructure and embedded systems.
Reverse Engineering and Exploiting Font Rasterizers - The OpenType Saga
Explore critical vulnerabilities in OpenType font handling across popular software, revealing potential for arbitrary code execution and bypassing exploit mitigations. Learn about reverse-engineering techniques and in-depth vulnerability analysis.
Stegosploit - Drive by Browser Exploits Using Only Images
Innovative technique encoding browser exploits in images, combining steganography and polyglots for undetectable delivery. Explores implementation, challenges, and implications for cybersecurity.
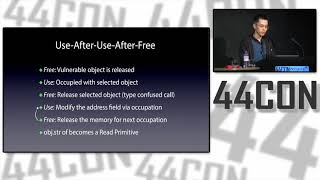
Leverage One-shot UAF to a Minigun
Exploración de técnicas avanzadas de explotación de vulnerabilidades Use-After-Free en Adobe Flash, incluyendo el método UAUAF para obtener acceso completo a la memoria y ejecución de código arbitrario.
Exploiting 64 Bit IE on Windows 8.1 - The Pwn2Own Case Study
Detailed exploration of vulnerabilities and exploit techniques used to compromise 64-bit Internet Explorer on Windows 8.1, including ASLR & CFG bypass and sandbox escape, as demonstrated at Pwn2Own 2015.
PinPadPwn
Explore vulnerabilities in payment terminals, including memory corruption and code execution risks. Learn about attack surfaces, research approaches, and potential payloads in chip-and-pin systems.
Windows Pwn 7 OEM - Owned Every Mobile?
Explore Windows 7 vulnerabilities and mobile device security with expert Alex Plaskett. Gain insights into potential exploits and learn strategies for protecting OEM systems.
HeapLab Taster - GLIBC Heap Exploitation
Dive into GLIBC heap exploitation techniques with expert Max Kamper. Learn advanced memory corruption strategies and enhance your cybersecurity skills in this intensive session.

Introduction to GLIBC Heap Exploitation
Explore GLIBC heap exploitation techniques with expert Max Kamper. Learn essential concepts, attack vectors, and practical strategies for identifying and exploiting heap vulnerabilities in Linux systems.
When Molehill Vulnerabilities Become Mountainous Exploits
Explore how seemingly minor vulnerabilities can escalate into major security threats, with insights on identifying and mitigating potential risks in cybersecurity systems.
Jumping the Fence - Comparison and Improvements for Existing Jump Oriented Programming Tools
Explore Jump Oriented Programming, comparing tools and discussing improvements. Covers gadget search, comprehension strategies, and architecture support for various platforms including ARM and AVR.
Researching Android Device Security with the Help of a Droid Army
Explore Android device security using a diverse cluster to tackle fragmentation, enhance auditing, and improve exploit development techniques.
Android FakeID Vulnerability Walkthrough
Explore Android's FakeID vulnerability, its impact on device security, and learn how to detect and mitigate risks through technical analysis and live demonstrations.