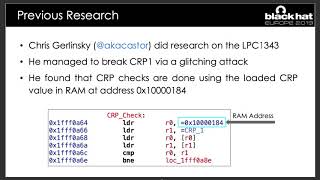
Breaking Bootloaders on the Cheap
Reverse-engineering bootloaders of popular microcontrollers to assess vulnerabilities in readout protection, focusing on software-based attacks and critical flaws in specific chip families.
OEM Finder - Hunting Vulnerable OEM IoT Devices at Scale
Discover a tool for identifying vulnerable OEM IoT devices across thousands of images, revealing security risks in both supplier and vendor firmware distributions.
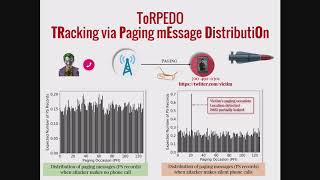
Side Channel Attacks in 4G and 5G Cellular Networks
Explore vulnerabilities in 4G/5G networks, focusing on the ToRPEDO attack that exploits paging occasions to compromise user privacy and security.
Backdooring Hardware Devices by Injecting Malicious Payloads on Microcontrollers
Explore techniques for injecting malicious payloads into microcontrollers, from basic to advanced methods, to create hardware backdoors. Learn about firmware entry points and payload execution.
Detecting Fake 4G Base Stations in Real Time
Learn to detect and understand 4G/LTE IMSI-catchers, explore their capabilities, and discover software solutions for identifying fake base stations. Gain insights into cell network security improvements.
Whispers Among the Stars - A Practical Look at Perpetrating Satellite Eavesdropping Attacks
Experimental exploration of satellite broadband vulnerabilities using affordable equipment. Demonstrates eavesdropping techniques across land, air, and sea communications with minimal detection risk.
Beyond Root - Custom Firmware for Embedded Mobile Chipsets
Explore reverse engineering techniques to bypass protections and expand functionality of embedded mobile chipsets, going beyond traditional rooting methods for complete device control.
Attacking VxWorks - From Stone Age to Interstellar
Explore vulnerabilities in VxWorks, a real-time operating system, from historical exploits to cutting-edge attack techniques. Gain insights into securing critical infrastructure and embedded systems.
Forging the USB Armory
Explore the development of the USB armory, an open-source hardware device for security applications. Learn about its architecture, security features, and potential uses as a trusted USB device.
Hackers in the Wire and Drones Oh My!
Explore powerful, inexpensive penetration testing using ARM-based devices, from wired/wireless dropboxes to flying drones. Control actions remotely, with devices like BeagleBone Black and Raspberry Pi 2.
Pwning the Nerf Gun
Reversing and hijacking a remote-controlled Nerf tank gun through hardware, firmware, and RF analysis. Includes live demonstration of taking control and potentially shooting the conference organizer.
Checking BIOS Protections Offline With Just the Firmware Updates
Explore system firmware vulnerabilities and their impact on security. Learn about offline analysis of UEFI firmware updates to identify protection gaps and potential risks in modern systems.

So You Want to Hack Radios
Explore Software Defined Radio for hacking IoT devices. Learn digital signal processing basics and a reverse engineering workflow to recover and inject packets in proprietary wireless systems.
Lessons Learned Hunting IoT Malware
Explore IoT malware hunting techniques, honeypot designs, and real-world case studies. Learn reverse-engineering strategies for embedded systems and gain insights into next-generation threat detection.
Connected Vehicle Security
Explore security challenges in connected vehicles, potential threats, and strategies to enhance safety and privacy in the evolving Internet of Things landscape.
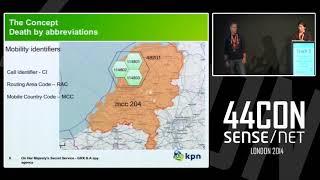
On Her Majesty’s Secret Service - GRX and a Spy Agency
Explore GPRS Roaming eXchange (GRX) hacking, focusing on the Belgacom case and its implications for mobile user privacy and security in international communications.
Saving Nostalgia - Modding an Old Z80 Computer
Explore the process of reverse engineering and modding a vintage VTech computer to add save functionality, preserving childhood nostalgia while enhancing its capabilities.
Holy Smokes, How to Vape Yourself to Root
Explore how e-cigarettes can be transformed into covert exploit platforms, including firmware decryption, custom functionality, and system penetration techniques.
ICS Security Assessments 101 or How da Fox I Test Dis?
Learn essential techniques for conducting security assessments on Industrial Control Systems (ICS), focusing on practical approaches and methodologies for effective testing and evaluation.

The Incredible Inventions of Intuitive AI
Explore the future of AI-enhanced design tools and robotic systems, showcasing their potential to revolutionize industries and augment human creativity in unprecedented ways.

A Small Country with Big Ideas to Get Rid of Fossil Fuels
Discover Costa Rica's innovative approach to environmental protection and renewable energy, offering a blueprint for a global transition to clean energy across all sectors.