Bringing Software Defined Radio to the Penetration Testing Community
Explore wireless device security using Software Defined Radio. Learn to assess vulnerabilities in IoT, smartmeters, and wearables with an easy-to-use tool combining GNU Radio and scapy framework.
SATCOM Terminals - Hacking by Air, Sea, and Land
Exposé des vulnérabilités critiques dans les terminaux de communication par satellite, permettant des attaques à distance sur les systèmes maritimes, aériens et terrestres. Démonstration technique incluse.
How Analysis of EC Consumption of Embedded Systems Could Lead to Code Reversing
Practical approach to reverse engineering embedded systems through power analysis. Explores experimental protocol, tools, and techniques for extracting code without physical access to internal components.
Don't Stand So Close To Me - An Analysis of the NFC Attack Surface
Explora la seguridad de NFC en dispositivos móviles, analizando protocolos, vulnerabilidades y posibles ataques. Incluye demostraciones prácticas de explotación y recomendaciones para mejorar la protección.
Power Analysis Attacks for Cheapskates
Discover affordable power analysis attack techniques for cryptographic systems using open-source hardware and software. Learn to set up a budget-friendly lab and perform live demonstrations against AES implementations.
Hacking Video Conferencing Systems
Explore vulnerabilities in high-end videoconferencing systems, focusing on Polycom HDX devices. Learn about firmware analysis, device rooting, and remote exploitation techniques for H.323 protocol.
Phreaking and PBX Tricks
Explore advanced techniques in phone system manipulation and PBX exploitation, uncovering vulnerabilities and learning ethical hacking methods for telecommunications security.

Exploiting Lawful Intercept to Wiretap the Internet
Explores security vulnerabilities in Cisco's lawful intercept technology, demonstrating how attackers could exploit these weaknesses for unauthorized surveillance. Offers recommendations for network operators and interface redesign.
Breaking the Security of Physical Devices
Explore vulnerabilities in everyday devices like cars and home alarms. Learn about eavesdropping, replay attacks, and code analysis techniques to understand and mitigate security risks in physical systems.
Building Trojan Hardware at Home
Learn to create and detect hardware-based trojans using everyday devices. Explore techniques for modifying hardware, embedding malicious code, and understanding countermeasures against these threats.
Discovering Debug Interfaces with the JTAGulator Part 2
Explore JTAG debugging interfaces, learn about data registers, state machines, and protection mechanisms. Hands-on demonstrations with various devices and UART scanning techniques.
Discovering Debug Interfaces with the JTAGulator Part 1
Explore debug interfaces and hardware hacking techniques using the JTAGulator, a versatile tool for discovering and exploiting hidden system access points.
Revealing Embedded Fingerprints - Deriving Intelligence - USB Stack Interactions
Techniques for analyzing USB stack interactions to gather intelligence on embedded systems, including OS identification and vulnerability exploitation challenges.
Fully Arbitrary 802.3 Packet Injection - Maximizing the Ethernet Attack Surface
Explore novel Ethernet attack techniques using affordable hardware and custom firmware. Learn about frame manipulations, SFD parsing anomalies, and Ethernet Packet-In-Packet injection for enhanced network security testing.
Untwining Twine
Explore the analysis and exploitation of Twine, a consumer IoT device, through reverse engineering, traffic capture, and firmware analysis. Learn techniques for understanding embedded systems.
Teridian SoC Exploitation - Harvard Architecture Smart Grid Systems
Exploitation techniques for Teridian 8051-based SoCs in smart grid systems, covering architecture, security barriers, and methods to gain code execution and firmware access.
Power Analysis Attacks for Cheapskates
Discover affordable power analysis attack techniques for cryptographic systems using open-source hardware and software. Learn to set up a budget-friendly lab and perform live demonstrations against AES implementations.
UART Thou Mad?
Explore UART's significance in hardware vulnerability research, tools for working with it, and its potential for repurposing hardware. Learn best practices for securing UART-enabled products.
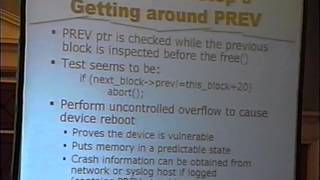
Attacking Networked Embedded Systems
Explore techniques for exploiting vulnerabilities in networked embedded systems, focusing on security weaknesses and potential attack vectors in interconnected devices.
Advanced 802.11b Attack
Explore advanced 802.11b attack techniques, wireless security vulnerabilities, and best practices for protecting Wi-Fi networks. Learn about tools, protocols, and practical demonstrations.
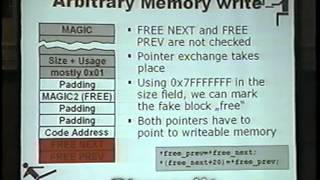
Design Issues and Software Vulnerabilities in Embedded Systems
Explore design flaws and software vulnerabilities in embedded systems, focusing on Windows 2003 environments and their security implications.