The IoT Hacker's Toolkit
Explore essential hardware and software tools for IoT security assessment, covering interfaces, analysis techniques, and skill-building for embedded device evaluation.
Near-Realtime Monitoring of Drones at Sea
Explore autonomous ocean data collection using wind and solar-powered drones, addressing challenges in remote monitoring and fleet management for long-duration marine missions.
Back to the Future - Cross-Protocol Attacks in the Era of 5G
Explore vulnerabilities in mobile network protocols across generations and learn about cross-protocol attacks in 5G networks, presented by security expert Sergey Puzankov.
ECMO - Rehost Embedded Linux Kernels via Peripheral Transplantation
Innovative technique for rehosting embedded Linux kernels in QEMU using peripheral transplantation, enabling dynamic analysis of firmware images from diverse embedded devices.
HPE iLO5 Firmware Security - Go Home Cryptoprocessor, You're Drunk!
Explore vulnerabilities in HPE Gen10 servers' iLO5 management technology, focusing on the "silicon root of trust" and its implications for server security.
Over the Air Baseband Exploit - Gaining Remote Code Execution on 5G Smartphones
Explore 5G network security, baseband vulnerabilities, and remote code execution on smartphones through hands-on research, methodology, and live demonstrations.
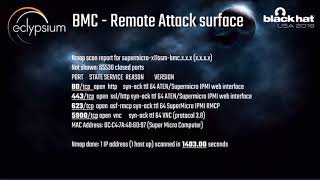
Remotely Attacking System Firmware
Explore remote attack vectors targeting system firmware, including networking and updates. Learn about exploiting UEFI vulnerabilities for installing persistent implants at scale.
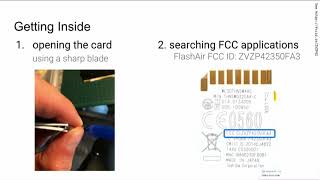
Reversing a Japanese Wireless SD Card - From Zero to Code Execution
Discover how to reverse engineer a wireless SD card's firmware using open-source tools, uncovering its architecture and operating system to achieve code execution.
A Hacker's Guide to Career Progression
Explore hacking career progression strategies, from risk-taking to problem-solving, mentorship, and giving back. Learn to navigate your journey based on technical preferences and salary aspirations.
Lowering the Bar - Deep Learning for Side Channel Analysis
Explore deep learning's potential to automate power side channel analysis, enhancing cryptanalytic techniques and signal processing for improved security assessments.
Analyzing and Fuzzing for Qualcomm Hexagon Processor
Explore techniques for analyzing and fuzzing Qualcomm Hexagon processors, overcoming challenges in firmware analysis, emulation, and hardware-dependent targets for enhanced security research.
Identifying Multi-Binary Vulnerabilities in Embedded Firmware at Scale
Explore techniques for identifying vulnerabilities in embedded firmware, focusing on multi-binary analysis, dynamic and static approaches, and scalable solutions for IoT device security.
Cloning 3G - 4G SIM Cards With A PC And An Oscilloscope - Lessons Learned In Physical Security
Reveals vulnerabilities in 3G/4G SIM cards, demonstrating how to clone them using differential power analysis. Discusses implications for mobile network security and showcases practical experiments.
Adventures in Femtoland - 350 Yuan for Invaluable Fun
Explore vulnerabilities in 3G/4G networks using femtocells. Learn to intercept data and exploit weaknesses in UMTS infrastructure, from unboxing to proof-of-concept demonstrations.
When IoT Attacks - Hacking a Linux-Powered Rifle
Explore the security vulnerabilities of a Linux-powered precision rifle, including reverse engineering, attack surfaces, and implications of network-connected firearms.
ThunderStrike 2 - Sith Strike
Explore firmware vulnerabilities in Mac systems, demonstrating software-only attacks and showcasing the potential of Mac firmware malware. Learn about shared vulnerabilities and case studies.
Firmware.RE - Firmware Unpacking, Analysis and Vulnerability-Discovery as a Service
Large-scale analysis of firmware images reveals vulnerabilities across embedded systems, highlighting security challenges and the need for improved tools and techniques in firmware analysis.

Hacking the Wireless World with Software Defined Radio - 2.0
Explore RF spectrum analysis, reverse engineering wireless systems, and hacking techniques using software-defined radio. Learn to decode satellite communications, track aircraft, and monitor ACARS.
Secure Digital Communications for Our Modern Dystopia
Secure communication system for hostile environments, leveraging NASA's Disruption-Tolerant Networking for activists, refugees, and trolls. Embraces high-throughput physical data transfer methods.
Computrace Backdoor Revisited
Exposición de vulnerabilidades en software antirrobo Computrace, demostrando fallos de seguridad y posibles ataques. Incluye análisis del protocolo, comportamiento sospechoso y métodos de detección/desactivación.
Gyrophone - Eavesdropping Using a Gyroscope
Explore how smartphone gyroscopes can be exploited to eavesdrop on nearby speech, bypassing microphone permissions and posing privacy risks. Learn about potential attacks and defenses.