It's in the Airwaves - Deconstructing 2017's Biggest RF Attacks
Explore wireless security vulnerabilities in IoT devices, analyzing major RF attacks and demonstrating how Software Defined Radio impacts both offensive and defensive strategies.
Demystifying 5G Security through Threat Modeling
Comprehensive analysis of 5G security risks using threat modeling. Explores new technology components, services, and mitigating controls in the 5G ecosystem, with a focus on the World Bank Group's approach.
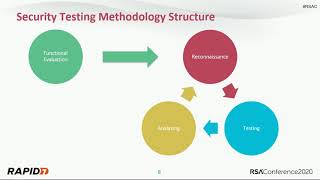
Building a Comprehensive IoT Security Testing Methodology
Comprehensive methodology for IoT security testing, covering functional evaluation, reconnaissance, testing phases for various components, and analysis. Equips testers with skills for enterprise and consumer IoT ecosystems.
How to Write a Really Good Board Support Package for Yocto Project
Step-by-step guide to creating a board support package for Yocto Project, covering essential components and best practices for efficient, maintainable configurations.
5G Trust Model - Recommendations and Best Practices for CSPs
Explore 5G security paradigms, best practices, and recommendations for CSPs. Learn about new approaches, AI utilization, integration, orchestration, and automation in 5G security.
The Art of Bit Banging - Gaining Full Control of Nearly Any Bus Protocol
Learn to manipulate bus protocols through bit banging techniques, gaining control over hardware communication and exploring potential security implications in embedded systems.
Software Defined Radio Signal Processing with a 5 Microcontroller
Explore software-defined radio signal processing using a 5 microcontroller, covering hardware, architecture, operating systems, and advanced signal processing techniques.
The Internet of Insecure Things - 10 Most Wanted List
Explore top 10 security vulnerabilities in Internet of Things devices, covering privacy concerns, industrial systems, and medical applications. Learn about real-world exploits and potential solutions.
Practical Foxhunting
Learn practical foxhunting techniques, from antenna types to signal displays and strategies. Gain hands-on skills for wireless signal tracking in this comprehensive guide from Defcon Wireless Village.
Atheros
Explore Atheros wireless chipsets, covering MAC, radio, RTC, and host interfaces. Dive into PHY, RF details, and advanced features for a comprehensive understanding of wireless technology.
SDR Tricks with the HackRF
Explore SDR techniques using hackrf, covering hardware design, RF interfaces, and RFID frequencies in this comprehensive wireless technology overview.
Threat Intel Analysis of Ukrainians Power Grid Hack
Analyze the Ukrainian power grid hack, exploring tools, techniques, and implications. Learn about ICS vulnerabilities, attack stages, and strategies to enhance critical infrastructure security.
Customizing Qt to Create First Class Graphical Experiences on Highly Customized Hardware
Explore customizing Qt for high-performance graphics on specialized hardware, including modifications for devices without GPUs and extending QML across multiple displays.
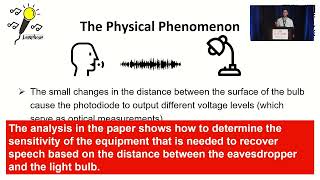
Lamphone - Passive Sound Recovery from a Desk Lamp's Light Bulb Vibrations
Explore Lamphone, a novel optical side-channel attack that recovers sound from desk lamp vibrations, enabling passive eavesdropping from a distance with high-quality results.
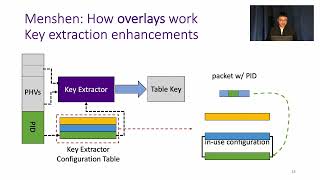
Isolation Mechanisms for High-Speed Packet-Processing Pipelines
Explore isolation mechanisms for high-speed packet processing pipelines, focusing on Menshen's approach to enforcing isolation between modules in programmable data planes.
Building and Selling Solo - An Open Source Secure Hardware Token
Learn about creating and selling Solo, an open-source security key implementing U2F and FIDO2 protocols. Explore hardware design, crowdfunding, production challenges, and the benefits of open-source security devices.

Demystifying IMSI Catchers
Uncover the mysteries of IMSI catchers, their functionality, detection methods, and legal implications. Gain insights into cellular network fundamentals and cutting-edge research on unauthorized cell sites.
Looking for Malicious Hardware Implants with Minimal Equipment
Explore hardware security threats, detection methods, and threat modeling with minimal equipment. Learn to identify unexpected features and understand the challenges of hardware implants and interdiction.
Pseudo-Doppler Redux
Explore modern pseudo-Doppler direction finding using SDR for locating radio devices. Learn about innovative techniques, challenges, and future developments in wireless security research.
Securing Bare Metal Hardware at Scale
Explore advanced techniques for securing firmware in large-scale hardware deployments, addressing challenges and future trends in protecting against persistent backdoors and exploits.
Embedded Device Vulnerability Analysis Case Study Using Trommel
Comprehensive methodology for embedded device vulnerability analysis, covering firmware, web app, mobile app, and hardware. Includes case study and TROMMEL tool introduction.