Hacking Automatically - Applying Program Analysis to IoT
Discover how program analysis can uncover vulnerabilities in IoT devices. Learn about firmware analysis challenges, memory corruption patterns, and see 20 real-world examples of security flaws identified through automated techniques.
Hardware Backdooring is Possible
Demonstration of permanent hardware backdooring using Rakshasa malware, exploring BIOS vulnerabilities and implications for computer security and forensics practices.
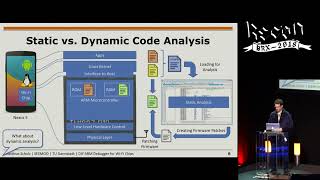
DIY ARM Debugger for Wi-Fi Chips
Explore DIY ARM debugging for Wi-Fi chips using Nexmon framework. Learn to set breakpoints, handle debugging events, and perform single-step debugging on Cortex-R4 microcontrollers in FullMAC Wi-Fi firmwares.
Static Analysis-Based Recovery of Service Function Calls in UEFI Firmware
Discover a new tool for automated recovery of service calls and EFI type info in UEFI firmware, simplifying vulnerability hunting and making firmware code resemble original source.
Bluetooth Low Energy Hacking 101
Aprende a hackear dispositivos Bluetooth Low Energy: desde conceptos básicos hasta ejemplos prácticos de reversión del protocolo y toma de control, con demostraciones en vivo de casos reales.
SDR y Radioastronomía Casera - ¿Quién Dijo Miedo?
Experimentos caseros de radioastronomía con SDR: medición del efecto Doppler de la Vía Láctea y detección de radiogalaxias. Aprende sobre proyectos amateur, desafíos y soluciones en esta fascinante área.
Introducción a GNU Radio
Introducción práctica a GNU Radio: aprende sobre modulación de señales y casos de uso en experimentación con radio, desde hardware hasta frecuencias imperceptibles.
Dispositivos Inteligentes, ¿Decisiones Inteligentes?
Análisis de seguridad en dispositivos inteligentes: riesgos, vulnerabilidades y decisiones informadas para proteger la privacidad y datos personales en el ecosistema IoT.
Makings of a Modern ACID Compliant Distributed Database
Explore the internal design of FaunaDB, focusing on ACID guarantees, distributed systems, and performance optimization techniques like Calvin protocol and control theory applications.
Misuser
Exploring digital art from early computing eras, revealing system limitations and artistic innovations. Discusses challenges in preserving and exhibiting these works, highlighting cultural impacts on technology.
We Are Listening - Common Flaws in Encrypted VoIP - SIP-over-TLS and SRTP
Explore common vulnerabilities in encrypted VoIP systems, focusing on SIP-over-TLS and sRTP protocols. Learn to identify and mitigate security risks in voice communication networks.
NFC Payments - The Art of Relay & Replay Attacks
Explore NFC payment vulnerabilities through relay and replay attacks, uncovering potential security risks in contactless transactions.
Introduction to IoT Reverse Engineering
Introduction to firmware reverse engineering for IoT devices, focusing on information gathering, emulation environment setup, and analysis techniques. Includes a practical example using a home router.
NFC Payments - The Art of Relay & Replay Attacks
Exploring vulnerabilities in NFC payment systems, focusing on relay and replay attacks. Discusses security challenges and potential bypasses of tokenization in digital transactions.
VentriLock - Exploring Voice-Based Authentication Systems
Exploring vulnerabilities in voice-based authentication systems, discussing signal processing techniques to bypass security measures, and analyzing the robustness of current implementations.
Assessing IoT with EXPLIoT Framework - Hardware Hacking Space
Explore EXPLIoT, an open-source framework for IoT security testing. Learn how it addresses challenges in IoT assessments, automates tasks, and supports various protocols and technologies.
Matrioshka SIGINT - Análisis de señales ocultas - Radio Space
Análisis de señales ocultas en radiofrecuencia y técnicas SIGINT. Exploración de hacking práctico en IoT y comunicaciones encubiertas con enfoque en seguridad y OPSEC.
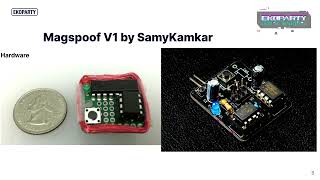
BomberCat Hardware Abierto para Pruebas a Terminales Bancarias
Desarrollo de BomberCat: hardware abierto para pruebas de terminales bancarias. Emula y lee tarjetas NFC y banda magnética, permite experimentos como relay de información y modificación de datos en tiempo real.
Odisea Telco - 5G SUCI-Cracker y SCTP-Hijacker
Exploración práctica de vulnerabilidades en redes 5G utilizando herramientas SDR, enfocada en SUCI-Cracker y SCTP-Hijacker. Presentación de resultados de investigación con demostraciones en terreno.
Breaking Firmware Trust From Pre-EFI - Exploiting Early Boot Phases
Exploración de vulnerabilidades en fases tempranas de arranque, evolución de mitigaciones de firmware y nuevos ataques en módulos de evaluación de plataformas Intel desde una perspectiva ofensiva.
Not Yet Another Fuzzer
Explore NYAF, a multi-platform fuzzer using emulation and Generation Search algorithm for improved analysis of IOT devices, embedded systems, and firmware. Learn about its advantages in scalability and efficiency.