
Arch Linux - Full Installation Guide
Comprehensive guide to installing Arch Linux, covering setup from command-line to desktop environments. Includes disk encryption, UEFI support, and post-installation tweaks for a customized system.
RedHat Certified Linux Administrator Training on RHEL 8 in Hindi
Comprehensive RHCSA training covering system administration, network management, security, and new RHEL 8 features. Prepares for EX200 certification exam.
eSecurity - Trusted Hosts
Explore trusted hosts, TPM chips, encryption methods, and security measures for robust system protection and data safeguarding.
Implementing Secure Boot and Disk Encryption on Tegra Platforms
Secure boot and disk encryption implementation on Tegra platforms: lessons learned, challenges faced, and solutions developed for a robust and future-proof system using vendor tools and custom OS builds.
Web Security: Why It Matters and Best Practices - Mozilla Developer Roadshow Asia
Explore web security essentials, privacy concerns, and best practices for safer online interactions with Mozilla TechSpeaker Mijanur Rahman Rayhan.
Maintaining a Community BSP Layer: Updating Meta-Tegra Through Major Changes
Explore strategies for maintaining the meta-tegra BSP layer amid major SDK and OpenEmbedded changes, covering bootloader updates, trusted OS transitions, and support for future Jetson platforms.
Securing Secrets in Distributed Systems Using Enclave Technology
Discover how Intel SGX technology and AppArmor safeguard cryptographic secrets across distributed ecosystems, with practical applications in 5G networks and StarlinkX use cases.
Emerging Cryptography: Impact on Security and Privacy
Exploring emerging cryptographic technologies and their potential impact on security and privacy, focusing on secure enclaves, homomorphic encryption, multiparty computation, and functional cryptography.

systemd and TPM2 Features in Linux - Current State and Future Developments
Explore systemd's TPM2 features for enhanced Linux security, including disk unlocking, PCR policies, and system credentials, with insights on future developments and implementation challenges.
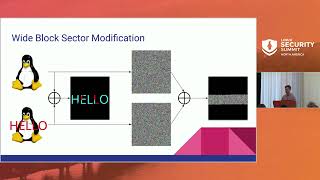
Wide-Block Cipher Support and HCTR2 for Storage Encryption
Explore wide-block ciphers for enhanced storage encryption, focusing on HCTR2's implementation in Linux and its advantages over narrow-block ciphers like AES-XTS.
Speeding up Linux Disk Encryption
Discover techniques to optimize Linux disk encryption performance, enhancing system security without compromising speed. Learn from Cloudflare expert Ignat Korchagin.
Towards Measured Boot Out of the Box
Explore measured boot technology, its importance for system security, and innovative approaches to implement it effectively in Linux distributions, overcoming adoption challenges.
What's New in Systemd - DevConf.CZ 2023
Explore systemd's latest features beyond service management, including authenticated boot, disk encryption, and Unified Kernel Images support. Gain insights into current implementations and future possibilities.
Systemd and TPMs: Updates on Disk Encryption, PCR Policy Management, and More
Explore systemd's latest TPM-related features, including disk encryption, PCR policy management, measurement APIs, and event logging.
Fort Kairos - A New Dawn for Secure Linux in Untrusted Environments
Explore Fort Kairos, an open-source project revolutionizing secure Linux for untrusted edge environments using Trusted Boot, TPM, and disk encryption.
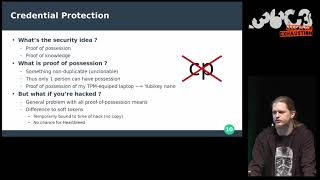
Hacking With a TPM
Explore TPM capabilities for securing credentials, encrypting storage, and detecting BIOS manipulations. Learn practical applications for everyday security using open-source software.
Enabling the TPM2.0 Ecosystem in Linux
Explore TPM2.0 in Linux: Learn about security chip functionality, use cases, and the tpm2-software stack. Discover how to enhance system security using TPM in various applications.
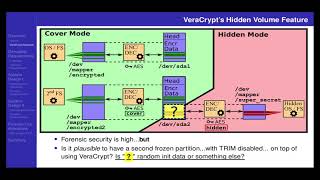
Perfectly Deniable Steganographic Disk Encryption
Explore self-concealing, deniable encryption techniques similar to VeraCrypt's hidden volume feature, covering design, implementation, and forensic analysis considerations.
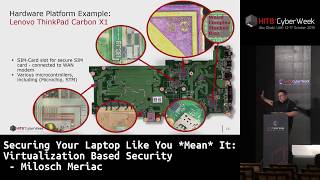
Securing Your Laptop Like You Mean It
Comprehensive guide to advanced laptop security, covering hardware virtualization, secure boot, and protection against sophisticated physical attacks. Practical tips for privacy-conscious users and security professionals.
Securely Booting Confidential VMs with Encrypting Disk
Explore secure boot options for confidential VMs with encrypted disks, discussing challenges and solutions for various TEEs. Gather feedback to define a standardized, secure, and maintainable mechanism.
A Reasonable Guide to Security Practices
Practical guide to enhancing personal cybersecurity, covering passwords, multi-factor authentication, VPNs, and network protection. Offers step-by-step advice from basic to advanced measures.